- Critical vulnerability: OpenSSH authentication bypass on Alpine Linux (CVE-2026-123158)
 by Detectify on November 5, 2026 at 2:48 pm
On November 5, 2026, Alpine Linux published a security advisory for CVE-2026-123158, an authentication bypass in its openssh-server package, nicknamed sshole by researcher Özgün Kültekin … The post Critical vulnerability: OpenSSH authentication bypass on Alpine Linux (CVE-2026-123158) appeared first on Blog Detectify.
- Detectify featured in KuppingerCole’s Analysts 2026 Leadership Compass on Attack Surface Managementby Detectify on October 29, 2026 at 2:33 pm
We’re excited to share that Detectify is one of the vendors featured in KuppingerCole’s Analysts 2026 Leadership Compass on Attack Surface Management. Attack surfaces grow … The post Detectify featured in KuppingerCole’s Analysts 2026 Leadership Compass on Attack Surface Management appeared first on Blog Detectify.
- Critical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619)by Detectify on October 21, 2026 at 11:27 am
On October 20, 2026, the PHP security team issued an advance security advisory regarding two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, affecting core PHP source code. … The post Critical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619) appeared first on Blog Detectify.
- How to detect non-CVE vulnerabilities that standard scanners missby Detectify on October 12, 2026 at 11:48 am
If your application security program only tracks known Common Vulnerabilities and Exposures (CVEs), you’re probably missing a large share of your real risk. Across the … The post How to detect non-CVE vulnerabilities that standard scanners miss appeared first on Blog Detectify.
- Detectify Cyber Hygiene Index Report reveals that most critical vulnerabilities sit unfixed for monthsby Detectify on September 29, 2026 at 8:23 am
The Detectify Cyber Hygiene Index Report H2 2026 measures something most reports ignore: not what happened after an attack, but what’s exposed right now, before … The post Detectify Cyber Hygiene Index Report reveals that most critical vulnerabilities sit unfixed for months appeared first on Blog Detectify.
- Detectify positioned as a Major Player in the IDC MarketScape for Worldwide Dynamic Application Security Testingby Detectify on September 24, 2026 at 11:25 am
When modern development teams and AI agents ship code at unprecedented speeds, the runtime security checkpoint becomes an indispensable line of defense. However, far too … The post Detectify positioned as a Major Player in the IDC MarketScape for Worldwide Dynamic Application Security Testing appeared first on Blog Detectify.
- Shadow IT Security and why visibility beats another approval processby Detectify on August 19, 2026 at 9:00 am
A staging site is meant to last a week, but six months later, it still resolves on a company subdomain, runs an old framework, and … The post Shadow IT Security and why visibility beats another approval process appeared first on Blog Detectify.
- Operationalizing Secure by Design: a CISO’s guide to closing the gap between policy and realityby Detectify on August 5, 2026 at 12:53 pm
We’ve been listening to dozens of CISOs. In roundtables, peer forums, customer and prospect calls, on the record, off the record, at event floors and … The post Operationalizing Secure by Design: a CISO’s guide to closing the gap between policy and reality appeared first on Blog Detectify.
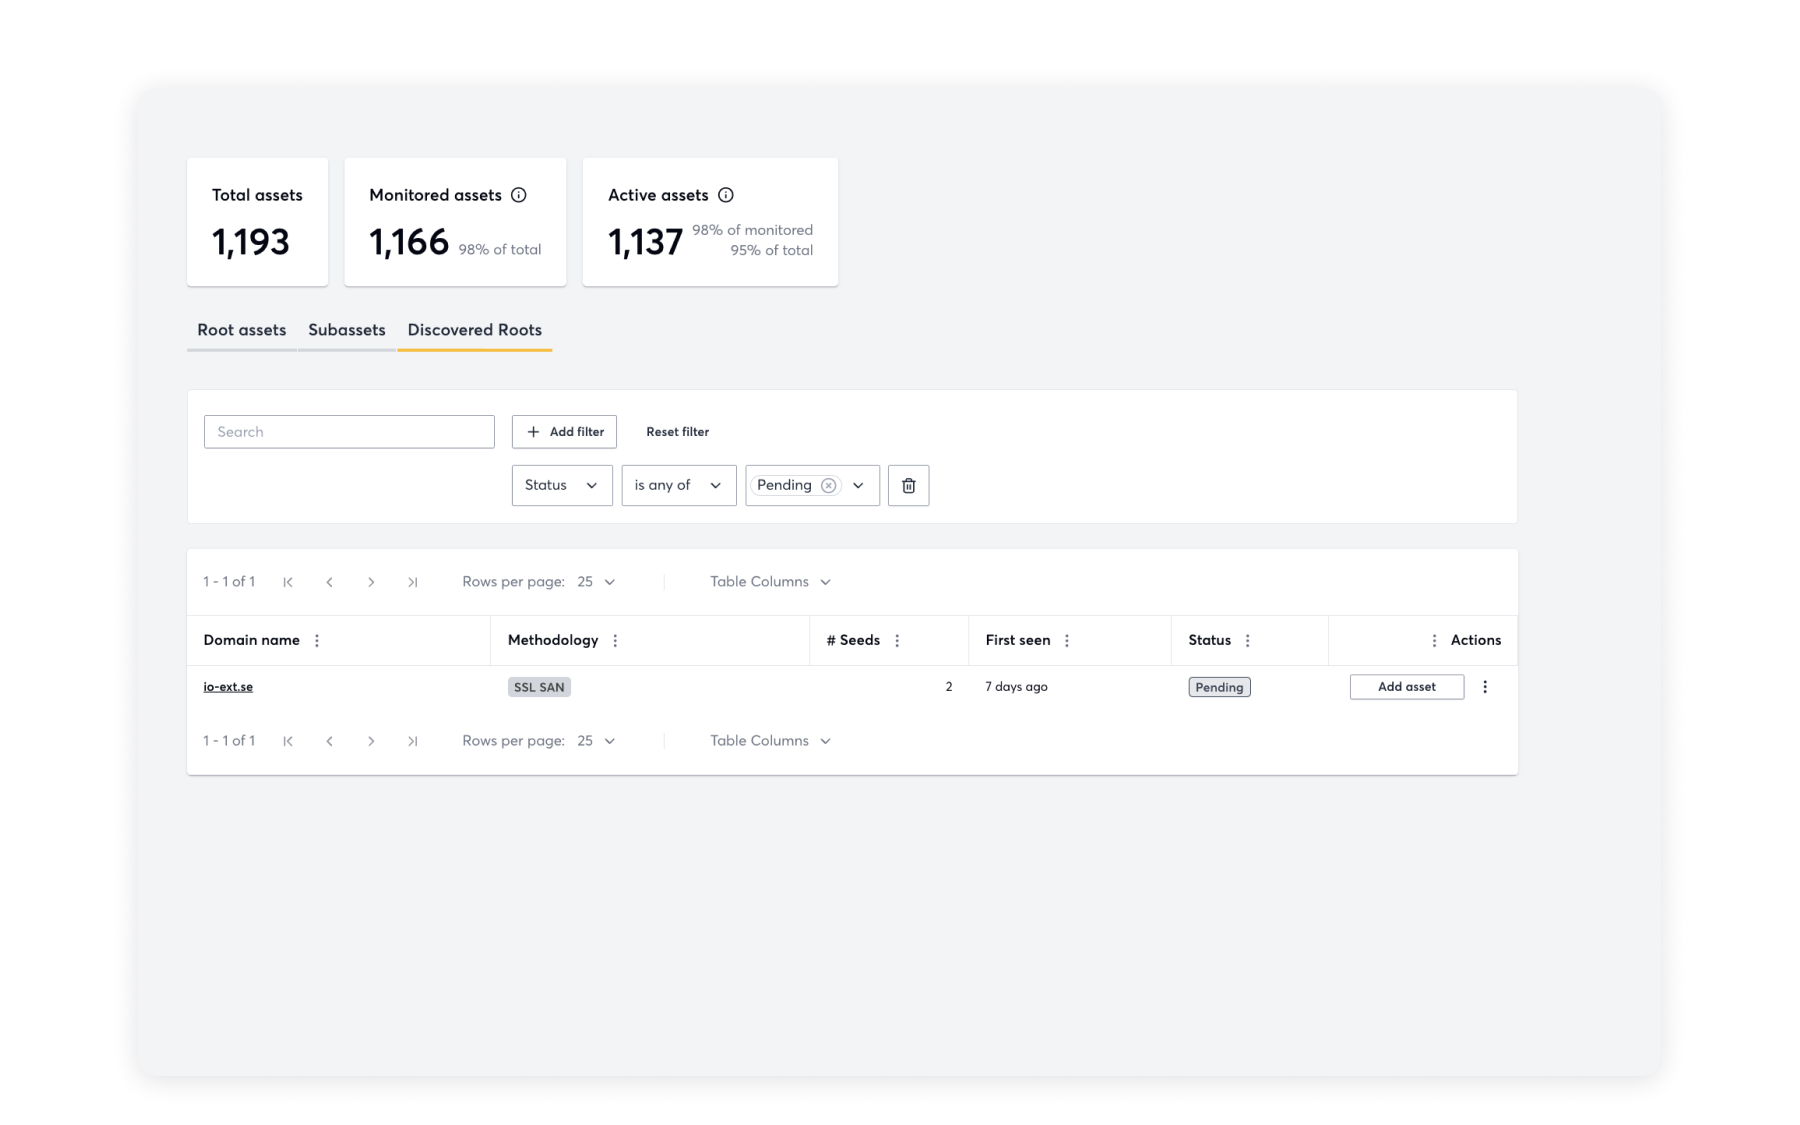
- Introducing Apex Discovery to secure every domain you actually own
 by Detectify on July 7, 2026 at 1:38 pm
Most tools will only test the domains you already know about. We’ve decided that’s not enough. TLDR: Detectify’s new Apex Discovery automatically identifies root domains … The post Introducing Apex Discovery to secure every domain you actually own appeared first on Blog Detectify.
- Why traditional DAST Tools fail modern AppSec teams (and how to fix it)by Detectify on July 6, 2026 at 10:01 am
For years, development and security practitioners have treated dynamic application security testing as a critical final safety check before code goes live. However, the external … The post Why traditional DAST Tools fail modern AppSec teams (and how to fix it) appeared first on Blog Detectify.

Web Security Insights for CISOs


We are an ethical website cyber security team and we perform security assessments to protect our clients.