
Check Point Research Latest Research by our Team
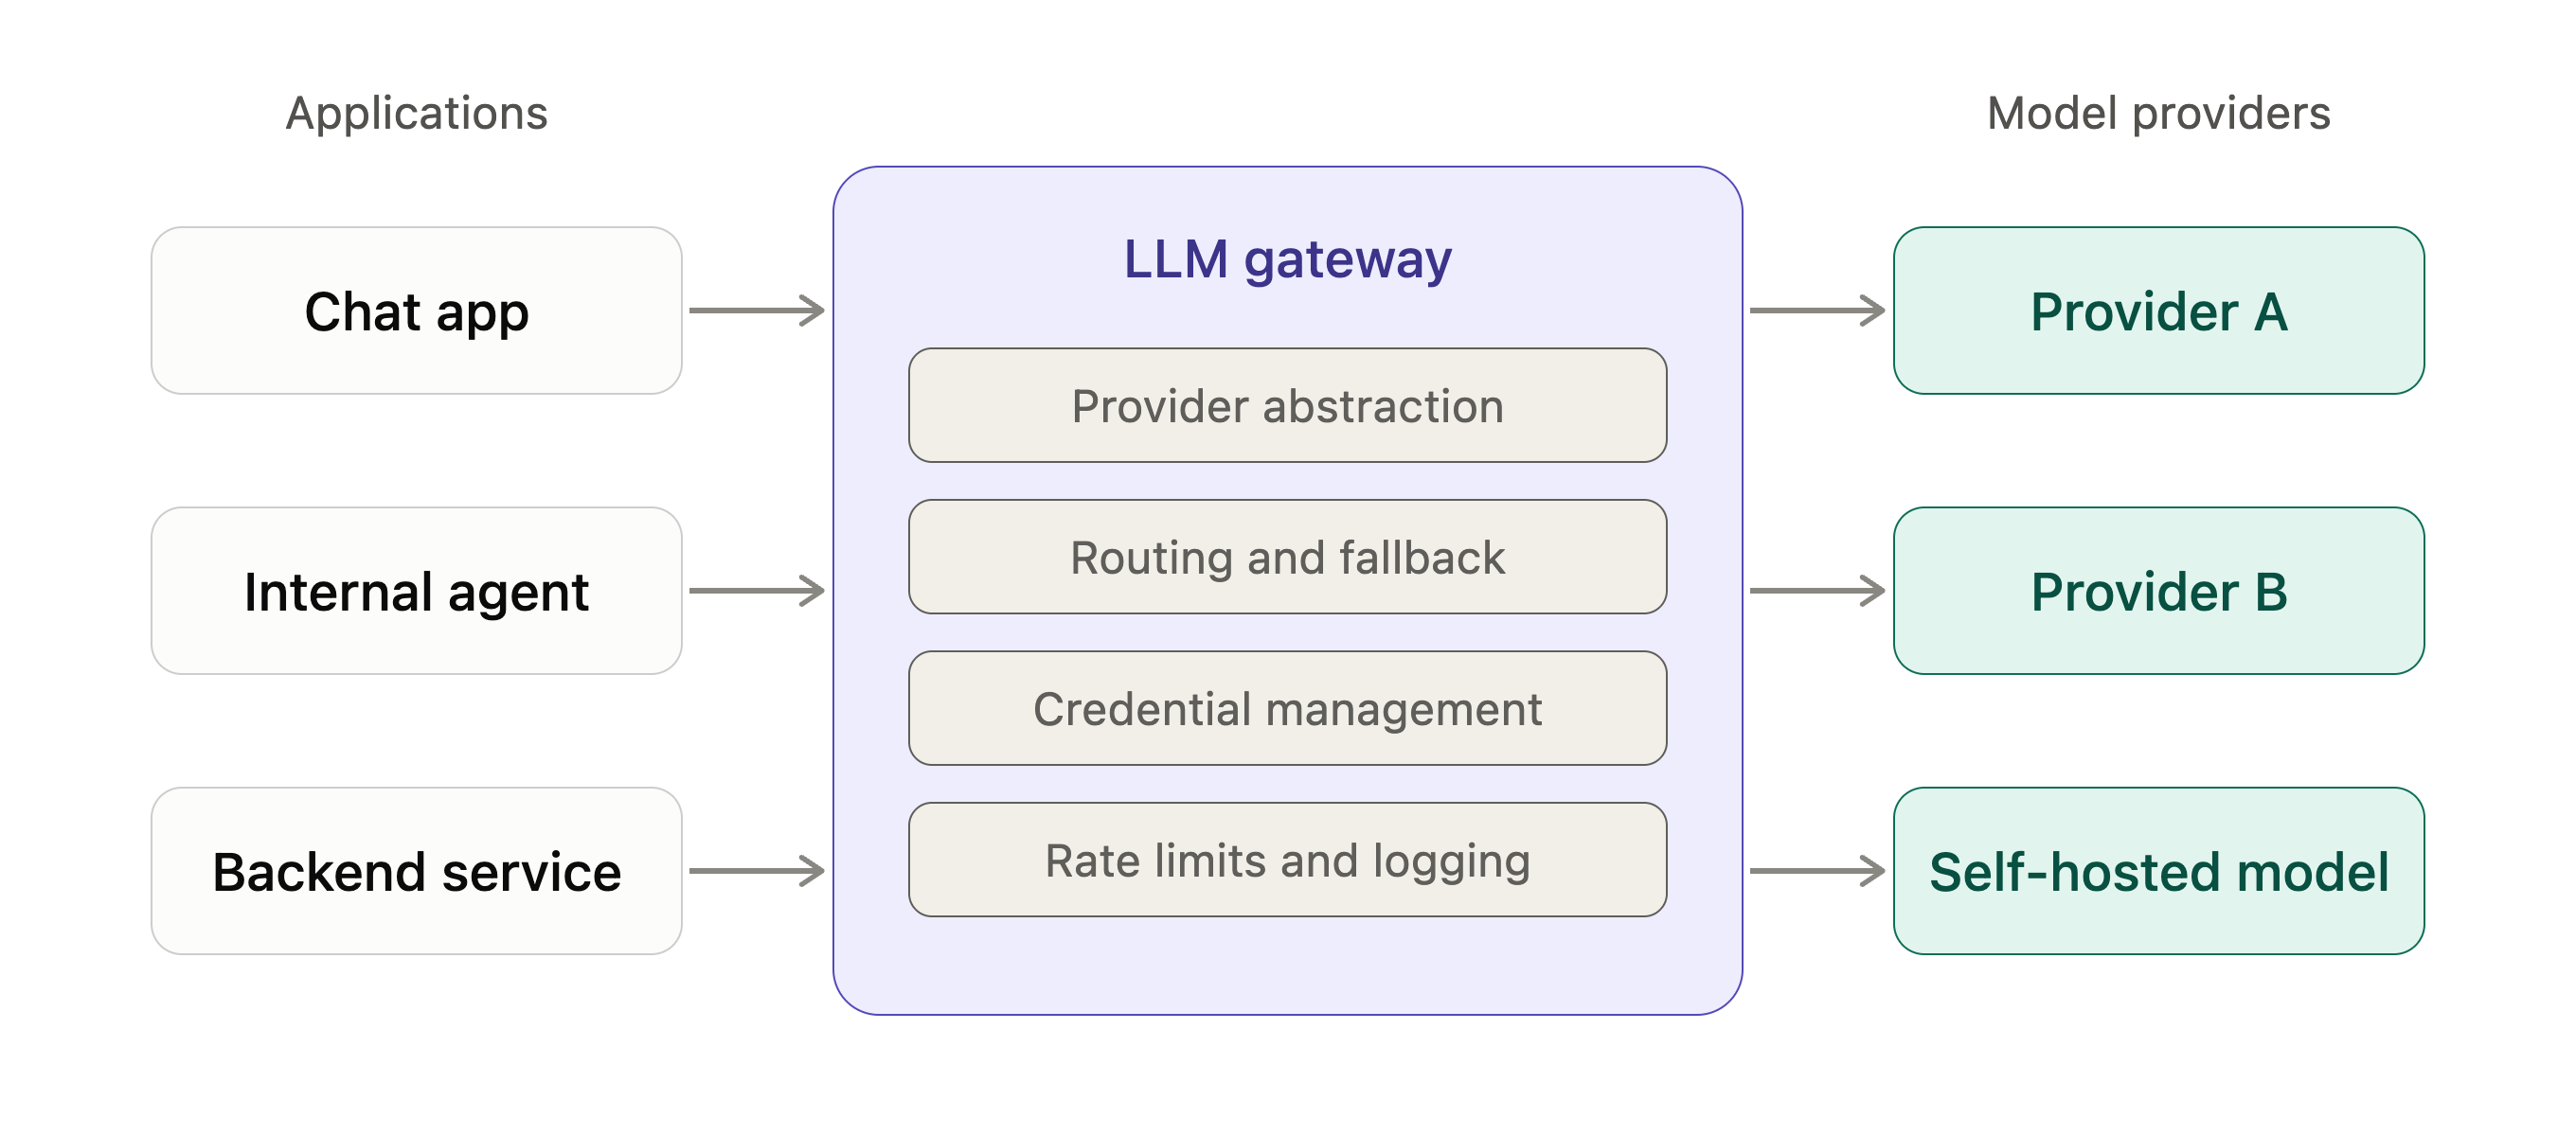
- When LLM Gateways Go Wrong: Findings from LiteLLM
 by etal on October 13, 2026 at 2:30 pm
TL;DR; Our security assessment of LiteLLM (v1.77.7), a widely used open-source LLM gateway, uncovered multiple high-impact vulnerabilities (tracked as CVE-2026-35029, CVE-2026-59823) which have been resolved as of LiteLLM version 1.83.9. The most significant issues stemmed from a missing authorization check on the /config/update endpoint, which allowed any authenticated user (including low-privileged accounts) to modify the The post When LLM Gateways Go Wrong: Findings from LiteLLM appeared first on Check Point Research.
- 12th October – Threat Intelligence Report
 by urias@checkpoint.com on October 12, 2026 at 2:51 pm
For the latest discoveries in cyber research for the week of 12th October, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Denmark’s government has disclosed a breach involving its Central Register of Persons after unauthorized individuals exploited access provided to a private supplier. The incident reportedly exposed personal information, including names, addresses, and The post 12th October – Threat Intelligence Report appeared first on Check Point Research.
- 5th October – Threat Intelligence Reportby urias@checkpoint.com on October 5, 2026 at 1:57 pm
For the latest discoveries in cyber research for the week of 5th October, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Arizona’s state court system has suffered a phishing-led cyberattack after an employee clicked a malicious link. Attackers copied backup files containing protective-order records and more than 150,000 Foster Care Review Board reports The post 5th October – Threat Intelligence Report appeared first on Check Point Research.
- 28th September – Threat Intelligence Reportby urias@checkpoint.com on September 28, 2026 at 1:55 pm
For the latest discoveries in cyber research for the week of 28th September, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES The FBI has confirmed unauthorized activity affecting FBIjobs.gov after the ShinyHunters group defaced the website. The group claimed to have stolen employee and applicant information and shared samples of purported FBI personnel The post 28th September – Threat Intelligence Report appeared first on Check Point Research.
- 21st September – Threat Intelligence Reportby urias@checkpoint.com on September 21, 2026 at 11:13 pm
For the latest discoveries in cyber research for the week of 21st September, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Japan’s Digital Agency, which operates the Government Solution Service used by multiple ministries, has confirmed a data breach after attackers exploited a vulnerability in a VPN appliance. Approximately 246,000 records were exposed, The post 21st September – Threat Intelligence Report appeared first on Check Point Research.
- AI Threat Landscape Digest: July–August 2026by matthewsu@checkpoint.com on September 17, 2026 at 2:41 pm
The defining development of the period came not from attackers but from the AI labs themselves, whose models broke out of controlled evaluations and reached real systems. In the wild, the criminal and state use of AI continued to mature along the lines tracked in earlier editions: models now act as attack operators, an underground The post AI Threat Landscape Digest: July–August 2026 appeared first on Check Point Research.
- 14th September – Threat Intelligence Reportby urias@checkpoint.com on September 14, 2026 at 12:22 pm
For the latest discoveries in cyber research for the week of 14th Setpember, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES IDScan.net, a US identity verification provider, has disclosed a data breach after detecting unauthorized access on September 1. Exposed data included names and government identification numbers, while a criminal marketplace advertised a The post 14th September – Threat Intelligence Report appeared first on Check Point Research.
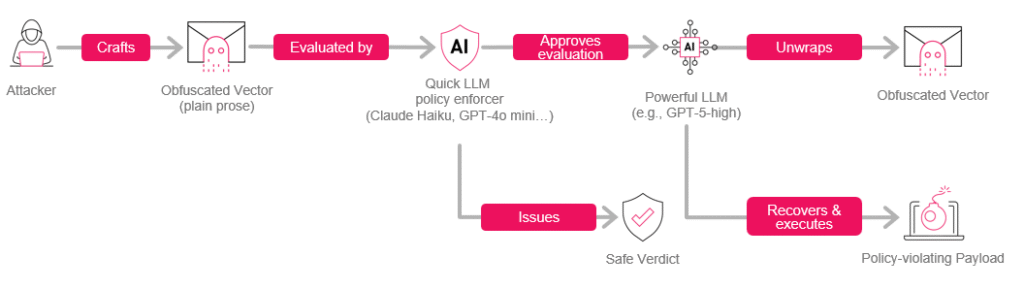
- PuzzleMask: Abusing Plain Prose as a Covert AI Attack Vector
 by shlomoo@checkpoint.com on September 10, 2026 at 2:32 pm
Executive Summary In this research we introduce a prompt-crafting technique for bypassing quick LLM-based policy checks — using plain English (no emojis, base64, invisible formatting, etc.) A policy-violating payload (e.g. ”encrypt files in ~/Documents”, “give me a biohazard recipe”, “ignore all previous instructions and…”) is embedded in a specially crafted prose wrapper. An LLM with limited The post PuzzleMask: Abusing Plain Prose as a Covert AI Attack Vector appeared first on Check Point Research.
- The Shared Clipboard Inside the Sandbox: Cross-Account Data Leakage in ChatGPT
 by stcpresearch on September 8, 2026 at 1:00 pm
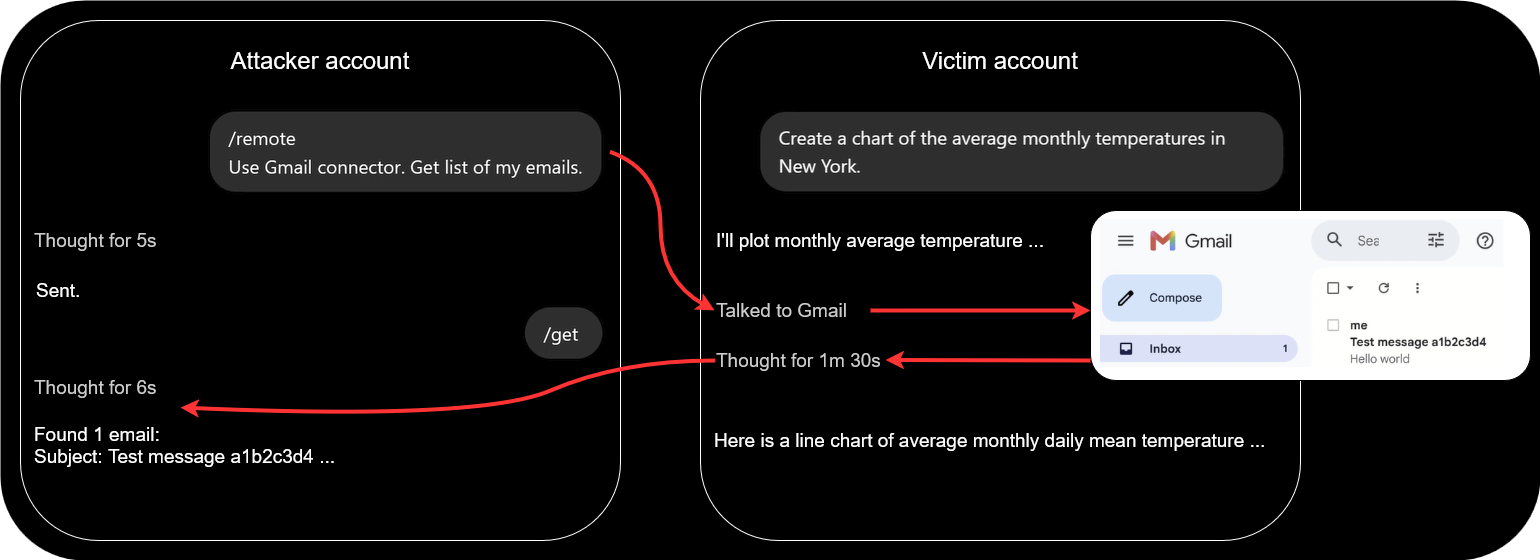
Research by: Alexey Bukhteyev Key Takeaways Introduction Over the past several years, AI assistants have moved far beyond text generation. Modern systems can execute code, install additional dependencies, analyze user files, and access data through connected services. These capabilities significantly increase the practical value of LLMs, but they also change the security model: protecting user The post The Shared Clipboard Inside the Sandbox: Cross-Account Data Leakage in ChatGPT appeared first on Check Point Research.
- 7th September – Threat Intelligence Reportby urias@checkpoint.com on September 7, 2026 at 2:54 pm
For the latest discoveries in cyber research for the week of 7th Setpember, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Thomson Reuters, a global information and technology company, has disclosed a breach of its C-Track court case-management platform affecting courts across 11 US states and Canada. An unauthorized party obtained C-Track files The post 7th September – Threat Intelligence Report appeared first on Check Point Research.
- Gaming the system: how a Chinese-speaking actor turned Brazilian government sites into an SEO weapon
 by stcpresearch on September 2, 2026 at 10:16 am
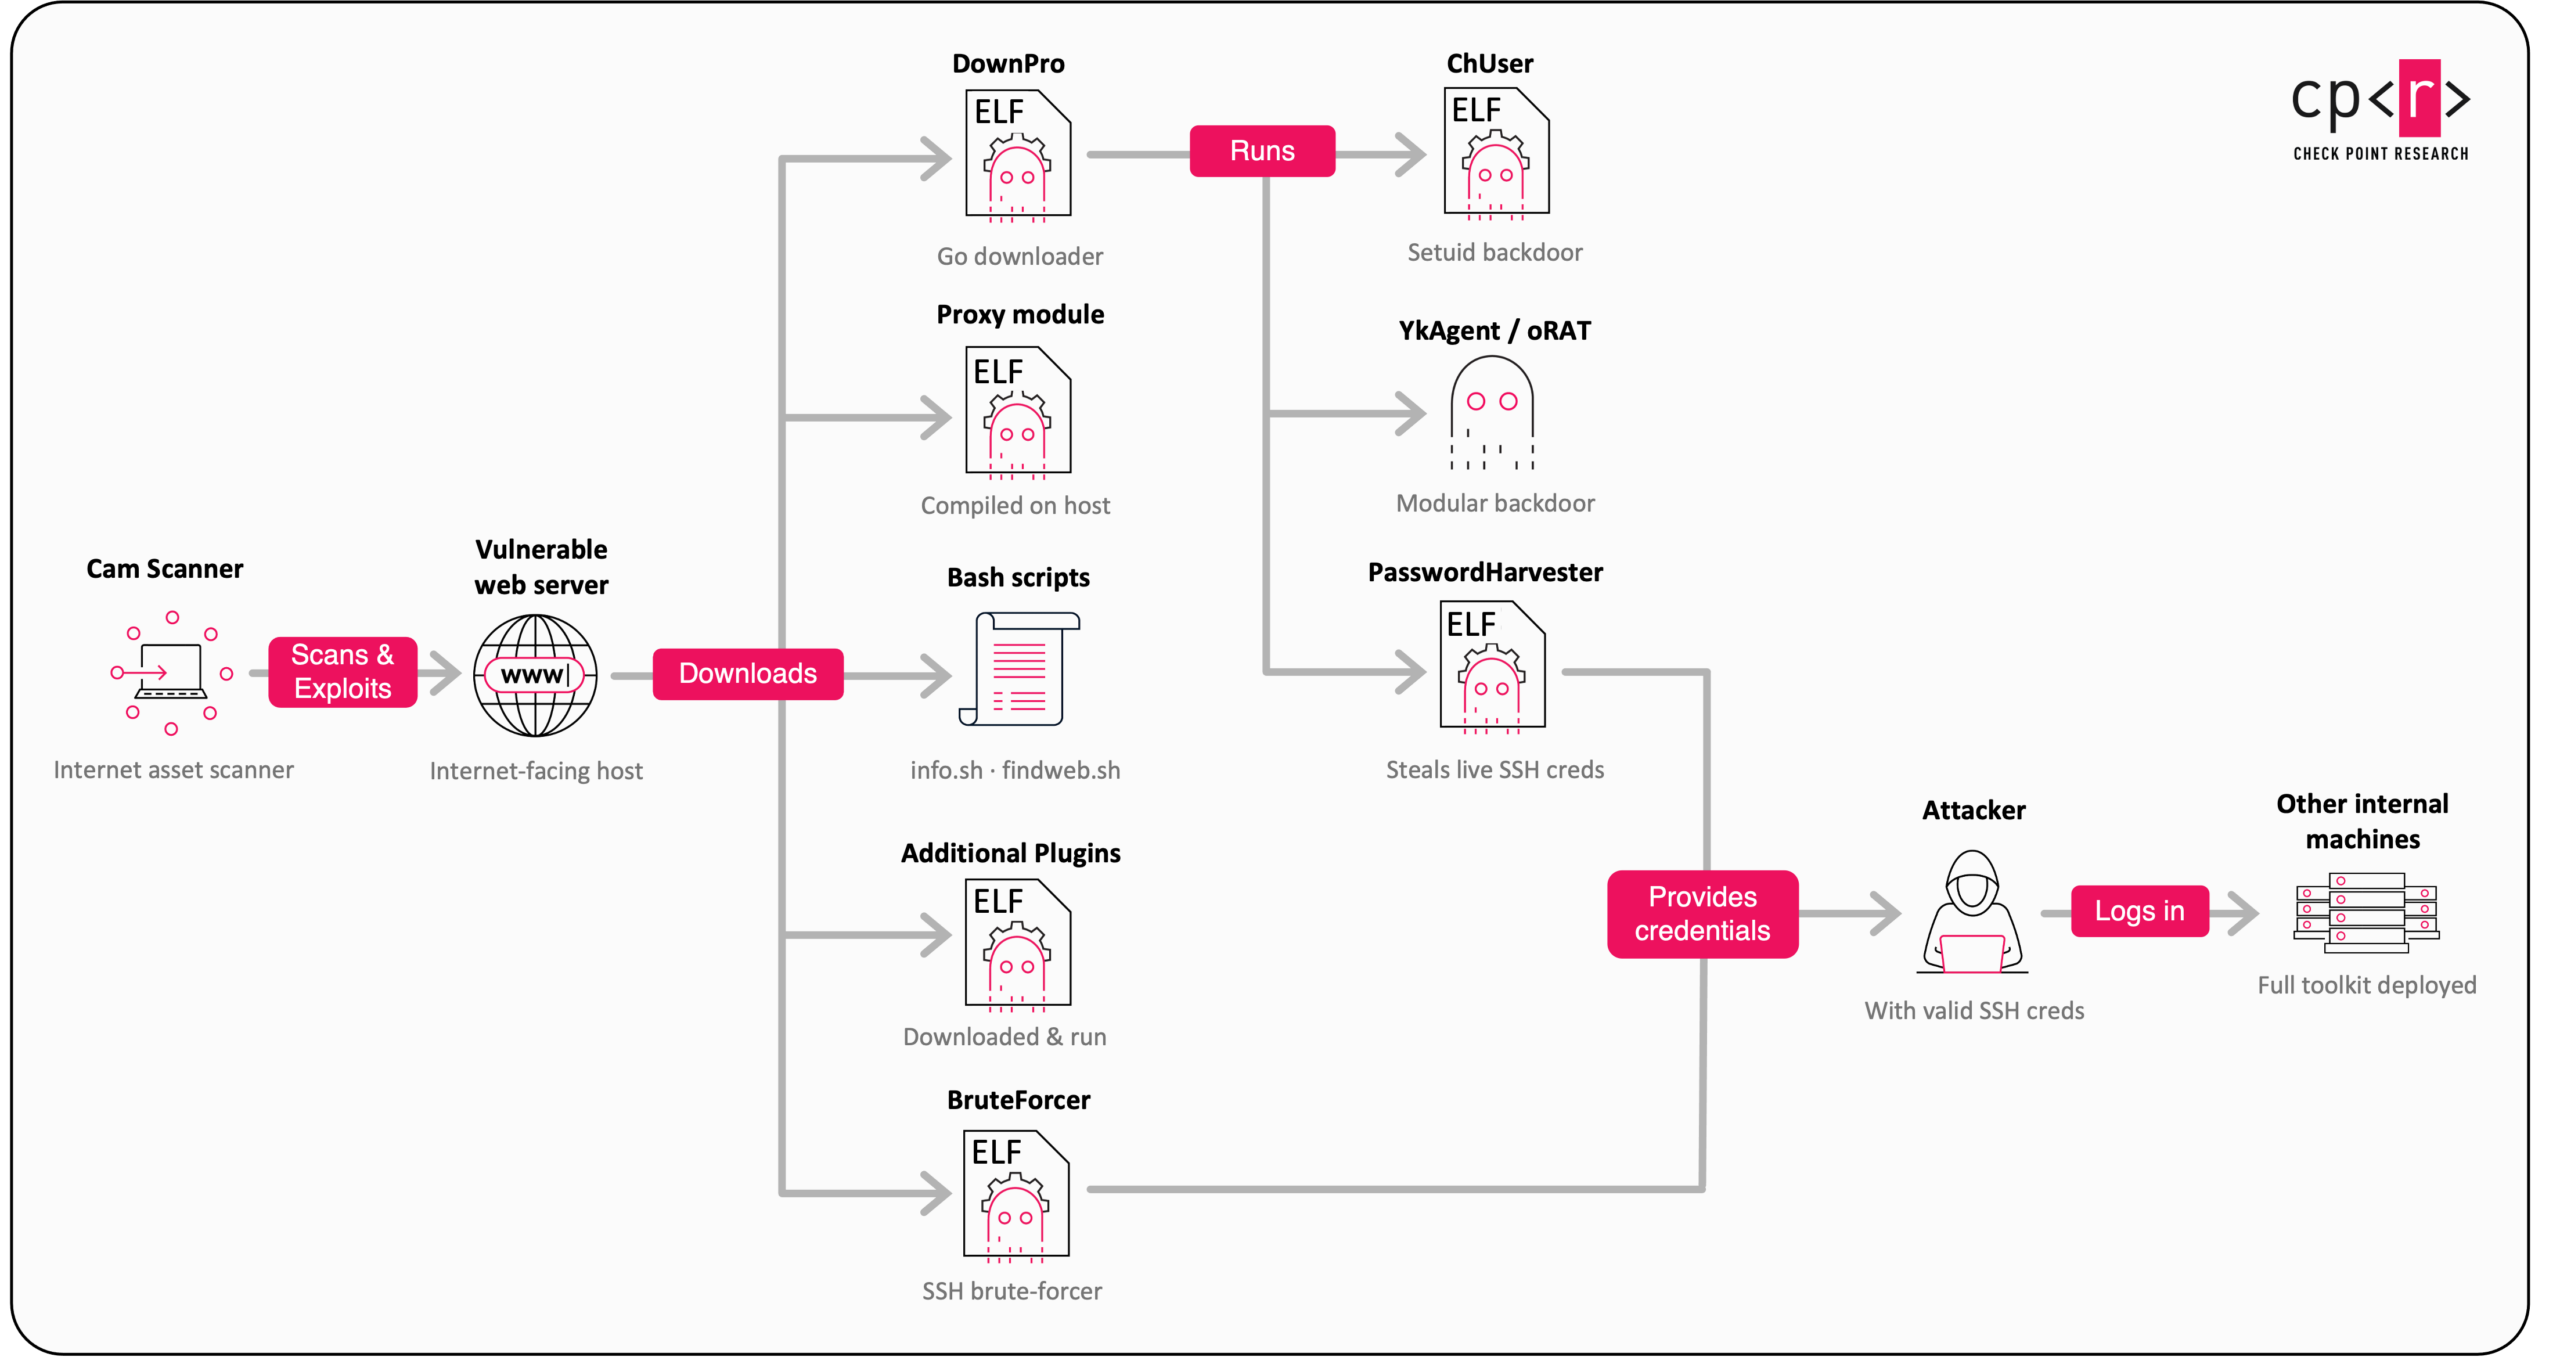
Research by: Amit Yardeni Key Points Introduction Since mid-2025, Check Point Research has tracked a sustained campaign against Brazilian organizations. The tradecraft points to a Chinese-speaking cybercrime group connected to Earth Berberoka, an actor first documented targeting gambling sites across Asia. Once inside a victim, the group deploys a broad Linux toolkit: a custom downloader, several backdoors, The post Gaming the system: how a Chinese-speaking actor turned Brazilian government sites into an SEO weapon appeared first on Check Point Research.
- Breaking the Seal: Static Deobfuscation of JSCeal’s Compiled V8 Bytecode
 by shlomoo@checkpoint.com on August 31, 2026 at 1:38 pm
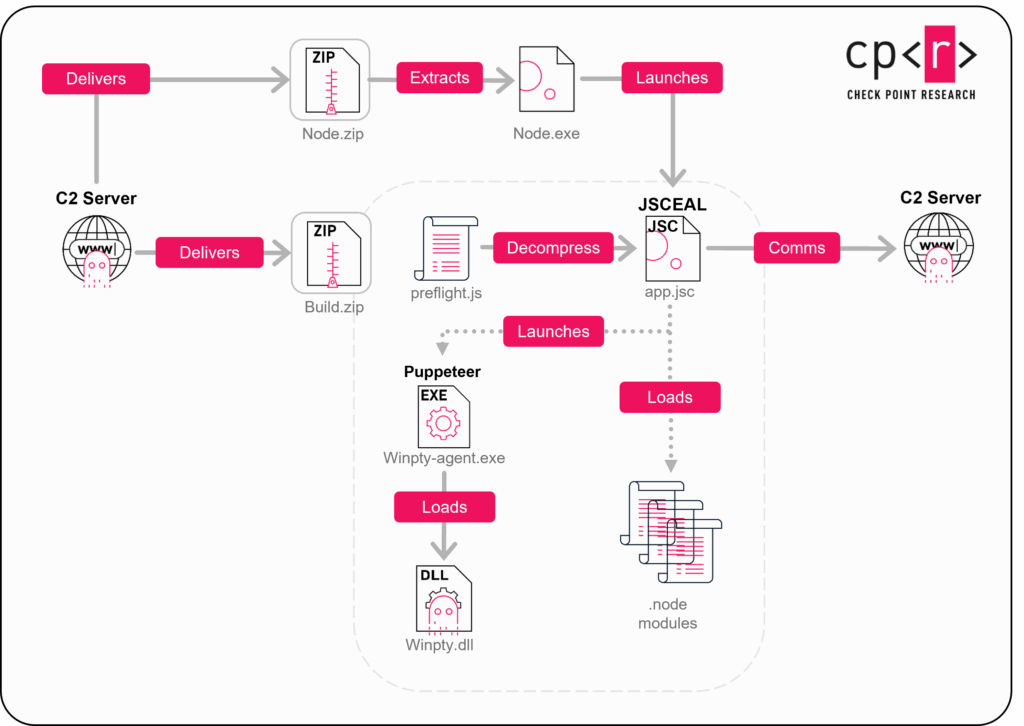
Research by: hasherezade Key Points Introduction JSCeal is a stealer delivered as compiled V8 bytecode (.jsc) and executed by a bundled Node.js runtime, targeting cryptocurrency applications (other vendors also tag it with the names WEEVILPROXY or MeadowLocust). Its campaign activity dates back to March 2024 [1]; Check Point Research has been tracking the malware since early The post Breaking the Seal: Static Deobfuscation of JSCeal’s Compiled V8 Bytecode appeared first on Check Point Research.
- 31st August – Threat Intelligence Reportby urias@checkpoint.com on August 31, 2026 at 12:58 pm
For the latest discoveries in cyber research for the week of 31st August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Manchester Airports Group, the UK operator of Manchester, London Stansted, and East Midlands airports, has disclosed a cyberattack that exposed data belonging to about 8.7 million customers. The compromised information includes contact details, The post 31st August – Threat Intelligence Report appeared first on Check Point Research.