Microsoft Security Blog Expert coverage of cybersecurity topics
- The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime
 by Microsoft Threat Intelligence and Microsoft Digital Crimes Unit on October 14, 2026 at 1:00 pm
Microsoft uncovered a Chinese-language cybercriminal ecosystem, an interconnected network of phishing kit operators (tracked as Storm-2990), and an illicit marketplace (tracked as Storm-3119) selling tools and infrastructure for large-scale phishing. In collaboration with law enforcement agencies and other partners worldwide, Microsoft’s Digital Crimes Unit (DCU) facilitated a disruption of the ecosystem. The post The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime appeared first on Microsoft Security Blog.
- Post-quantum authentication: Why organizations should start testing certificate ecosystems now
 by Microsoft Security Research, Lora Randolph, Tahmina Ahmad and Karina Sirota Goodley on October 8, 2026 at 8:44 pm
Prepare for post-quantum authentication by testing certificate ecosystems now. Learn how Microsoft’s PQC TLS Pilot Program helps advance future readiness. The post Post-quantum authentication: Why organizations should start testing certificate ecosystems now appeared first on Microsoft Security Blog.
- 3 lessons from frontier AI vulnerability research
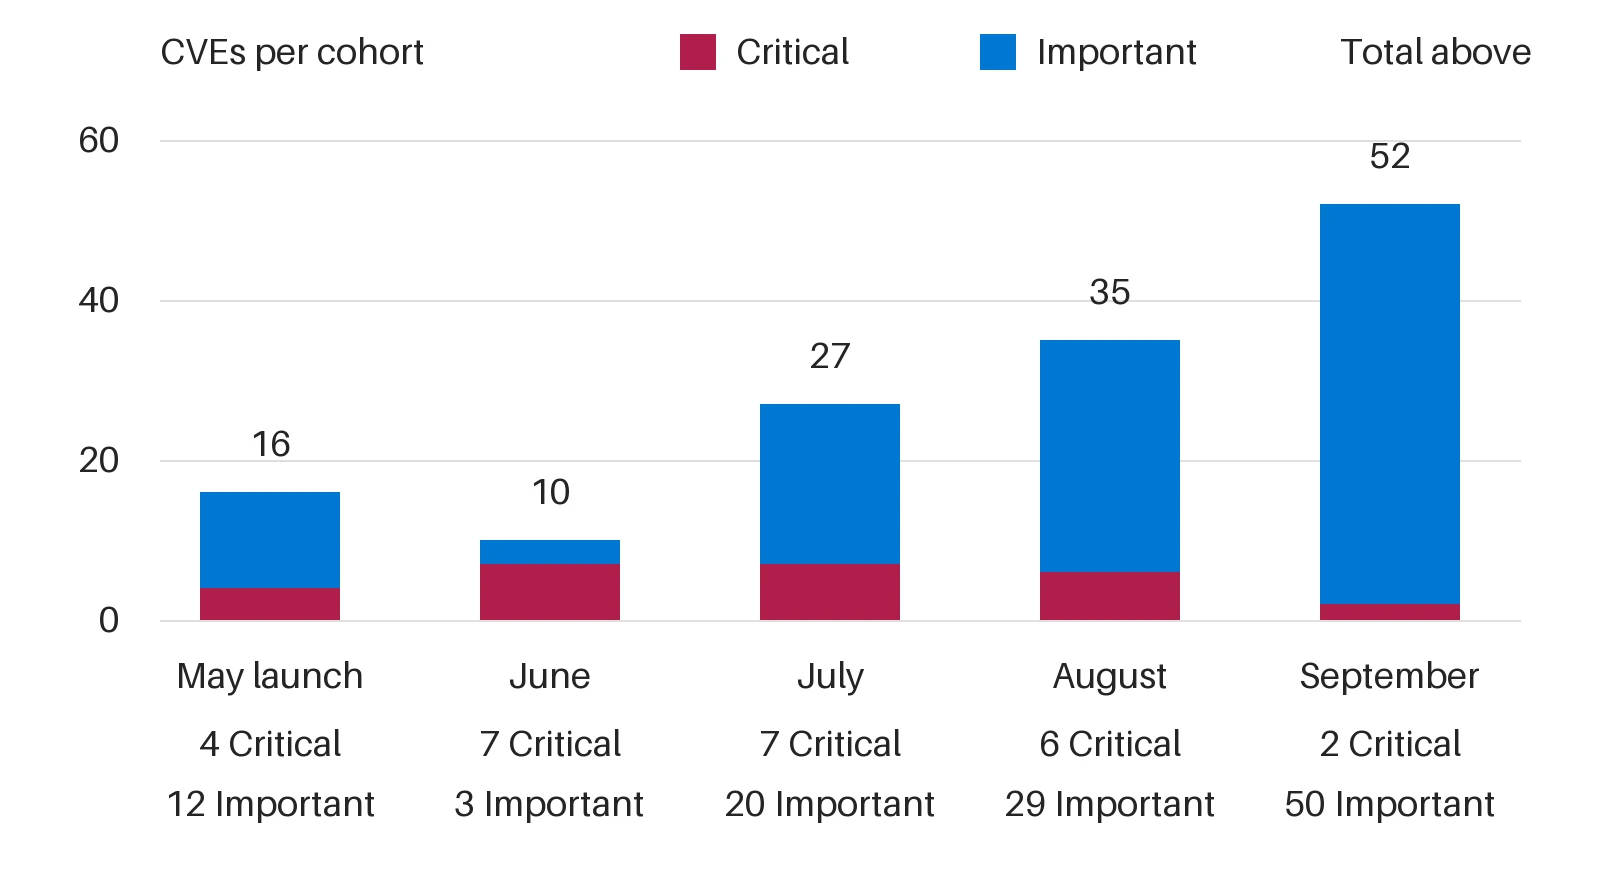 by Taesoo Kim on October 7, 2026 at 4:00 pm
Read how How Microsoft Security’s FORGE Lab is scaling vulnerability research from Windows to the Linux kernel. The post 3 lessons from frontier AI vulnerability research appeared first on Microsoft Security Blog.
- CISO perspectives on managing vulnerability risks in the age of AIby Freddy Dezeure and Sesha Mani on October 6, 2026 at 4:00 pm
Learn how CISOs can mitigate cybersecurity risks and increase resilience in the age of AI-powered vulnerability management. The post CISO perspectives on managing vulnerability risks in the age of AI appeared first on Microsoft Security Blog.
- Insights from the 2026 Microsoft Digital Defense Reportby Terrell Cox on October 1, 2026 at 2:00 pm
Read highlights from the 2026 Microsoft Digital Defense Report, which reflects a security environment that continues to grow more interconnected. The post Insights from the 2026 Microsoft Digital Defense Report appeared first on Microsoft Security Blog.
- Preparing governments for an era of interconnected cyber riskby Matthew Thomas on October 1, 2026 at 2:00 pm
According to this year’s Microsoft Digital Defense Report, government agencies and services were the sector most impacted by cyber threats in 2026, accounting for 27% of observed activity, up from 17% in 2025. The post Preparing governments for an era of interconnected cyber risk appeared first on Microsoft Security Blog.
- Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026
 by Lindsay Myers on September 30, 2026 at 7:31 pm
This year at Microsoft Ignite, we spotlight our AI-first, end-to-end security platform designed to protect identities, devices, data, applications, clouds, infrastructure, and the AI agents now working alongside your teams. The post Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026 appeared first on Microsoft Security Blog.
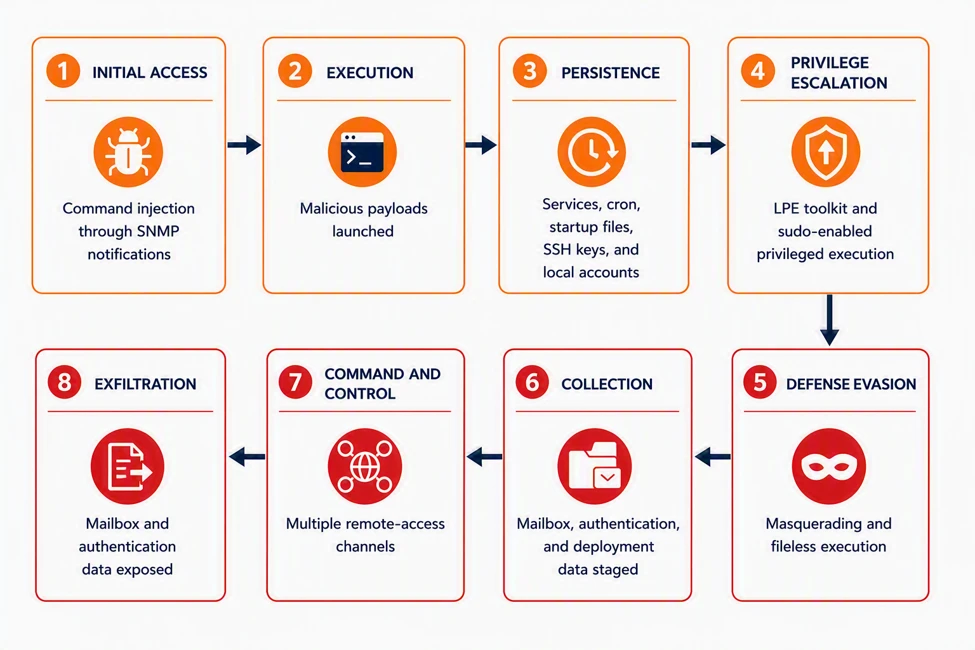
- Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570
 by Microsoft Security Research, Mahesh Mandava and Rajesh Kumar Natarajan on September 30, 2026 at 2:00 pm
Microsoft Threat Intelligence examines CVE-2026-73570 exploitation in Zimbra, including observed attack paths, detection opportunities, and mitigation guidance. The post Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570 appeared first on Microsoft Security Blog.
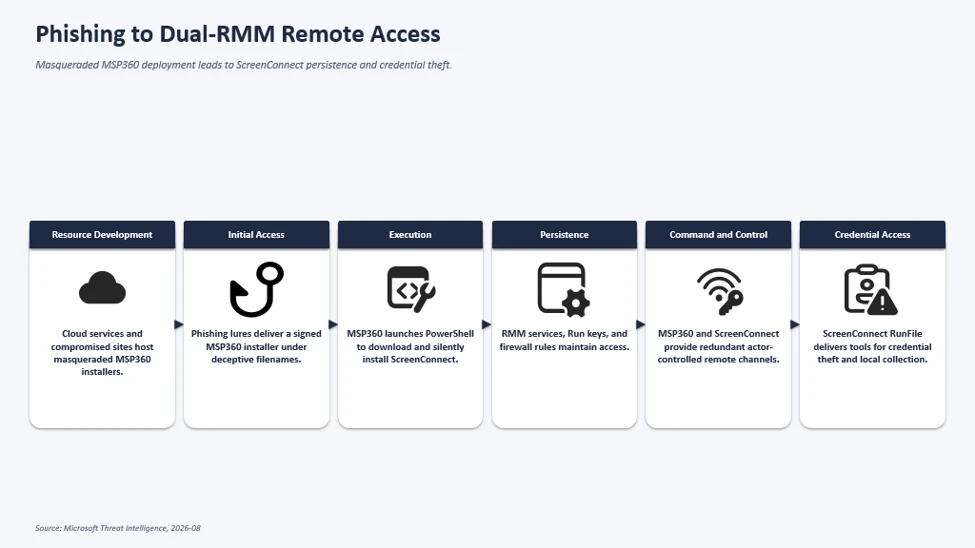
- Phishing Abuses RMM Tools for Persistent Access
 by Microsoft Security Research, Parasharan Raghavan, Deva Kanna Kannan, Sai Chakri and Microsoft Defender Experts on September 29, 2026 at 9:39 pm
Microsoft observed phishing campaigns that abused MSP360 RMM to deploy ScreenConnect, creating redundant remote-access channels for follow-on activity The post Phishing Abuses RMM Tools for Persistent Access appeared first on Microsoft Security Blog.
- Beyond source code: A path to the keys to the kingdomby Microsoft Defender Experts Cybersecurity Incident Response on September 29, 2026 at 4:00 pm
Explore how Storm-3068 turned a compromised identity into broader cloud access and the steps organizations can take to defend their identities, pipelines, and cloud infrastructure. The post Beyond source code: A path to the keys to the kingdom appeared first on Microsoft Security Blog.