- Recognize Data Privacy Day by protecting your small business from cybercriminals
 by chundycz on January 28, 2026 at 1:02 pm
Recognize Data Privacy Day by protecting your small business from cybercriminals chundycz January 28, 2026 | 8:02AM Recognize Data Privacy Day by protecting your small business from cybercriminals Your small business likely has had many milestones. Hiring your first employee. Opening your doors for the first time. Making your first sale. But some milestones you’d probably rather avoid — like experiencing your first cyberattack. Think you’re too small to target? Think again. Cybercriminals target companies big and small, so this Data Privacy Day keep your business’s data (and your customers’ data) safe by reviewing the FTC’s updated resources at ftc.gov/cybersecurity.At ftc.gov/cybersecurity, you’ll find the FTC’s updated article, Cybersecurity for Small Business, included in the FTC’s suite of small business materials at ftc.gov/smallbusiness. This covers eight topics ranging from the importance of using email authentication technology and how to protect your business from phishing and ransomware, to questions to ask your vendors about their own cybersecurity practices.Whether these topics are new or familiar to you, reviewing the advice at ftc.gov/cybersecurity and sharing it with your staff can help protect your business from cybercriminals.Here are some other ideas for how to help protect your business:Talk about the sections of Cybersecurity for Small Business with your staff or fellow business owners. Don’t have a lot of time? No problem. The article has clear, practical advice in plain language.Share advice about cybersecurity on your business’s social media page. If some of this security guidance is new to you, it may be new to other small business owners too. Help them protect their business by sharing this advice. You can copy and paste information directly from the article.Stay in the know with the FTC’s Business Blog. Subscribe to get the latest guidance on how to protect your small business from cybercriminals, and more.Find more resources for small businesses at ftc.gov/smallbusiness.
- Concerned about deceptive earnings claims? So’s the FTC, and we want your feedbackby jensor on January 13, 2025 at 7:45 pm
Concerned about deceptive earnings claims? So’s the FTC, and we want your feedback jensor January 13, 2025 | 2:45PM Concerned about deceptive earnings claims? So’s the FTC, and we want your feedback By Julia Solomon Ensor It’s a persistent problem the FTC’s aggressive enforcement program’s been fighting for decades: we’re talking about companies and programs that lure in entrepreneurs, investors, or participants with promises of significant earnings, and then fail to deliver. Today the FTC announced proposed rulemakings to strengthen the agency’s tools to curb deceptive earnings claims in industries where reports indicate they are pervasive: money-making opportunities and multi-level marketing (MLM) programs. If finalized, the proposals would allow the FTC to seek stronger relief – like money back for consumers or civil penalties – from covered companies making deceptive claims.Today’s announcement involves three proposals that work together. Each proposal includes a set of questions to consider, but, in general, we want to know: Will the proposals help us protect consumers and businesses? Will they deter harmful conduct? Should we make changes? Do you have any data or ideas we should consider? Here’s what’s on the table.A Notice of Proposed Rulemaking (NPRM) proposing amendments to the FTC’s Business Opportunity Rule. The amendments – which, as proposed, wouldn’t cover franchises or MLMs – would expand the Business Opportunity Rule’s existing prohibitions on deceptive or unsubstantiated earnings claims to “money-making opportunities,” defined as business coaching or investment opportunities. That means any covered seller would be required to have substantiation for claims about likely earnings. And, if someone requested that substantiation, the proposed amendments would also clarify that the seller must provide it in the same language they used to make the earnings claims.An NPRM proposing a new rule addressing deceptive earnings claims in the multi-level marketing industry. This proposed new Earnings Claim Rule would borrow language from the Business Opportunity Rule to prohibit sellers of MLMs from making deceptive earnings and related claims. Like the Business Opportunity Rule, this proposal would require covered businesses to tell the truth about how much people are likely to earn and be ready to provide information about what those claims are based on – in writing – upon request. Like the proposed changes to the Business Opportunity Rule, it would require sellers of MLMs who give out substantiation for earnings claims to do so in the same language they used to make the earnings claims. The FTC has offered several proposed definitions and alternative provisions in the NPRM. Check them out and let us know which ones you think work best.An Advance Notice of Proposed Rulemaking (ANPR) asking whether the FTC should propose additional rule requirements that would apply to the MLM industry. The FTC has reason to believe deceptive earnings claims are prevalent in the MLM industry, and we want to know if more rule provisions – beyond what’s being proposed in the NPRM discussed above – are needed. Check out the Notice for details, but the big questions include whether MLM sellers should be required to: (1) provide earnings data to participants and potential recruits or post that information on their websites; (2) provide clear information about typical earnings whenever they make any earnings claims; or (3) impose a waiting period before recruits can join or pay any money to the MLM.You’ll have 60 days to review and comment on each proposal on Regulations.gov. That 60-day period starts from the date the proposals are published in the Federal Register. We hope you’ll weigh in.
- Online sellers: How the INFORM Consumers Act could impact your business
 by lfair on August 18, 2023 at 4:43 pm
Online sellers: How the INFORM Consumers Act could impact your business lfair August 18, 2023 | 12:43PM Online sellers: How the INFORM Consumers Act could impact your business By Lesley Fair The INFORM Consumers Act took effect on June 27, 2023. The FTC has issued staff guidance for online marketplaces and now we have advice for online sellers whose businesses may be affected by the new law.Congress passed the Integrity, Notification, and Fairness in Online Retail Marketplaces for Consumers Act – or the INFORM Consumers Act – to make online transactions more transparent. The law requires “online marketplaces” to collect, verify, and disclose certain information about “high-volume third party sellers.” Informing Businesses about the INFORM Consumers Act explains more about how the law defines those terms, discusses what’s required of online marketplaces, and outlines the substantial penalties the FTC and state law enforcers may seek if online marketplaces violate the law.A new FTC publication, What Third Party Sellers Need to Know About the INFORM Consumers Act, looks at the statute from the perspective of businesses that sell via online platforms – for example, what sellers are impacted, what you can expect online platforms to require of you, and what information platforms must disclose about you to consumers. It also answers some questions you may have about the law.Have you spotted a violation of the INFORM Consumers Act? Report it to the FTC. We have a dedicated link where you can let us know about possible INFORM Consumers Act violations. Image
- FTC charges battery maker in first case under Made in USA Labeling Rule
 by lfair on April 12, 2022 at 6:15 pm
FTC charges battery maker in first case under Made in USA Labeling Rule lfair April 12, 2022 | 2:15PM FTC charges battery maker in first case under Made in USA Labeling Rule By Lesley Fair For people who prefer to buy Made in USA merchandise, products from Lithionics Battery LLC seemed like an attractive option. According to the FTC, Lithionics and General Manager Steven Tartaglia used phrases and American flag images to convey a Made in USA marketing message for their battery, battery module, and battery management system products. But don’t wave Old Glory just yet. As the FTC’s first action under the new Made in USA Labeling Rule alleges, the lithium ion cells Lithionics used were actually made in China. The proposed settlement includes a civil penalty of $105,319.56 and requires changes in how the company makes Made in USA claims. Image Lithionics sells battery products for recreational vehicles, marine applications, and similar uses. The defendants labeled their merchandise with an image of the flag image surrounded by the words “Made in U.S.A.” Sometimes they added the phrase “Proudly Designed and Built in USA.” The defendants doubled down on those representations on the Lithionics website, in mail order catalogs, and in social media. For example, the complaint cites YouTube videos featuring Tartaglia and company employees putting Made in USA labels on Lithionics products. Other marketing materials featured a chart comparing the “advantage[s] of Lithionics battery systems” to what are described as “imports.” Image Under the Made in USA Labeling Rule, marketers are prohibited from labeling products as “Made in USA” unless all or virtually all ingredients or components are made and sourced in the United States. What’s more, the final assembly or processing – and all significant processing that goes into the product – must occur in the US. But according to the FTC, Lithionics battery and battery module products incorporated Chinese-made lithium ion cells, and Lithionics battery management systems included significant imported components. That’s why the FTC says the defendants’ “Made in USA” claims were deceptive. The complaint, which names both Lithionics and Tartaglia, alleges violations of the Made in USA Rule and Section 5 of the FTC Act. In addition to a civil penalty of $105,319.56 authorized under the new Rule, the proposed settlement includes injunctive provisions that will change how the defendants do business going forward. For example, the order prohibits them from making unqualified U.S.-origin claims unless they have proof that the product’s final assembly or processing – and all significant processing – takes place in the US and that all or virtually all ingredients or components are made and sourced here. The order further requires that any qualified Made in USA claims include clear disclosures about the extent to which the product contains foreign parts, ingredients, or components, or involved foreign processing. Finally, if the defendants convey that a product is assembled in the United States, they must ensure it was last substantially transformed in the US, its principal assembly took place here, and US assembly operations are substantial. If your company makes Made in USA claims, the case offers two important compliance notes. Review the Rule to keep your representations red, white, and true. If you make Made in USA claims, do they comport with the Made in USA Labeling Rule? The new civil penalty remedy can make non-compliance costly.If necessary, take care to qualify your claims. If you make Made in USA claims that are “unqualified “ – in FTC parlance, that means claims that aren’t modified or limited – you must to live up to the “all or virtually all” standard. If you made “qualified claims” – claims that include caveats or explanations – the legal onus is on you to ensure those qualifications are clearly understood by consumers. The FTC’s Enforcement Policy Statement on U.S. Origin Claims provides more guidance on making Made in USA claims.
- Data security hearings start today: Watch the webcast
 by lfair on December 11, 2018 at 1:43 pm
Data security hearings start today: Watch the webcast lfair December 11, 2018 | 8:43AM Data security hearings start today: Watch the webcast By Lesley Fair You’ve probably been following the FTC Hearings on Competition and Consumer Protection in the 21st Century. The next two days of hearings – Tuesday, December 11th, and Wednesday, December 12th – will take a deep dive into a topic of interest to just about every business and consumer: data security. No matter where you’re located, it’s easy to participate. Today’s proceedings begin at 10:10 Eastern Time. After opening remarks from Andrew Smith, Director of the FTC’s Bureau of Consumer Protection, panels will cover data breaches, incentives to invest in data security, and the consumer demand for it. Speakers include academics, industry members, and security researchers. The two-day hearing is free and open to the public at the FTC’s Constitution Center, 400 7th Street, S.W., located at the Metro L’Enfant Plaza station. Can’t attend in person? Watch the webcast by following the link that will go live a few minutes before the 10:10 starting time. You can file a public comment on issues raised at the data security hearing by March 13, 2019.
- FTC says deceptive rental listings were nothing to write home about
 by lfair on September 17, 2018 at 5:03 pm
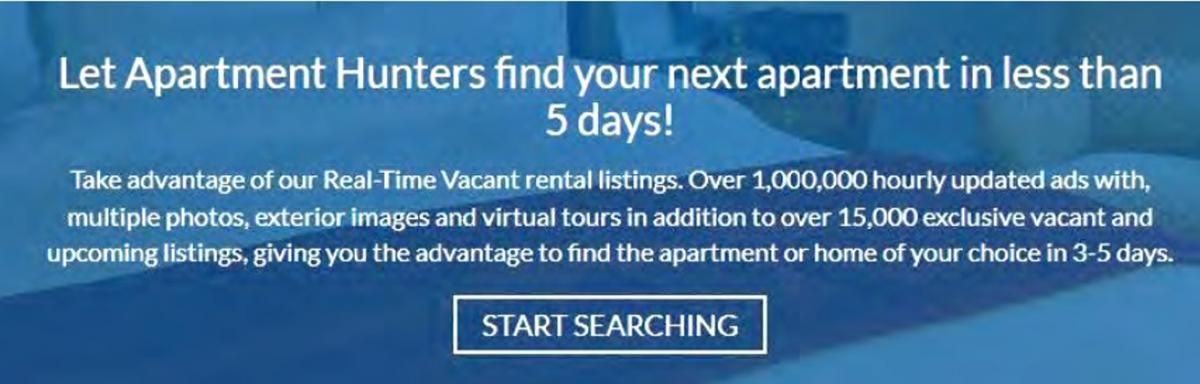
FTC says deceptive rental listings were nothing to write home about lfair September 17, 2018 | 1:03PM FTC says deceptive rental listings were nothing to write home about By Lesley Fair As the song goes, “A house is not a home.” And as alleged in an FTC lawsuit against the operators of rental listing websites, sometimes an apartment isn’t an apartment. Steven Shayan, Kevin Shayan, and affiliated companies run ApartmentHunterz.com, FeaturedRentals.com, and WeTakeSection8.com. For consumers who pay weekly or monthly subscription fees, the defendants promise accurate listings for available units. For example, ApartmentHunterz.com claims its “unique, date-sensitive, rental software updates the listings on a daily basis, so that the data you receive from us is the most accurate and up-to-date information available on the Web today.” Touting “Real-Time Vacant rental listings,” the site purports to feature “over 1,000,000 hourly updated ads” and “over 15,000 exclusive vacant and upcoming listings, giving you the advantage to find the apartment or home of your choice in 3-5 days.” No need to worry about outdated information, the site assures prospective tenants. The company uses “phone and email verification to remove rented listings and verify price changes as well as post new rentals hourly as they become available.” FeaturedRentals.com echoes those accuracy claims, putting a particular emphasis on the quality of its listings. Unlike “free sites or yellow pages that just lists the community that might not have a vacancy,” FeaturedRentals.com describes itself as “a reputable rental site” that gets information “directly from landlords and management companies,” “verif[ies] the availability of the properties,” and then “updates its search engine on a daily and hourly basis.” For elderly and disabled consumers and very low-income families who qualify for Section 8 housing assistance, available units can be particularly hard to find. But WeTakeSection8.com billed itself as “the Nation’s Largest Section 8 Apartment Finder” and “one the most up-to-date sites” for rentals that are “already set up to accept the vouchers.” Why buy a subscription to WeTakeSection8.com? Because unlike sites that include “old listings that have long since been rented,” WeTakeSection8.com claims to offer “thousands of updated and verified listings including exclusive listings not found on free websites.” But according to the FTC, the defendants’ sites are rife with inaccurate or unavailable listings. Hundreds of consumers and property managers have complained directly to the defendants and through groups like the BBB. Among other things, they reported that units on the site weren’t really for rent. And we’re not talking about “Gosh darn it. Somebody just signed a lease this morning” near-misses. Consumers and property managers report that apartments featured on the defendants’ sites had been rented months – or even years – earlier. In addition, the FTC alleges that many listings on WeTakeSection8.com don’t actually accept Section 8 vouchers. Anyone who pays a subscription fee for a service that doesn’t deliver as promised experiences financial injury, but it takes a particular bite out of the budget of low-income consumers who qualify for Section 8. According to the complaint, the defendants’ conduct harms those consumers in another way, too. A disabled person or low-income family can spend years on the Section 8 waiting list. But once they qualify for a voucher, they may have only 60-90 days to find a place that takes Section 8. Time spent going down blind alleys – for example, pursuing listed properties that aren’t really available – cuts into that narrow window. The FTC lawsuit alleges (among other things) that the defendants’ claims of offering accurate, up-to-date, and available listings are false or deceptive. The complaint also challenges the defendants’ representation that their sites feature “exclusive” listing of available apartments and Section 8 units not available on free sites. Furthermore, as the FTC lawsuit notes, this wasn’t the defendants’ first rental rebuke. The California Department of Real Estate revoked ApartmentHunterz’ license, but it has continued to do business. Then there were earlier state disciplinary actions for false and misleading ads. A federal court in California has issued a temporary restraining order. What’s the word for other businesses? Even at this early stage, the complaint is a reminder that companies have a legal obligation to live up to promises they make in their ads. That’s the case if they sell widgets and gadgets or if their stock-in-trade is paid access to curated information. If you deal in data, established truth-in-advertising standards still apply.
- “Amazing Wealth System” not so amazing, alleges the FTC
 by lfair on March 23, 2018 at 4:17 pm
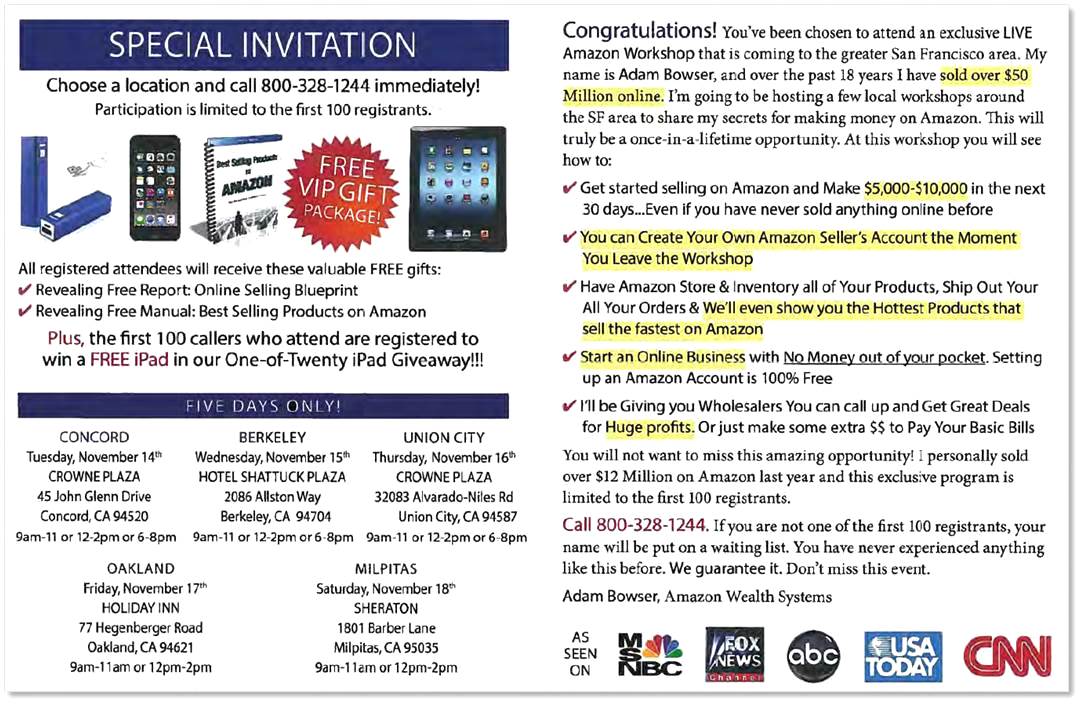
“Amazing Wealth System” not so amazing, alleges the FTC lfair March 23, 2018 | 12:17PM “Amazing Wealth System” not so amazing, alleges the FTC By Lesley Fair An FTC lawsuit alleges that money-making claims made by a related group of companies and individuals for their Amazing Wealth System are “amazing” all right – if by “amazing” you mean “not credible” or “unsupported by the facts.” The complaint charges the defendants with violating the FTC Act and the Business Opportunity Rule. One interesting factual twist is how elements of the “system” allegedly depend on subverting Amazon’s rules about online reviews and third-party sales.Defendants advertise their Amazing Wealth System via direct mail, radio, YouTube videos, social media, and live events. (Consumers may know them by names like Amazon Wealth Systems, FBA Stores, Insider Online Secrets, or Online Auction Learning Center. But let’s be clear: The defendants have no affiliation with Amazon.)According to the FTC, the defendants lure prospective purchasers in with claims like this:“My name is Adam Bowser, and over the past 18 years I have sold over $50 million online. I’m going to be hosting a few local workshops around the Seattle area to share my secrets for making money on Amazon.”“Get started selling on Amazon and make $5,000-$10,000 in the next 30 days . . . Even if you have never sold anything online before.”“Just last year we sold over $12 Million on Amazon.com. Now we want to help you become our next Amazon success story.”The defendants’ initial step is bringing consumers in for a free two-hour seminar. At the seminar, they pitch their $995 three-day workshops: “How many of you would love to be able to learn how you can make an extra $5,000 to $10,000 a month by spending 30 minutes to an hour a day learning and implementing a plug-and-play system I’m going to share with you here in a moment.”According to the FTC, the three-day workshops shift the hype into overdrive, including the sale of more expensive packages like the $34,995 “Diamond” enrollment. As one pitch person said at a workshop, “So whether you want an extra $20- to $30,000 a year or you want to create a million dollar a year business, I’m going to show you how to do either of those.”The complaint alleges that in purporting to showing people “how to do either of those,” much of the information the defendants convey is basic stuff available for free on Amazon’s Resources and Tutorials page. However, other “tips, tricks, and techniques” allegedly violate Amazon’s Business Solutions Agreement, the document that sets forth the rules that companies must follow if they want to sell on Amazon. For example, according to the FTC, the defendants instruct consumers who buy their Amazing Wealth System to get fake product reviews for the items they list on Amazon – advice that violates Amazon’s Anti-Manipulation Policy for Customer Reviews. Another of those “tricks” teaches people to use various ruses in an effort to “win the box” – in other words, to be the seller of choice in Amazon’s coveted Buy Box when the same merchandise is available from multiple sellers. As a result, says the FTC, purchasers who use the defendants’ system often experience problems with their Amazon stores, including getting suspending and losing their ability to sell on the site.The FTC lawsuit charges that people who buy the Amazing Wealth System and try to use the defendants’ strategies are unlikely to earn the income the defendants advertise. And according to the lawsuit, the defendants’ brief “earnings disclaimers” are ineffective to undo the net impression that people who implement the “system” are likely to make money.The complaint alleges other specific violations of the Business Opportunity Rule. The FTC says the defendants failed to make advertising disclosures mandated by the Rule, including the number and percentage of people who bought the business opportunity and achieved at least the stated level of earnings. Furthermore, in many cases, the defendants allegedly failed to furnish prospective purchasers in a timely fashion with the disclosure document and attachments required by the Business Opportunities Rule.The case is pending in federal court in Nevada. The court has appointed a temporary receiver over the corporate defendants, enjoined the defendants from making deceptive claims, and frozen their assets pending resolution of the FTC’s preliminary injunction motion.Even at this early stage, the case is a reminder to companies that offer business opportunities to conduct a Rule review to make sure they’re in compliance. What’s the message for would-be entrepreneurs? View money-making claims with a seriously skeptical eye. In addition, if anyone suggests that you solicit, post, or in any other way involve yourself with product reviews that aren’t 100% accurate and independent, you’re getting really bad advice. The FTC endorsements page has resources on that subject.
- 4 tips businesses can take from the FTC’s $19+ million Google settlementby wfg-adm109 on September 4, 2014 at 4:39 pm
4 tips businesses can take from the FTC’s $19+ million Google settlement wfg-adm109 September 4, 2014 | 12:39PM 4 tips businesses can take from the FTC’s $19+ million Google settlement By Lesley Fair The polar bears and penguins sold within kids’ apps offered in the Google Play Store may have been virtual, but the unauthorized charges Moms and Dads got stuck with were all too real. A proposed FTC settlement will refund at least $19 million to parents whose accounts were charged illegally, according to the complaint, and will implement enforceable changes in how Google handles in-app purchases. Of course, the order applies just to Google, but the case offers compliance tips for anyone in the app industry. How do your practices measure up?Many of the kids’ apps available from Google – even some of the free ones – offer in-app purchases. At a per-click cost that ranges from 99 cents to $200, they don’t come cheap. According to the FTC, when Google first introduced in-app charges in 2011, the company didn’t require a password or other method to get the account holder’s authorization. Kids could incur in-app charges billable to their parents simply by clicking on popups within the app – as Moms and Dads found out when they checked their statements and learned that all those clicks had resulted in hefty unauthorized charges.Sometime in 2012, Google changed its procedures and started to present a popup that asked for the account holder’s password before purchase. But the FTC says Google’s purported “fix” didn’t solve the problem – and actually introduced confusing new wrinkles. For example, the new popup just asked the account holder to type in their password and click CONFIRM, but never mentioned anything about charging for an in-app purchase. But it gets worse: Google didn’t tell people that entering a password opened a 30-minute window where kids could rack up unlimited charges without Mom or Dad’s approval. In effect, how Google chose to design its payment system created a half-hour shopping spree for kids, with parents obligated to pay the piper. In this case, the piper was Google, which pocketed about 30% for every app sold in its store.This isn’t the FTC’s first salvo against unauthorized in-app charges in kids’ apps. In January, it was a $32.5 million settlement with Apple that requires the company to get the account holder’s express, informed consent. In July, the FTC sued Amazon.com, also seeking full refunds for consumers and an order requiring informed consent for in-app charges. (That case is pending in federal court in Seattle.)For members of the app industry interested in keeping their practices within the law, what tips can they take from the Google settlement?1) Get consumers’ express consent before billing them. It’s hardly a novel concept, but it bears repeating: It’s illegal to place charges on consumers’ accounts without their permission. That was the law before the advent of mobile apps and we’ll go out on a limb and say the same principle will apply to The Next New Thing. Regardless of what you sell or how you sell it, get people’s informed OK before billing them.2) Read – and heed – your mail. According to the complaint, Google started to get flak from consumers almost as soon as it introduced in-app purchases in kids’ apps. The FTC’s complaint cites just a few of the thousands of communications from parents that should have made it crystal-clear to Google that it had a problem on its hands. What’s the message for marketers? One insightful – and free – gauge of what’s going on in the marketplace is what your customers are telling you.3) Listen to your staff. It wasn’t just parents who expressed concerns. In a 2012 email, one Google product manager warned higher-ups that:“friendly fraud” (unauthorized purchases by individuals you know) is the lead cause of chargebacks. For example, parents realize their kids have made a series of purchases and call the credit card company claiming those were unauthorized. Risk estimates that close to 80% of current chargebacks are driven by this specific issue.Another in-house communication referred to a “high number of canceled orders for in-app billing” and explained that “these usually tend to be family fraud (kids takes phone and buys lots of food for virtual fish).” Remember: Those weren’t quotes from someone with an axe to grind. It’s what Google’s own people were saying about problems with the payment process.4) Nix the trick fix. Once you know there’s a problem, commit your company to correct it pronto. It’s unlikely that half-hearted measures will do the trick. As the complaint in this case alleges, the changes Google implemented didn’t solve the problem. What’s the next step for businesses? Think through how you bill customers to make sure you have their express authorization. Take special care with kid-related apps. If you were one of the parents billed without your permission, the settlement requires Google to contact you within 15 days of the final entry of the order with details on how to get a refund.You have until October 6, 2014, to file online comments about the proposed settlement.
- Default lines: How the FTC says Credit Karma and Fandango SSLighted security settingsby wfg-adm109 on March 28, 2014 at 1:35 pm
Default lines: How the FTC says Credit Karma and Fandango SSLighted security settings wfg-adm109 March 28, 2014 | 9:35AM Default lines: How the FTC says Credit Karma and Fandango SSLighted security settings By Lesley Fair Imagine a burly doorman at an exclusive party. When someone claims to be a guest, the doorman checks their invitation and runs it against the names on the list. If it doesn’t match up, the person won’t make it through the velvet rope. But what happens if the doorman isn’t doing his job? His lapse could allow a ringer into the party to scarf up the hors d’oeuvres and steal the valuables. It’s not a perfect analogy, of course, but the FTC’s settlements with credit information company Credit Karma and movie ticket site Fandango demonstrate the dangers when companies override the default settings of operating systems designed to authenticate and secure the connections used to transmit sensitive information. Here’s how things work after a consumer has downloaded an app onto a device. Think of Secure Sockets Layer (SSL), the industry-standard protocol to establish encrypted connections, as the doorman. When an online service wants to connect to an app, the service presents an SSL certificate to vouch for its identity. Once the app validates the certificate, the online service is allowed through the velvet rope and establishes an encrypted connection to the device so the consumer can send information. This one-two punch of validation through an SSL certificate and encryption creates a safer way for people to transmit sensitive data. But fraudsters have been known to use spoofing techniques to mount what are called man-in-the-middle attacks. If the app doesn’t check the SSL certificate, an attacker can use an invalid certificate to get their foot in the door and establish a connection to intercept information sent between the app and the online service. Neither the person using the app nor the online service realizes what’s going on. Securing the transmission of personal information against threats like man-in-the-middle attacks is so important that the iOS and Android operating systems provide developers with easy-to-use application programming interfaces – APIs – to implement SSL. By default, these APIs automatically validate SSL certificates and reject the connection if the certificate is invalid. The developer documentation for both the iOS and Android operating systems uses particularly strong language to warn against disabling those default validation settings. According to the iOS documentation, failing to validate SSL certificates “eliminates any benefit you might otherwise have gotten from using a secure connection. The resulting connection is no safer than sending the request via unencrypted HTTP because it provides no protection from spoofing by a fake server.” The Android documentation doesn’t mince words either: An app that doesn’t validate SSL certificates “might as well not be encrypting communication, because anyone can attack users at a public Wi-Fi hot spot . . . [and] the attacker can then record passwords and personal data.” According to the FTC, Credit Karma and Fandango ignored those “Don’t go there” warnings. While developing its iOS app, which lets consumers get their credit scores and monitor other financial data, Credit Karma authorized a service provider to use code that disabled SSL certificate validation for the purpose of testing. But the FTC says Credit Karma let the app go to market without turning the default settings back on. So between July 18, 2012, and around January 1, 2013, the company’s iOS app was vulnerable to man-in-the-middle attacks, putting users’ Social Security numbers, dates of birth, and credit report data at risk. How did CreditKarma find out about the problem? According to the FTC, not through its own in-house checks and monitoring. The complaint alleges that a user contacted Credit Karma, leading the company’s engineers to update the app in January 2013 to restore the default settings. But that’s not the end of the Credit Karma story. A short time later, FTC staff contacted Credit Karma about the problem. Only then did the company’s in-house team run a security review on both versions of the app. Was it a complicated, expensive, time-consuming thing? No. According to the FTC, it took just a few hours and cost next to nothing. And guess what it revealed? In February 2013 – after Credit Karma had been told about the iOS vulnerability – the company launched the Android version of its app with the exact same problem. The review also revealed another security glitch: The iOS app was storing authentication tokens and passcodes on the device in an insecure manner. The FTC’s lawsuit against Fandango charges the company with similar lapses. From March 2009 until March 2013, the iOS version of Fandango’s app failed to validate SSL certificates, overriding the system’s security defaults. According to the FTC, Fandango didn’t test its app before release to make sure it was validating SSL certificates and securely transmitting consumers’ personal data, including credit card numbers, expiration dates, and security codes. Yes, Fandango commissioned some audits in 2011, a full two years after the app was released. But even then, it limited the scope to include only threats posed when the attacker had physical access to a consumer’s device. It didn’t test for secure data transmission. Thus, Fandango missed an opportunity to detect the vulnerability it had introduced by overriding the defaults. The FTC says Fandango compounded the problem by not having an effective channel for people to report security problems. According to the complaint, a researcher contacted the company in December 2012 through the only method readily available – a Customer Service web form. Because the researcher’s message included the term “password,” Fandango’s Customer Service system treated it as a routine password reset request and responded with a canned message. The system then dismissed the security warning as “resolved.” When did Fandango finally fix the problem? According to the complaint, it wasn’t until the company heard from FTC staff. Only then did Fandango run the simple test that revealed that its app failed to validate SSL certificates. Fandango also found out that the vulnerability affected a separate movie ticket app it hosted for a third party. Within three weeks, Fandango issued an update of both iOS apps that restored the default settings, thereby plugging that security hole. The proposed settlements with Credit Karma and Fandango require the companies to put comprehensive security programs in place to address risks related to the development and management of new and existing products and to protect the security, integrity, and confidentiality of information covered by the order. Consistent with other settlements, Credit Karma and Fandango will need stem-to-stern security audits from an independent professional every other year for the next 20 years. Of course, the terms of the agreements apply just to those companies, but savvy businesses will want to read the proposed orders to see what’s required of Credit Karma and Fandango. You can file a comment about the proposed settlements by April 28, 2014. What else can companies learn from these cases? 1. Exercise extreme care when modifying security defaults. Had the companies left well enough alone, the security defaults of the operating systems would have protected consumers’ personal information from man-in-the-middle attacks. Of course, we’re not saying it’s always illegal to modify a default setting. In fact, there are ways you can go above and beyond the default SSL certificate validation by implementing an even stronger authentication method known as “certificate pinning.” But modifying security defaults is the brain surgery of app development. Companies need to be darn sure they know what they’re doing. 2. Test your app thoroughly before releasing it. Carpenters have an old adage: “Measure twice, cut once.” The corollary for app developers: Take advantage of readily available free or low-cost methods for testing the security of your apps before you put them into consumers’ hands. 3. Consider how people will use your apps. There’s a reason why SSL is so important in the mobile environment and why the iOS and Android developer documentation makes such a big deal about it: because people often use mobile apps on unsecured public Wi-Fi networks. Like chess players, developers need to think a few moves ahead. Before releasing an app, think through how people are likely to use it and secure it with those real-world considerations in mind. 4. You’re responsible for what others do on your behalf. According to the complaint, Credit Karma authorized a service provider to disable the SSL certificate validation process during pre-release testing, but didn’t see to it that the security settings were restored after that. The first concern: The testing could have been done without turning the defaults off. But even so, it’s critically important that companies make sure everything is back in apple pie order before consumers get the app. 5. Keep your ear to the ground. There’s an active research community out there that shares information about potential security vulnerabilities. But by responding to a serious warning with a standard “bedbug letter,” Fandango missed the opportunity to fix the problems. Has a knowledgeable person contacted your company recently about a potential risk? And is that message languishing unread in an email box? 6. Consult available resources. The FTC brochure, Mobile App Developers: Start with Security, offers advice for companies about protecting against this type of vulnerability: To protect users, developers often deploy SSL/TLS in the form of HTTPS. Consider using HTTPS or another industry-standard method. There’s no need to reinvent the wheel. If you use HTTPS, use a digital certificate and ensure your app checks it properly. A no-frills digital certificate from a reputable vendor is inexpensive and helps your customers ensure they’re communicating with your servers, and not someone else’s. But standards change, so keep an eye on current technologies, and make sure you’re using the latest and greatest security features. Bookmark the FTC’s Privacy & Security page and consult other public sources for free information about developing safer apps.
- Painting the town greenby wfg-adm109 on October 25, 2012 at 4:27 pm
Painting the town green wfg-adm109 October 25, 2012 | 12:27PM Painting the town green By Lesley Fair The biggest decision facing a DIYer in the paint store used to be whether Dusting of Snow or Wistful Beige was right for the dining room. But nowadays more businesses are making express claims about their products, including purported environmental benefits. Two of the nation’s leading paint companies — The Sherwin-Williams Company and PPG Architectural Finishes, Inc. — advertised that some of their paints were free of volatile organic compounds (VOCs).First, a little VOC-ational education about paint. Some VOCs (carbon-containing compounds that evaporate at room temperature) can be harmful to human health and to the environment. Many interior wall paints contain significant levels of VOCs, so it’s not surprising that companies have introduced paints advertised as free of VOCs. The “zero VOCs” claim for Sherwin-Williams’ Dutch Boy Refresh and PPG’s Pure Performance were on product labels, on point-of-purchase displays, online, and in the media. The companies also disseminated them through promotional materials provided to independent distributors and retailers.But the FTC says the companies colored the truth about the level of VOCs in the paint people bought. According to the complaint, while the “zero VOCs” representation may have been accurate for the uncolored base, buyers generally get tinted paint, which may contain significant levels of VOCs. Therefore, the FTC charged that the companies’ “zero VOCs” claims were false. The complaint also alleges that Sherwin-Williams and PPG gave distributors and retailers the “means and instrumentalities” to disseminate misleading claims, in violation of the FTC Act.To settle the charges, the companies have agreed not to make deceptive claims in the future. (Read the Sherwin-WIlliams pleadings and PPG pleadings for the specifics.) If they say expressly or by implication that the VOC level of a paint is zero, they’ll need sound science to prove that it contains no VOCs — or no more than a trace level. The definition of “trace level” comes from the FTC’s revised Green Guides: that VOCs haven’t been intentionally added to the product, that the presence of VOCs at that level doesn’t cause material harm to health or to the environment typically associated with VOCs, and the VOC level isn’t higher than what’s found in background levels in ambient air.The order gives the companies two other options. If after tinting, the VOC level is below a certain specified level, the companies can clearly and prominently disclose that the claim applies only to the base paint and that the actual VOC level may increase, depending on the color choice. A third option: They can clearly and prominently disclose that the claim applies on to the base paint and that the VOC level may increase “significantly” or “up to [insert: the highest possible VOC level after tinting],” depending on the color choice. The order also bans unsubstantiated environmental benefit claims for any covered product.In response to the FTC’s lawsuit, the companies also agreed to send letters to their dealers and distributors, directing them to stop using ads and marketing materials making the “no VOCs” or “zero VOCs” claims challenged in the complaint. Sherwin-Williams and PPG also will direct dealers and distributors to sticker over those claims on paint cans. What’s the take-away for businesses? First, view claims from your customers’ perspective. Put another way, what really matters to people shopping for paint? The VOC levels in the base or in the paint that was actually going on the walls of their homes? Second, if you haven’t had a chance to take a look at the revised Green Guides, here’s a timely opportunity.Interested in commenting on the proposed settlements? The deadline is November 26, 2012. Contemplating a little do-it-yourself? Read Before You Buy Paint.
FTC Business Blog



We are an ethical website cyber security team and we perform security assessments to protect our clients.