
Chronicles of a CISO The world through a CISO’s eyes
- Building the Enterprise Identity Operating Model
 by John Masserini on September 22, 2026 at 7:37 pm
Building the Enterprise Identity Operating Model challenges the legacy view of identity as simply an access permission model. Instead, it defines identity as a continuously evaluated risk construct, requiring centralized visibility, policy orchestration, and lifecycle control. My new release provides a step-by-step model of controls enterprise’s must consider when building out a modern identity management infrastructure. The post Building the Enterprise Identity Operating Model appeared first on Chronicles of a CISO.
- Q&A with Expert Insights
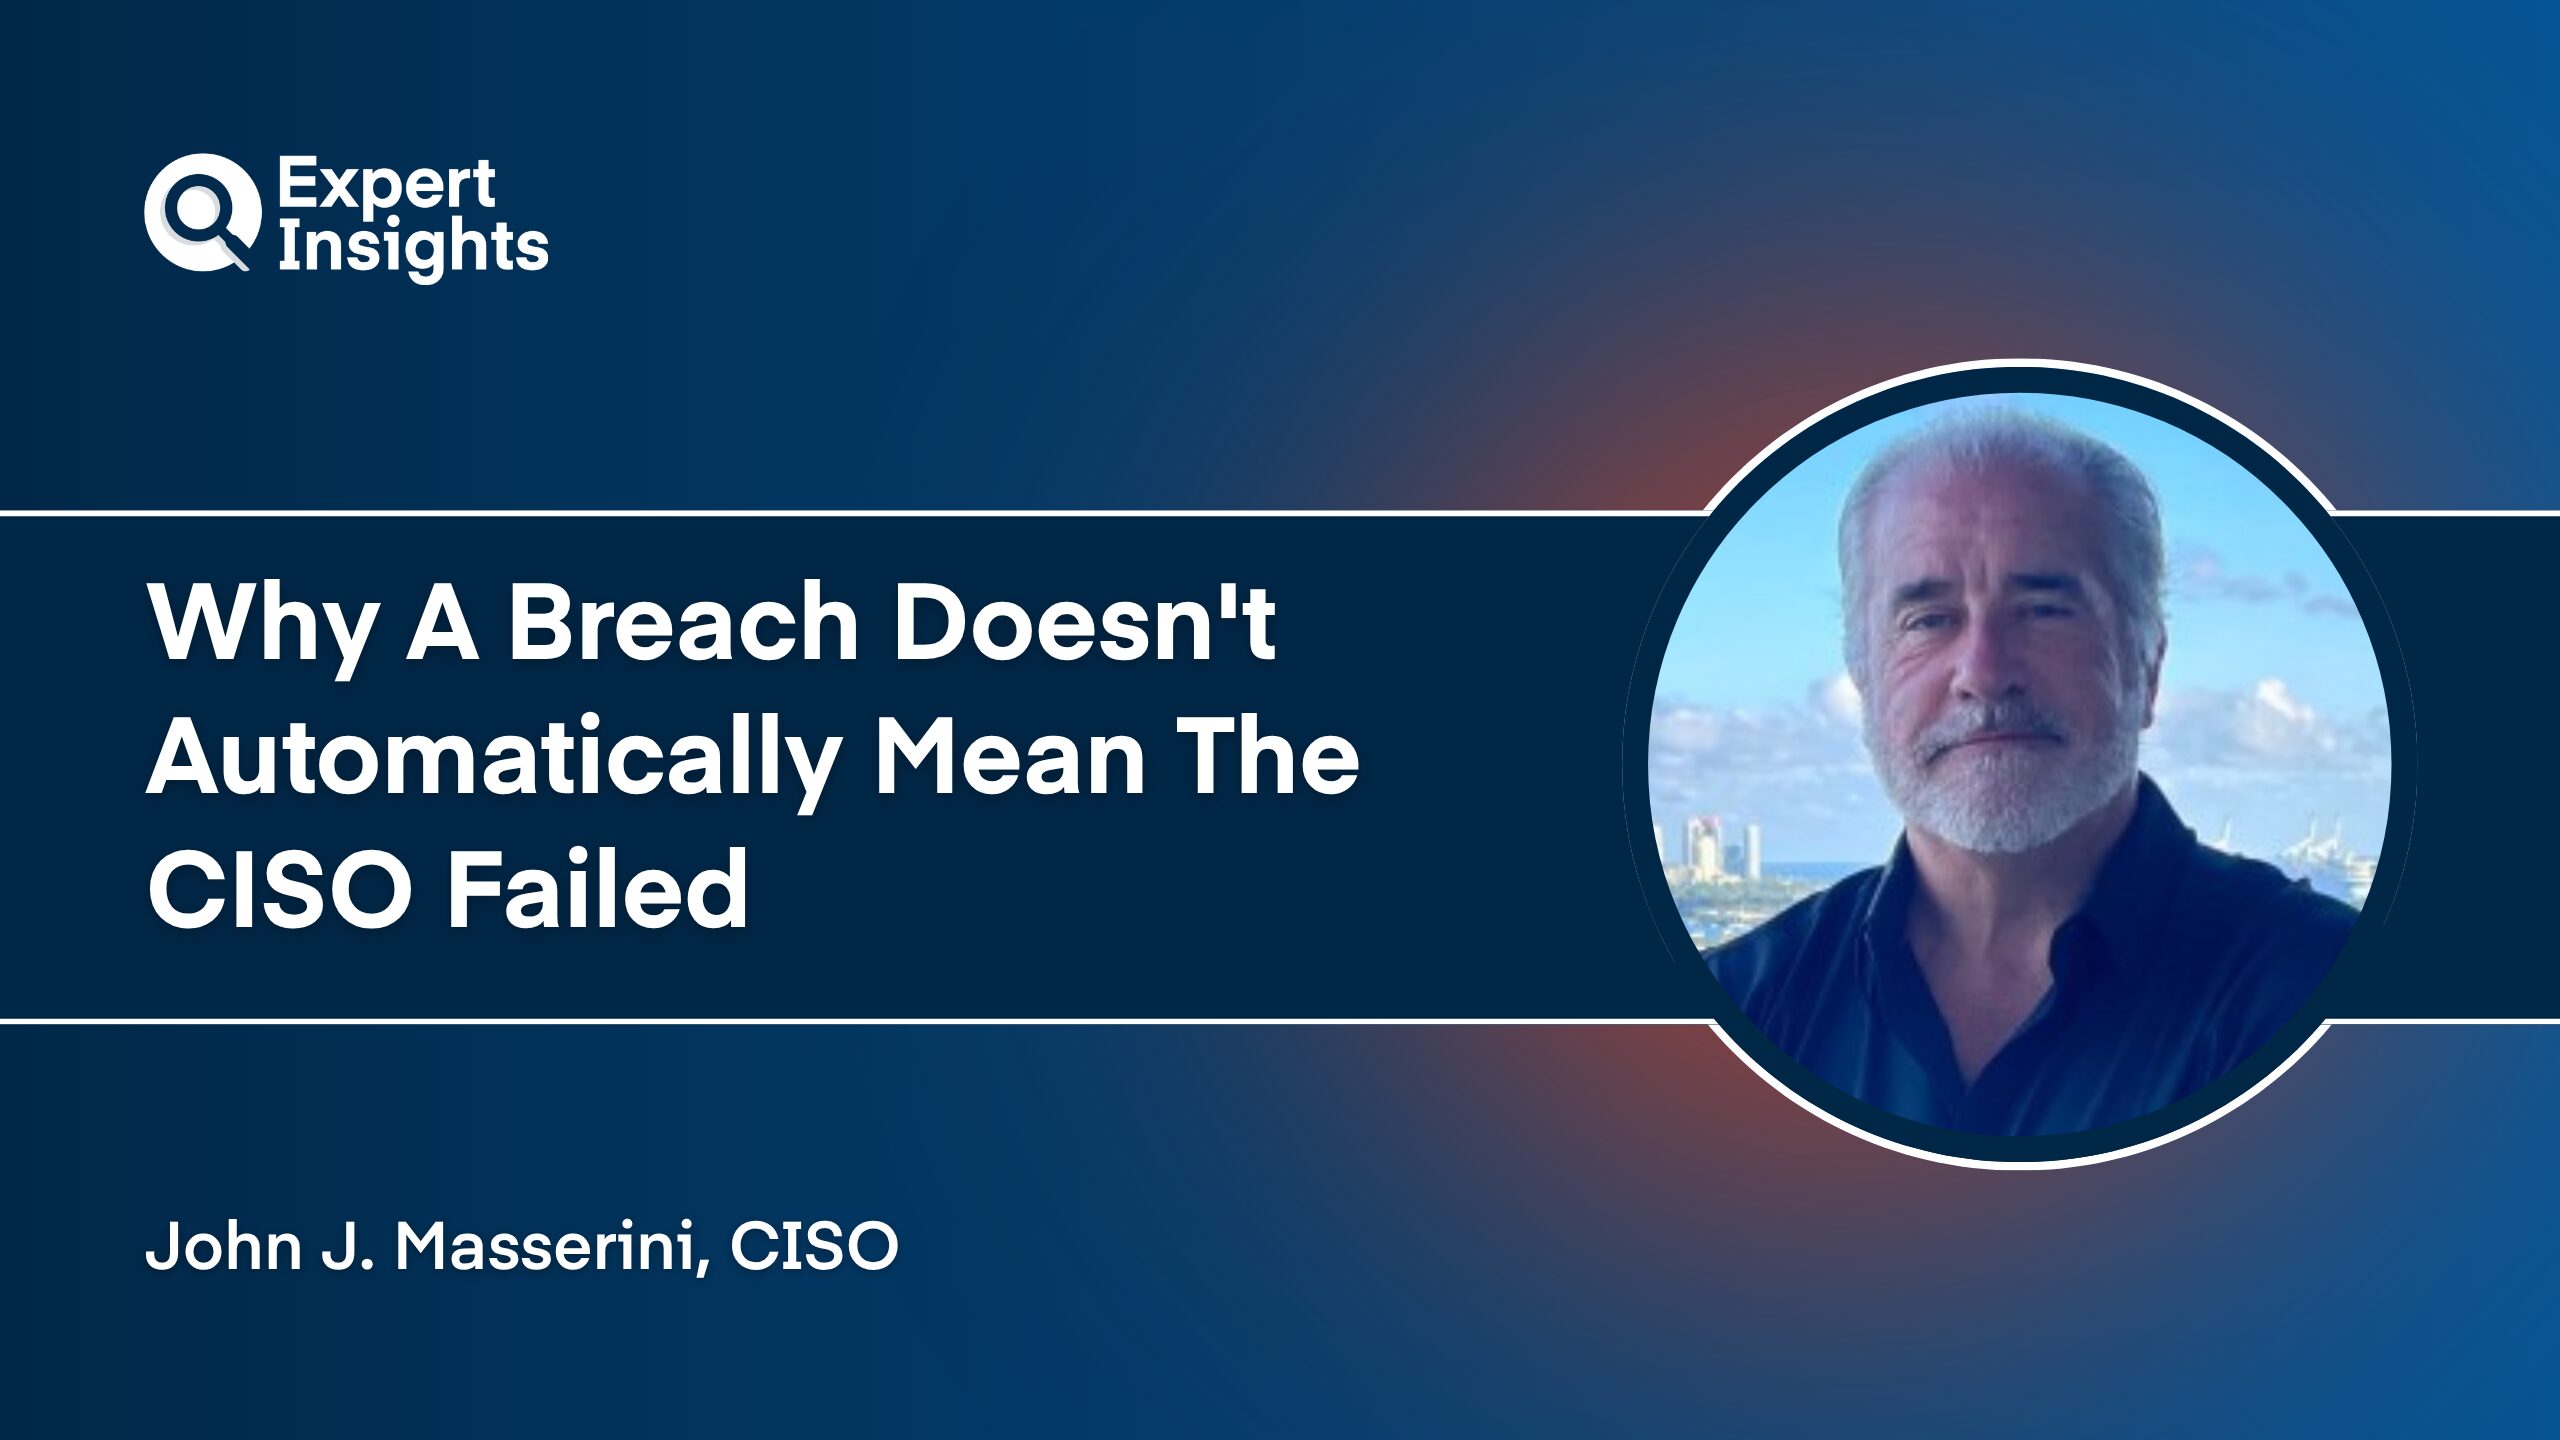 by John Masserini on August 29, 2026 at 6:05 pm
An interview with Expert Insights on the challenges of CISO liability, organization structure, and breach response time. The post Q&A with Expert Insights appeared first on Chronicles of a CISO.
- Interview with CISO Voice
 by John Masserini on August 18, 2026 at 1:45 pm
An interview with CISOVoice around on Identity sprawl, being a CISO, the gap between authority and expectations, and why boards that understand the difference end up with better security programs. The post Interview with CISO Voice appeared first on Chronicles of a CISO.
- Root to CISO Podcast
 by John Masserini on August 11, 2026 at 3:51 pm
Root to CISO podcast where we discuss the security industry, and topics like certifications, experience, and the need for college degrees. The post Root to CISO Podcast appeared first on Chronicles of a CISO.
- Security Chiefs Unfazed by Federal AI Oversight
 by John Masserini on June 5, 2026 at 1:57 pm
An interview with the Wall Street Journal around the new AI Executive Order and the federal ‘safety check’ being proposed. The post Security Chiefs Unfazed by Federal AI Oversight appeared first on Chronicles of a CISO.
- 2025 Top-20 Best CISO Blogs
 by JM on May 2, 2025 at 10:01 am
Chronicles of a CISO has been ranked 8th of the Top-20 Best CISO blogs on Feedspot The post 2025 Top-20 Best CISO Blogs appeared first on Chronicles of a CISO.
- RSAC 2025 NIST CSF Session
 by JM on April 30, 2025 at 12:03 pm
A recap of my NIST CSF Maturity Toolkit session for RSAC 2025. The post RSAC 2025 NIST CSF Session appeared first on Chronicles of a CISO.
- Risk Preparedness in the Age of Policy Volatility
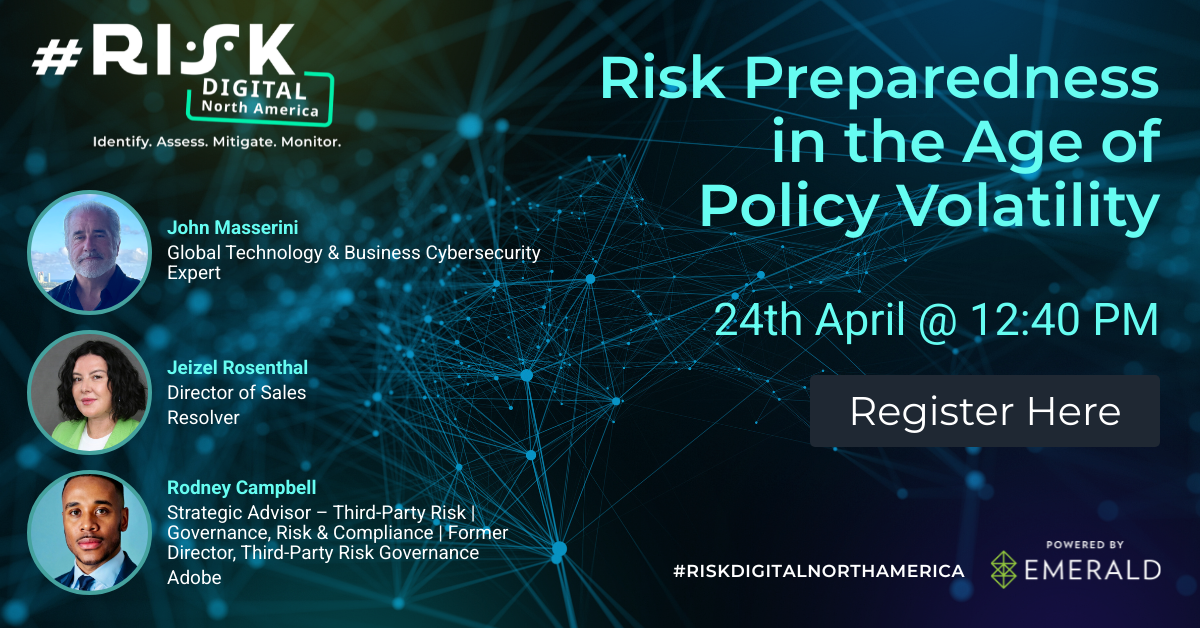 by John Masserini on April 24, 2025 at 10:06 pm
This panel discussion, as part of the Digital Risk North America virtual event, focuses on Risk Preparedness in the Age of Policy Volatility The post Risk Preparedness in the Age of Policy Volatility appeared first on Chronicles of a CISO.
- The Virtual CISO Moment Interview
 by John Masserini on March 25, 2025 at 1:57 pm
Virtual CISO Moment podcast with Greg Schaffer. We discussed the challenges facing SMBs when it comes to security and how we need to fix the model. The post The Virtual CISO Moment Interview appeared first on Chronicles of a CISO.
- 2025 Top-100 Best Security Blogs
 by JM on March 24, 2025 at 3:07 pm
Chronicles of a CISO has been named to the Top-100 Best Information Security blogs on Feedspot The post 2025 Top-100 Best Security Blogs appeared first on Chronicles of a CISO.
- The Compliance Equation: Preparing for Regulatory Shifts Under Trump 2025
 by JM on January 31, 2025 at 1:30 pm
This panel discussion, as part of the Digital Risk North America virtual event, focuses on the anticipated regulatory changes from the incoming Trump administration. The post The Compliance Equation: Preparing for Regulatory Shifts Under Trump 2025 appeared first on Chronicles of a CISO.
- Inside Out: Unveiling and Mitigating Insider Threats in the Modern Workplace
 by JM on December 12, 2024 at 12:18 pm
A panel discussion, as part of the PrivSec Global event, that focuses on the complexities of insider threats, exploring the motivations behind them, detection methods and effective mitigation strategies. The post Inside Out: Unveiling and Mitigating Insider Threats in the Modern Workplace appeared first on Chronicles of a CISO.
- Zero Trust Architecture: Implementing Best Practices in the US
 by JM on October 22, 2024 at 1:55 pm
This panel discussion, as part of the GRC World Forums Digital Risk US virtual event, focuses on implementing best practices for Zero Trust Architectures. The post Zero Trust Architecture: Implementing Best Practices in the US appeared first on Chronicles of a CISO.
- Compliance, Due Diligence, & More: Navigating Upcoming TPRM Trends
 by JM on September 13, 2024 at 8:07 pm
A discussion with Scott Lang, VP of Product Marketing at Prevalent, as we explore the emerging trends in TPRM and provide actionable insights to help you stay ahead of your third-party risks. The post Compliance, Due Diligence, & More: Navigating Upcoming TPRM Trends appeared first on Chronicles of a CISO.
- Inherent Risk vs. Residual Risk: The Foundation of Effective TPRMby JM on August 21, 2024 at 5:12 pm
An on-demand webinar around effectively managing inherent and residual third-party risks and their importance for a durable third-party risk management (TPRM) program. The post Inherent Risk vs. Residual Risk: The Foundation of Effective TPRM appeared first on Chronicles of a CISO.