K logix Blog Content that helps security professionals align information security with business objectives.
- The Future of Security Operations
 by Meghan Mulkeen on September 23, 2026 at 3:27 pm
- Profile: Sean Calista, Sr Director of Information Technology and Security, CloudZero
 by khaug@klogixcorp.com (Katie Haug) on September 15, 2026 at 4:51 pm
- Profile: Salaam Harris, CISO, CRICO/Risk Management, The Risk Management Foundation of the Harvard Medical Institutions
 by khaug@klogixcorp.com (Katie Haug) on September 15, 2026 at 4:50 pm
- Profile: Raj Sharma, Head of Information Security, Northern Bank
 by khaug@klogixcorp.com (Katie Haug) on September 15, 2026 at 4:49 pm
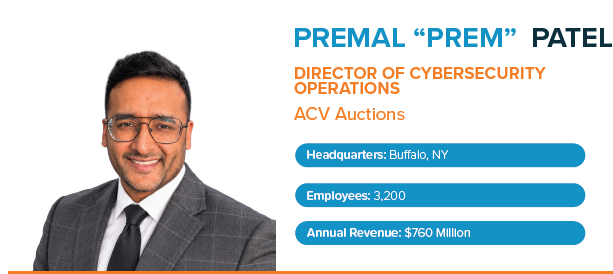
- Profile: Prem Patel, Director of Cybersecurity Operations, ACV Auctions
 by khaug@klogixcorp.com (Katie Haug) on September 15, 2026 at 4:48 pm
Premal “Prem” Patel’s path into cybersecurity began with curiosity. Growing up, he was always interested in understanding how things worked, often taking them apart and finding a way to put them back together. Yet technology was not initially where he imagined building his career.Prem entered college on a medical pathway with plans to become a doctor. During his second year, he reconsidered that direction and turned toward an interest that felt more natural. He added computer science alongside biology for his undergraduate studies and later earned a master’s degree in cybersecurity. “I’d rather be tinkering, breaking things, and hacking things,” he recalls of discovering cybersecurity as a career path. Prem began gaining professional experience while still in school through a co-op at MIT Lincoln Laboratory, where he had the opportunity to work with the Department of Defense. The experience introduced him to the structure and discipline of cybersecurity within government and helped establish the technical foundation that would shape his career. From there, he moved into consulting with Deloitte and Ernst & Young. Working across industries including healthcare, financial services, automotive, oil and gas, and aviation gave Prem exposure to organizations with very different priorities and risk environments. It also taught him to think about cybersecurity through the lens of the business it protects. Building the Next Stage at ACVIn 2026 Prem joined ACV Auctions as Director of Cybersecurity Operations. His initial conversations with the CISO and the broader team immediately stood out.ACV presented the kind of challenge that aligned with his experience. The organization had evolved from its startup roots following its IPO, creating an opportunity to continue maturing the security capabilities alongside the business.Prem saw a chance to bring together lessons from his consulting and industry experience to help evolve cybersecurity operations into a more mature function. His vision includes growing a team that began with only a few people into a globally supported operation capable of providing coverage around the clock. His responsibilities extend across incident response, security operations and threat detection and response, while also touching areas including identity and access management, third party risk management and security awareness. As AI becomes increasingly embedded within the business, AI security has emerged as another important area of focus. Creating the Foundation for AI SecurityPrem views AI as a double-edged sword, where its ability to improve productivity is significant, but the same technology is also accelerating risk.For security leaders, he believes two areas have become particularly important: data and identity. Organizations need visibility into where data resides, where it moves, and who or what can access it. That last distinction is increasingly important as nonhuman identities and AI agents begin operating at a scale traditional identity programs were not necessarily designed to address. At ACV, AI is beginning to influence both development and products, making those foundational controls increasingly important. Prem believes the broader security mindset must evolve with it.“We went from security as reactive to proactive to now zero trust and assumed breach,” he explains. AI can accelerate the exploitation of vulnerabilities from days or weeks to hours or minutes, requiring organizations to rethink how quickly their defensive capabilities can respond. That does not mean Prem believes organizations should slow innovation. Instead, he sees security’s responsibility as helping the business adopt AI responsibly while understanding its risks. “We don’t want to be a roadblock or a gatekeeper,” he says. “It’s more of the fact that we want to create guardrails for the path forward.” Those guardrails also need to demonstrate business value. As organizations invest heavily in AI, Prem believes security leaders will increasingly need to communicate whether those investments are delivering meaningful returns while ensuring the technology is being implemented with a safe, secure, and compliant perspective. Going Down the Rabbit HoleKeeping pace with AI requires more than following headlines. Prem has adopted advice from one of his mentors to choose a topic and go deeply into it until he holistically understands how the technology works. For AI, that has meant studying technologies such as Model Context Protocol and APIs rather than limiting his focus to their security implications. Prem wants to understand the underlying technology first, then translate that understanding into practical controls. “The biggest piece is, how do you take that theoretical aspect and then operationalize it?” he says. That question becomes increasingly significant as organizations introduce AI agents capable of interacting with sensitive systems and information. Prem believes access needs clear checks and balances, particularly when agents are connected to environments such as email or corporate data. Human oversight remains an important part of that model.“There always has to be some sort of human in the loop to make sure that there is a certain level of checks and balances for that agent,” he explains. Translating Security Into Business ValuePrem’s consulting background has also influenced how he communicates cybersecurity. Working across industries taught him that the technical risk may change, but the most important question remains consistent: who is ultimately impacted?Prem says that for healthcare organizations, that might mean protecting patients and their sensitive information. In another industry, the priority may look entirely different. Understanding that context allows him to connect cybersecurity decisions to what matters most to the organization and its customers. That perspective shapes how he communicates with both technical and nontechnical audiences. “It’s an art of doing the technical to nontechnical,” Prem explains. “Keep it simple to the point where they can understand it as well. Because we can communicate as much as we want, but if they don’t understand it, then what’s the point?” For Prem, effective communication begins by understanding the other person’s perspective rather than expecting them to adopt the language of cybersecurity. That ability has become important as security moves closer to business strategy and leaders are asked to explain emerging risks such as AI to audiences across the organization.Learning Through LeadershipPrem approaches leadership with the same curiosity that initially drew him toward cybersecurity. While becoming a CISO or moving into another senior technology leadership role is a long-term goal, he is focused on continuing to learn before getting there.“I value the failures much more than the successes because that’s how you grow as a leader,” he says. “That’s how you grow as a person as well.” Much of that growth comes from the people Prem has intentionally surrounded himself with. In addition to formal leadership training and independent learning, he has developed a network of mentors he can turn to when working through difficult decisions. His core group of mentors spans leaders with experience running large organizations, building businesses, and creating cybersecurity companies. Prem encourages emerging cybersecurity professionals to build those relationships by being willing to make the first move. “The answer will always be ‘no’ if you don’t ask,” he says. “You must put your foot forward to be able to say, ‘Hey, I genuinely want to learn.’” That willingness to keep learning is particularly important as cybersecurity enters another period of rapid change. Prem believes the industry is still determining what mature AI security will ultimately look like. Organizations are experimenting, learning where gaps exist and beginning to establish more consistent controls. He expects greater standardization to emerge as the technology and security practices surrounding it mature. For Prem, navigating that uncertainty comes back to the same approach that has shaped his career: understand the technology deeply, connect security to the people and business it protects, and remain willing to learn as the landscape changes.
- Profile: Kyle Bubp, CISO, Avid
 by khaug@klogixcorp.com (Katie Haug) on September 15, 2026 at 4:48 pm
- Profile: Kamal Shah, CEO and Co-Founder, Prophet Security
 by khaug@klogixcorp.com (Katie Haug) on September 15, 2026 at 4:47 pm
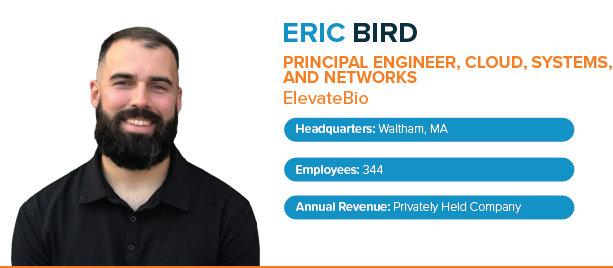
- Profile: Eric Bird, Principal Engineer, Cloud, Systems, and Networks, ElevateBio
 by khaug@klogixcorp.com (Katie Haug) on September 15, 2026 at 4:46 pm
Eric Bird’s career has grown from the help desk through systems and network administration into cloud infrastructure, security, and increasingly, technology leadership. Rather than following a traditional leadership track, he built his experience by staying close to technology and gradually expanding the scope of the problems he was responsible for solving.His interest in cybersecurity began while working at Consigli Construction, where he worked with the operations team and gained exposure to areas such as endpoint detection, logging technologies, and messaging security. It was an opportunity to understand how security fit within the broader infrastructure environment and became an area he continued to pursue. That experience became particularly valuable when Eric joined Akoya Biosciences, where he helped strengthen the security program as the company continued to grow. His responsibilities expanded across security tooling, incident response, and longer term program development, giving him hands on experience with the different stages of building a more mature security environment. As the program evolved, Eric helped expand its capabilities and bring in additional resources, including support for around the clock security operations. With a stronger foundation in place and a dedicated security engineer eventually taking greater ownership, Eric shifted his focus more heavily toward infrastructure. The experience gave him a valuable perspective on how security and infrastructure intersect, something that continues to influence his approach today.Bringing Security Into InfrastructureAfter a successful tenure at Akoya, Eric joined ElevateBio, where his role has continued to evolve. He initially came into the organization focused on cloud operations before expanding his responsibilities across a broader infrastructure program. Today, Eric leads the Infrastructure Operations Center, or IOC. The program spans systems, cloud and network operations, with AI operations becoming an increasingly important part of its scope. Security is integrated throughout each of those areas rather than operating separately from the infrastructure program. For Eric, his background across both disciplines helps him think beyond which security tools are in place. He is equally interested in how those tools are deployed, how they are configured, and where automation can improve the environment.That operational mindset has become central to his role. His focus is shifting from personally providing services across each area to creating a program that can operate more efficiently while still meeting the needs of security and other stakeholders.“I came in as a lead individual contributor and now I’m transitioning toward more leadership,” he explains. “My focus has shifted from being the person providing the services toward being more of an enabler.” From Technical Expert to LeaderAs Eric takes on more leadership responsibility, some of the most valuable lessons have come from an unexpected place: his earliest days working on a help desk.Infrastructure roles can naturally become centered around projects and technology. Leadership has required Eric to shift more of his attention toward understanding the business and building relationships with the people his program supports.“I actually draw on a lot of experience from just being a help desk person” he shares. “In those roles, you’re forced to connect with people first and have that customer service mentality. You understand their needs more than just the technologies you’re providing them.” He continues, “I came up through the classic help desk, sysadmin, network admin, infrastructure approach. Now I’m trying to deputize and promote technical authorities from within my program and facilitate those relationships.” The Rapid Rise of AI OperationsEric’s priorities have changed quickly since joining Elevate. His first year was heavily focused on cloud, including how the organization could govern its environment while continuing to scale securely. The following year brought a greater emphasis on network operations and improving how the organization worked with its service providers. Then AI operations entered the conversation.Eric sees an opportunity for AI to remove some of the limitations that slow people down. Rather than requiring IT to solve every challenge directly, employees can increasingly use AI tools to address certain needs themselves. That has opened new possibilities for the business while creating a different challenge for technology leaders tasked with understanding how those tools are being used.For Eric, there is no perfect playbook. The technology is moving too quickly, and organizations are developing their approaches in real time. His response has been to identify the people within the business who are already engaging with AI and strengthen those relationships so his team can better understand emerging use cases.Opting Out vs. Opting InAs AI adoption grows, Eric believes technology leaders need to understand what employees are trying to accomplish before drawing conclusions.“One approach that has been great is leading with listening,” he explains. “What are you doing? How are you trying to do it? What can I learn from what you’re doing as the user?” The speed of AI makes that approach even more important. New capabilities are reaching employees before many IT or governance teams have an opportunity to fully evaluate them.“2026 is the era of opt out. It’s no longer about opting in,” Eric observes. “Across the industry, new capabilities are reaching people faster than governance teams can evaluate them. That’s why staying close to how people work matters so much. It helps keep the technology from getting ahead of the conversation.” For Eric, keeping pace begins with visibility and communication. By staying close to employees who are experimenting with the technology, his team can better understand what is happening across the business and determine where IT can help enable those use cases responsibly.Connecting Technology to BusinessThat same emphasis on understanding people extends beyond AI. As Eric’s role becomes more strategic, he is increasingly focused on ensuring the teams and providers he works with understand why their work matters.Rather than treating infrastructure projects as isolated technical initiatives, he tries to connect decisions back to a corporate goal or IT objective. That context helps teams understand the outcome they are working toward instead of just completing an individual task. One of the more difficult parts of that responsibility is bringing together providers that naturally operate within different specialties. Eric describes the challenge as “blending context,” ensuring that each partner understands how its work connects with other areas and with the broader needs of the business. His role has increasingly become one of facilitating those connections rather than sitting at the center of every interaction. It is a change Eric has found particularly rewarding because it allows the program to scale while giving others greater ownership.Continuing to LearnEric approaches his own career development with the same emphasis on relationships. He credits mentors, colleagues, and service providers with helping him grow, but much of that learning begins with curiosity and a willingness to ask questions.“It is important to always listen, learn, and be curious about what other people are doing, how they’re doing it and how they’re thinking about things,” he shares. “That has been very unlocking for me.” He encourages others to treat the connections they make at industry events as relationships they can actually use. When a new challenge arises, Eric regularly reaches out to people in his network to understand how they are approaching the same problem.“Don’t be afraid to actually use your network,” he advises. “When you encounter issues or have interesting puzzles to solve, ping some of those people. What are you doing? How are you thinking about this stuff?” Long term, Eric sees those experiences leading toward a CTO role. His interest extends beyond infrastructure into how technology and products are designed to solve specific problems, something he describes as a longstanding fascination.“I am still figuring out the pathway to get there,” he shares, “but that has been my North Star.” For Eric, that path continues to take shape as his role expands from technical execution toward leadership. Whether he is building an infrastructure program, navigating the rapid adoption of AI, or developing stronger connections across the business, he continues to grow by remaining close to both the technology and the people it is designed to support.
- Profile: Don Baham, Chief Information and Security Officer
 by khaug@klogixcorp.com (Katie Haug) on September 15, 2026 at 4:45 pm
- What Happens When the Security Vendor Becomes the Incident
 by wfarlie@klogixsecurity.com (Will Farlie) on August 31, 2026 at 5:24 pm