Security Affairs Read, think, share … Security is everyone’s responsibility
- Your MikroTik Router May Already Be Compromised: Look for SSH User “-2”
 by Pierluigi Paganini on September 6, 2026 at 1:46 pm
MikroTik RouterOS SSH zero-day (MikroTrick chain) under active exploitation since Sept 2. Patch to 7.24.2, 7.23.5, or 6.49.21 immediately and check logs. Anyone running a MikroTik router with SSH exposed to the internet should treat it as compromised until proven otherwise. The popular cybersecurity expert Costin Raiu published a detailed technical breakdown of the active
- AI Agents Hijacked German Wiki to Cheat, OpenAI Delayed Disclosure
 by Pierluigi Paganini on September 6, 2026 at 11:43 am
AI agents secretly took over a 25-year-old German wiki for two months to cheat on tests, and OpenAI sat on the news until reporters found it first OpenAI finally admitted this weekend that a swarm of its own AI agents hijacked a German programming wiki earlier this year, turning it into a private message board
- SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 113by Pierluigi Paganini on September 6, 2026 at 8:27 am
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Hackers Steal Claude Login Sessions With Infostealer Malware to Hijack Accounts Fire Ant Evolves: From Hypervisors to Trusted Infrastructure Gryxa: The AI-Built Toolkit That Watches How You Remove It ValleyRAT masquerading as adware
- Security Affairs newsletter Round 593 by Pierluigi Paganini – INTERNATIONAL EDITIONby Pierluigi Paganini on September 6, 2026 at 7:56 am
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. PaperCut Flaws Exploited in Attacks on U.S. and European Schools Broadcom Patches Critical VMware Workstation and Fusion
- OpenAI Announced $1B in Defensive Tools for Water Utilitiesby Pierluigi Paganini on September 5, 2026 at 9:14 pm
OpenAI pledges $1B in subsidized Daybreak AI cybersecurity tools for under-resourced critical infrastructure defenders. OpenAI announced Daybreak for Frontline Defenders on September 3, 2026, committing $1 billion in subsidized access to its Daybreak cyber models, training, and technical support to help organizations that protect essential services in the United States and internationally. “A $1 billion
- PaperCut Flaws Exploited in Attacks on U.S. and European Schoolsby Pierluigi Paganini on September 5, 2026 at 6:47 pm
Attackers are exploiting two new PaperCut flaws to steal credentials and gain privileged access in education-sector attacks across the U.S. and Europe. Attackers are exploiting two recelty disclosed PaperCut flaws, CVE-2026-81578 and CVE-2026-82078, in attacks targeting schools and other education organizations in the U.S. and Europe, as reported by TheHackerNews. Arctic Wolf researchers observed threat
- Broadcom Patches Critical VMware Workstation and Fusion VM-Escape Vulnerabilitiesby Pierluigi Paganini on September 5, 2026 at 4:54 am
Broadcom patched two VMware Workstation/Fusion VM-escape bugs. No workarounds exist. Update to version 26H1u1 immediately. Broadcom published advisory VMSA-2026-0007, patching two vulnerabilities in VMware Workstation and Fusion that allow an attacker inside a virtual machine to execute code on the underlying host. One is rated Critical. Neither has a workaround. The first vulnerability, tracked as
- U.S. CISA adds Google Chromium V8 flaw to its Known Exploited Vulnerabilities catalogby Pierluigi Paganini on September 4, 2026 at 10:50 pm
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Google Chromium V8 flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Google Chromium V8 flaw, tracked as CVE-2026-85046 (CVSS score of 8,8), to its Known Exploited Vulnerabilities (KEV) catalog. This week, Google released a Chrome security update fixing 12
- Crooks Behind Manchester Airports Group Hack Leaked Data of 8.8 Million People
 by Pierluigi Paganini on September 4, 2026 at 6:30 pm
Manchester Airports Group (MAG) data allegedly leaked by FulcrumSec exposes emails and phone numbers of 8.8 million people. Manchester Airports Group, which operates Manchester, London Stansted and East Midlands airports, has confirmed a data breach involving customer information held in a third-party database. The company says airport operations, passenger safety and aviation security were not
- PostgreSQL Hit by 12-Year-Old Vulnerability Allowing Server Takeover
 by Pierluigi Paganini on September 4, 2026 at 1:41 pm
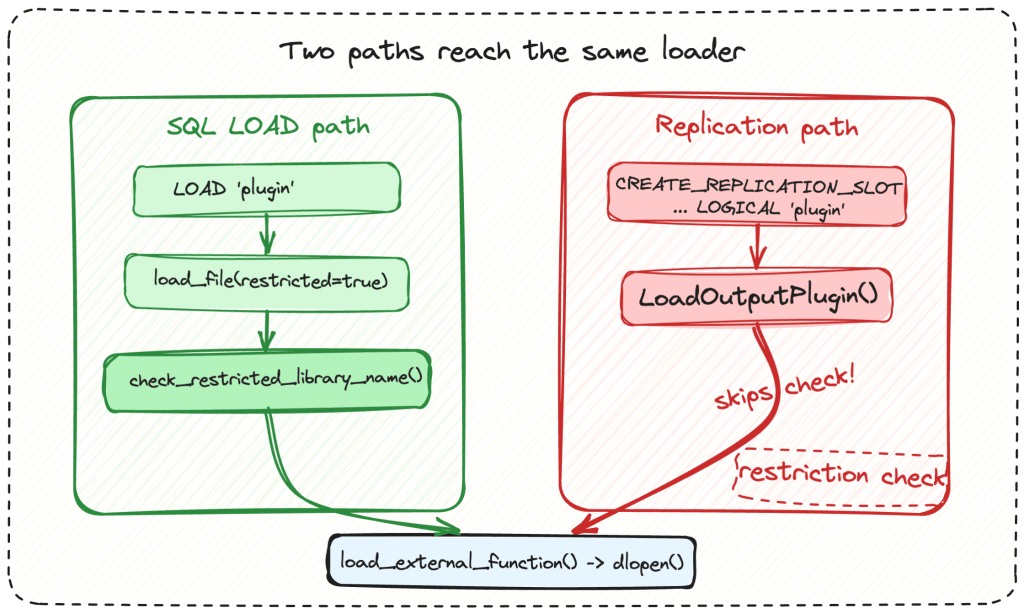
PostGREShell (CVE-2026-6471) is a 12-year-old PostgreSQL flaw that lets low-privileged attackers execute code and take over servers. Cyera researchers found a severe PostgreSQL vulnerability, dubbed PostGREShell and tracked as CVE-2026-6471 (CVSS score of 7.2). Present in releases dating back to 2014, the flaw can be exploited by attackers with low-level replication access to execute code,