Cyber Exposure Alerts From Tenable
- Microsoft’s October 2026 Patch Tuesday addresses 1407 CVEs (CVE-2026-96951)
 by Research Special Operations on October 13, 2026 at 5:49 pm
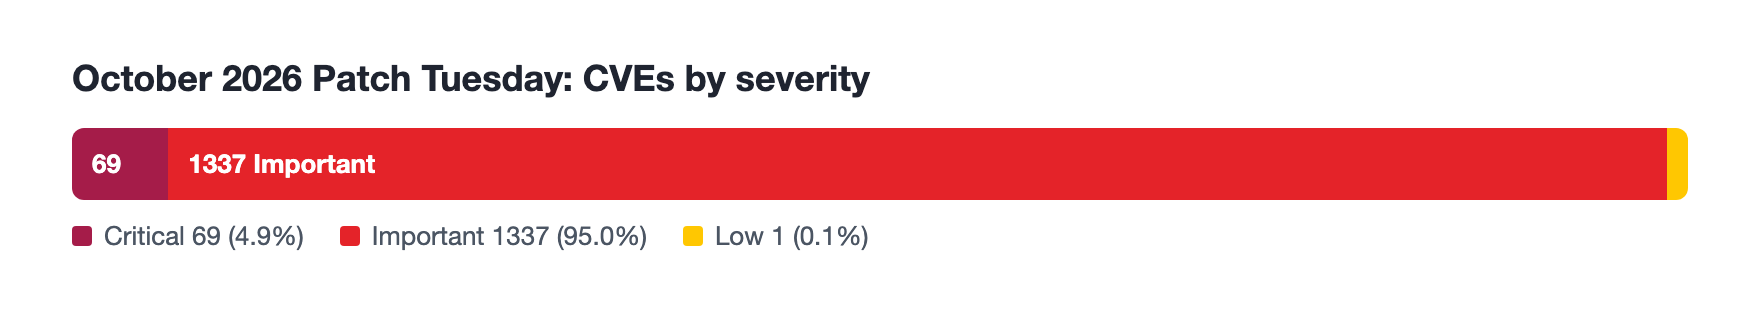
69Critical1337Important0Moderate1LowMicrosoft addresses 1407 CVEs in the tenth Patch Tuesday of 2026, marking the second consecutive month to reset the bar as the largest Patch Tuesday release. This month’s updates include patches for two zero days, including one that was exploited in the wild.Microsoft patched 1,407 CVEs in its October 2026 Patch Tuesday release, with 69 rated critical, 1,337 rated as important, and one rated as low.This month’s update includes patches for 301 products and components. The following table lists the products with the most CVEs patched this month. A full list of patched products is available in the appendix.RankProductCVE Count1Microsoft Office Excel692Role: DNS Server523Windows Kernel464Windows Installer385Windows Win32 Kernel Subsystem366Microsoft Office SharePoint347Microsoft Windows Search Component298Windows NTFS269.NET2510 (Tie)Microsoft Office Word2210 (Tie)SQL Server2210 (Tie)Windows Error Reporting22Elevation of Privilege (EoP) vulnerabilities accounted for 47.9% of the vulnerabilities patched this month, followed by remote code execution (RCE) vulnerabilities at 22.3%.ImportantCVE-2026-96951 | Windows Shell security feature bypass vulnerabilityCVE-2026-96951 is a security feature bypass vulnerability affecting Windows Shell. It received a CVSSv3 score of 8.8 and was rated as important. According to Microsoft, this vulnerability was exploited in the wild as a zero-day.An attacker could exploit this vulnerability using social engineering tactics, via email or messages, to convince their target to open a malicious file. Successful exploitation would bypass the Mark of the Web (MOTW) security feature.This is the third flaw in Windows Shell that was exploited in the wild in 2026: CVE-2026-21510 was patched in February 2026’s Patch Tuesday while CVE-2026-32202 was patched in April 2026’s Patch Tuesday.ImportantCVE-2026-108398 |.NET Framework security feature bypass vulnerabilityCVE-2026-108398 is a security feature bypass vulnerability affecting.NET Framework. It received a CVSSv3 score of 8.8 and is rated as important. It was publicly disclosed prior to a patch being available.An attacker could exploit this vulnerability by registering a malicious.NET assembly on a vulnerable system to be loaded by a protected process. Successful exploitation would allow the attacker to bypass Windows Defender Application Control (WDAC).CriticalCVE-2026-70229 | Windows Active Directory Domain Services remote code execution vulnerabilityCVE-2026-70229 is an RCE vulnerability affecting Windows Active Directory Domain Services (AD DS). It received a CVSSv3 score of 8.1 and is rated as critical. Microsoft assesses this vulnerability as “Exploitation More Likely” according to Microsoft’s Exploitability Index.An attacker could exploit this vulnerability by sending a crafted packet to the vulnerable AD DS service. Successful exploitation could grant an attacker code execution on the vulnerable system.ImportantCVE-2026-70279 | Microsoft Exchange Server spoofing vulnerabilityCVE-2026-70279 is a spoofing vulnerability affecting Microsoft Exchange Server. It received a CVSSv3 score of 9.3 and is rated as important. It was assessed as “Exploitation More Likely.” An attacker could exploit this vulnerability by convincing a target through social engineering to click on a malicious link. Successful exploitation against a target with administrative privileges would allow an attacker to access or modify organizational data.CriticalCVE-2026-70571 | Microsoft Exchange Server remote code execution vulnerabilityCVE-2026-70571 is a remote code execution vulnerability affecting Microsoft Exchange Server. It received a CVSSv3 score of 8.1 and is rated as critical. It was assessed as “Exploitation More Likely.”An attacker could exploit this vulnerability by sending a malicious email to a vulnerable Microsoft Exchange server that would cause it to process the email using internal content-conversion. Successful exploitation would allow an attacker the ability to execute code on the Exchange server.Additional notable CVEsThe following CVEs also merit attention based on severity, exploitability, or CVSSv3 score:CVEProductImpactCVSSv3ExploitabilityNotesCVE-2026-100214Dynamics Business CentralRemote Code Execution8.8Exploitation More LikelyImportantCVE-2026-102217WebDAVElevation of Privilege8.8Exploitation More LikelyImportantCVE-2026-69918Windows Core MessagingElevation of Privilege8.8Exploitation More LikelyImportantCVE-2026-88159Windows Background Intelligent Transfer Service (BITS)Remote Code Execution8.8Exploitation More LikelyImportantCVE-2026-96940Microsoft Exchange ServerElevation of Privilege8.8Exploitation More LikelyImportantCVE-2026-69673Windows UpdateElevation of Privilege7.8Exploitation More LikelyImportantCVE-2026-69718Windows UpdateElevation of Privilege7.8Exploitation More LikelyImportantCVE-2026-69733Windows UpdateElevation of Privilege7.8Exploitation More LikelyImportantCVE-2026-69783Windows UpdateElevation of Privilege7.8Exploitation More LikelyImportantCVE-2026-69880Desktop Window ManagerElevation of Privilege7.8Exploitation More LikelyImportantCVE-2026-69882Windows UpdateElevation of Privilege7.8Exploitation More LikelyImportantCVE-2026-69923Windows AIElevation of Privilege7.8Exploitation More LikelyImportantCVE-2026-69926Desktop Window ManagerElevation of Privilege7.8Exploitation More LikelyImportantCVE-2026-70054Windows NetBIOSElevation of Privilege7.8Exploitation More LikelyImportantWindows Server 2012 End of SupportOn October 13, the final year of Extended Security Updates (ESU) for Windows Server 2012 and Windows Server 2012 R2 ended. Microsoft will no longer release security updates for either version. To identify unsupported versions of Windows Server 2012, customers can use plugin ID 192813. To check the ESU status of Windows Server 2012 and 2012 R2 hosts, customers can use plugin ID 182965.Extended support for Windows 10 Enterprise 2016 Long-Term Servicing Branch (LTSB) and Windows 10 IoT Enterprise LTSB 2016 also ended on October 13. To identify Windows 10 Enterprise 2016 LTSB, customers can use plugin ID 192817.Windows Server 2022 End of Mainstream SupportOctober 13, 2026 marks the end of mainstream support for Windows Server 2022. This month’s security update is the last one issued under mainstream support. The product now enters extended support, where it will continue receiving monthly security updates at no additional cost through October 14, 2031. Organizations still running Windows Server 2022 can begin evaluating an upgrade path to Windows Server 2025, the current LTSC release, which carries mainstream support through November 2029 and extended support through November 2034.Additional Microsoft Products End of SupportAs of October 13, several Microsoft products have reached end of support. Since these products will no longer receive security updates, we recommend upgrading to supported versions as soon as possible.Office 2021Office LTSC 2021Office LTSC 2021 for MacSkype for Business LTSC 2021Windows 11 Home and Pro Version 24H2Tenable solutionsA list of all the plugins released for Microsoft’s October 2026 Patch Tuesday update can be found here. As always, we recommend patching systems as soon as possible and regularly scanning your environment to identify those systems yet to be patched.For more specific guidance on best practices for vulnerability assessments, refer to our blog post on How to Perform Efficient Vulnerability Assessments with Tenable.Product Appendix.NET.NET Framework.NET and Visual StudioASP.NET CoreActive Directory Certificate Services (AD CS)Active Directory Domain ServicesActive Directory Federation Services (AD FS)Azure Active DirectoryAzure ArcAzure CycleCloudAzure DevOpsAzure HDInsightAzure Key VaultAzure Storage LibraryConnected Devices Platform Service (Cdpsvc)Desktop Window ManagerDynamics Business CentralFunction Discovery Service (fdwsd.dll)Graphic FontsHID Parser LibraryHID class driverInternet ExplorerLinux KernelMicrosoft AccountMicrosoft Azure Attestation service and Device Health Attestation ServiceMicrosoft Bluetooth DriverMicrosoft COM for WindowsMicrosoft Configuration ManagerMicrosoft DefenderMicrosoft Defender for EndpointMicrosoft Digest AuthenticationMicrosoft Exchange ServerMicrosoft Failover Cluster Virtual DriverMicrosoft Graphics ComponentMicrosoft Input Method Editor (IME)Microsoft Internet Messaging APIMicrosoft Local Security Authority Server (lsasrv)Microsoft MPEG-2 Video ExtensionMicrosoft OfficeMicrosoft Office AccessMicrosoft Office Click-To-RunMicrosoft Office ExcelMicrosoft Office OneNoteMicrosoft Office OutlookMicrosoft Office PowerPointMicrosoft Office SharePointMicrosoft Office VisioMicrosoft Office WordMicrosoft PostScript Printer DriverMicrosoft Power AppsMicrosoft PowerShellMicrosoft PowerToysMicrosoft QUICMicrosoft Scripting EngineMicrosoft Streaming ServiceMicrosoft Trace Data HelperMicrosoft Windows Codecs LibraryMicrosoft Windows Media FoundationMicrosoft Windows PDFMicrosoft Windows Search ComponentMicrosoft XMLNetwork Device Enrollment Service (NDES)Network Policy Server (NPS)OpenSSH for WindowsPythonQuality Windows Audio/Video Experience (QWAVE) serviceRPC Endpoint Mapper ServiceRPC RuntimeReliable Multicast Transport Driver (RMCAST)Remote Access Point-to-Point Protocol (PPP) EAP-TLSRemote Desktop ClientRemote Desktop Display DriverRemote Desktop Gateway ServiceRole: DNS ServerSQL ServerSQLiteServicing Stack UpdatesSkype for Business and Microsoft LyncSoftware Protection Platform (SPP)SysInternalsVirtual Hard Disk (VHD) Miniport DriverVisual Studio CodeVisual Studio Tools for Applications and SQL Server Management StudioWebDAVWindows AIWindows ALPCWindows Advanced Rasterization PlatformWindows Aggregated Data Platform ServiceWindows Ancillary Function Driver for WinSockWindows AppX Deployment ExtensionsWindows AppX Deployment ServiceWindows Application Compatibility CacheWindows Assigned AccessWindows Audio ServiceWindows AutopilotWindows Background Intelligent Transfer Service (BITS)Windows Backup EngineWindows Bind Filter DriverWindows Biometric ServiceWindows BitLockerWindows Bluetooth A2DP driverWindows Bluetooth Port DriverWindows Bluetooth ServiceWindows Broadcast DVR User ServiceWindows CCFFilter DriverWindows CD-ROM DriverWindows COM+ Event System ServiceWindows Camera Frame Server MonitorWindows Cash Drawer Protocol ProviderWindows CertificatesWindows Client License ServiceWindows Client Side Caching driver (csc.sys)Windows Client for NFSWindows Client-Side Caching (CSC) ServiceWindows Clipboard ServerWindows Clipboard User ServiceWindows Cloud Files Mini Filter DriverWindows Common Log File System DriverWindows Composite Image File SystemWindows Connected Devices Platform ServiceWindows Connected User Experiences and TelemetryWindows Console DriverWindows Container Isolation FS Filter DriverWindows Container Isolation FS Filter Driver (unionfs.sys)Windows Core MessagingWindows Credential GuardWindows Credential ManagerWindows Credential ProvidersWindows Cryptographic ServicesWindows DCOM ServerWindows DHCP ClientWindows DHCP ServerWindows DNSWindows DWM Core LibraryWindows Defender Firewall ServiceWindows Deployment ServicesWindows Device Association ServiceWindows Device Install ServiceWindows Diagnostic Policy ServiceWindows Direct CompositionWindows Distributed File System (DFS)Windows EAPHost ServiceWindows Embedded Mode ServiceWindows Encrypting File System (EFS)Windows Enterprise App ManagementWindows Error ReportingWindows Event Logging ServiceWindows Event TracingWindows Event ViewerWindows Failover ClusterWindows Fast FAT DriverWindows Fax and Scan ServiceWindows GDIWindows GDI+Windows Geotag BrokerWindows Graphics KernelWindows Group PolicyWindows HTTP.sysWindows Health and Optimized Experiences ServiceWindows HelloWindows Host Guardian ServiceWindows Hyper-VWindows IKE ExtensionWindows IP Over USB ServiceWindows Image AcquisitionWindows Imaging ComponentWindows Input SystemWindows InstallerWindows Internal System User ProfileWindows Internet (wininet.dll)Windows Internet Connection Sharing (ICS)Windows Internet Information ServicesWindows Internet Key Exchange (IKE) ProtocolWindows KerberosWindows KernelWindows Kernel Mode DriverWindows Kernel-Mode DriversWindows Key Distribution CenterWindows Key Storage ProviderWindows LibarchiveWindows Local Security Authority (LSA)Windows Local Security Authority Subsystem Service (LSASS)Windows MIDI Service ModuleWindows Management InstrumentationWindows Management ServicesWindows MediaWindows Media PlayerWindows Media Video DecoderWindows Message QueuingWindows Message Queuing Queue ManagerWindows Mobile BroadbandWindows Mobile Device ManagementWindows Modern Device Management (MDM)Windows NDISWindows NTFSWindows NTLMWindows NetBIOSWindows NetlogonWindows Network File SystemWindows Network List ServiceWindows Network Load BalancingWindows NotificationWindows Now Playing Session ManagerWindows OLEWindows OLE DBWindows Overlay FilterWindows PCI Bus DriverWindows PaintWindows Partition Management DriverWindows Perception Simulation ServiceWindows Performance MonitorWindows Phone ServiceWindows Portable Device Enumerator ServiceWindows Portable Device File System DriverWindows Portable Device MTP DriverWindows PowerShellWindows Print Spooler ComponentsWindows Program Compatibility Assistant ServiceWindows Projected File SystemWindows Push NotificationsWindows Quality of Service (QoS) Packet SchedulerWindows RNDISWindows Raw Image ExtensionWindows RegistryWindows Remote Access Connection ManagerWindows Remote Access Service InfrastructureWindows Remote DesktopWindows Remote Desktop ProtocolWindows Remote Desktop ServicesWindows Remote POS DriverWindows Resilient File System (ReFS)Windows Resilient File System (ReFS) Deduplication ServiceWindows Resource Management (MRM)Windows ResumeWindows Rich Text Edit ControlWindows Routing and Remote Access Service (RRAS)Windows SMB ClientWindows SMB ServerWindows SchannelWindows Secure BootWindows Secure Kernel ModeWindows Secure Socket Tunneling Protocol (SSTP)Windows Security Account ManagerWindows Security AppWindows Security CenterWindows Security Support Provider InterfaceWindows Sensor Data ServiceWindows Server Update ServiceWindows Server for NFSWindows Setup Files CleanupWindows Setup and DeploymentWindows ShellWindows Smart CardWindows SmartScreenWindows Spaceport.sysWindows StateRepository APIWindows StorageWindows Storage Port DriverWindows Storage Spaces ControllerWindows Storage VSP DriverWindows Storport Miniport DriverWindows Subsystem for LinuxWindows Sysmain ServiceWindows System Information ConsoleWindows TCP/IPWindows Telephony ServerWindows Text Services FrameworkWindows Text ShapingWindows UEFIWindows UI Immersive ServerWindows USB DriverWindows USB Print DriverWindows USB Video DriverWindows Universal Disk Format File System Driver (UDFS)Windows Universal Plug and Play (UPnP) Device HostWindows UpdateWindows Update Delivery OptimizationWindows Update Orchestrator ServiceWindows Update ServiceWindows Update StackWindows User Profile ServiceWindows VHD miniport driverWindows VMSwitchWindows Virtual InputWindows Virtualization-Based Security (VBS) EnclaveWindows Volume Manager Extension DriverWindows WLAN ServiceWindows WalletServiceWindows Web Account ManagerWindows Wi-Fi DriverWindows Win32 Kernel SubsystemWindows Win32KWindows Win32K – GRFXWindows Win32K – ICOMPWindows Wired AutoConfig ServiceWindows Work FoldersWindows Workstation ServiceWindows exFAT File SystemWindows iSCSIWindows kernel32.dllWinlogonGet more informationMicrosoft’s October 2026 Security UpdatesTenable plugins for Microsoft October 2026 Patch Tuesday Security Updates
- Frequently asked questions about reported Citrix NetScaler zero-day vulnerabilities
 by Satnam Narang on September 27, 2026 at 5:35 am
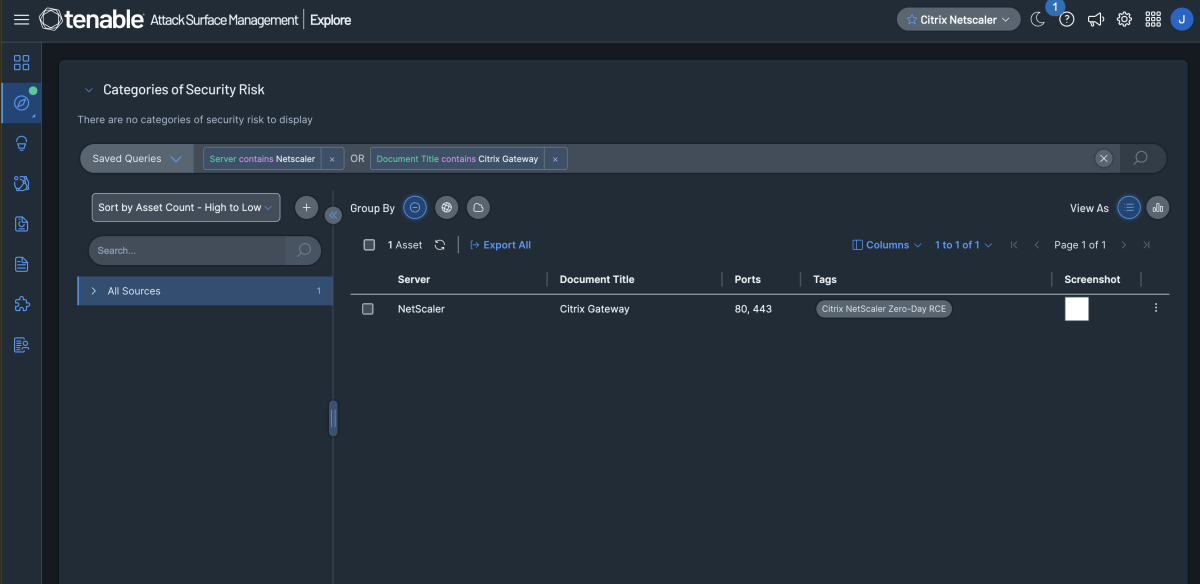
CVE-2026-88771 and CVE-2026-88772, two zero-day vulnerabilities in Citrix NetScaler, have been confirmed as exploited in the wild. Citrix released patches on September 27, 2026. On October 3, Citrix disclosed CVE-2026-88779, an exploited denial of service flaw affecting SAML deployments. Fixing it requires newer builds.Change logUpdate October 4: On October 3, Citrix published security bulletin CTX697174 with fixed versions for CVE-2026-88779, an exploited denial of service vulnerability affecting NetScaler deployments configured for SAML. Post updated with details on CVE-2026-88779, findings from Mandiant and Google Threat Intelligence Group (GTIG) on the exploitation of CVE-2026-88772, CISA KEV additions, public proof-of-concept tooling, and expanded mitigation and hunting guidance.Click here to review the change log historyUpdate October 4: On October 3, Citrix published security bulletin CTX697174 with fixed versions for CVE-2026-88779, an exploited denial of service vulnerability affecting NetScaler deployments configured for SAML. Post updated with details on CVE-2026-88779, findings from Mandiant and Google Threat Intelligence Group (GTIG) on the exploitation of CVE-2026-88772, CISA KEV additions, public proof-of-concept tooling, and expanded mitigation and hunting guidance.Update September 27: Citrix published security bulletin CTX697096, confirming CVE-2026-88771 and CVE-2026-88772 as the two zero-day RCE vulnerabilities and releasing patches. Post updated with CVE IDs, CVSS scores, patch versions, and IoC guidance.September 27: Original publication based on limited public information ahead of Citrix’s official advisory.Key takeawaysCitrix has confirmed two critical zero-day vulnerabilities in NetScaler ADC and NetScaler Gateway, both capable of remote code execution and actively exploited in the wild. A third vulnerability, CVE-2026-88779, can cause denial of service on SAML-enabled deployments and has also been exploited.Citrix released patches on September 27, 2026, and newer builds on October 3, 2026. Organizations that use SAML and already upgraded to the September 27 builds need to upgrade again. Citrix recommends that every customer move to the newest builds.According to Mandiant and Google Threat Intelligence Group (GTIG), exploitation of CVE-2026-88772 began no later than early September. Organizations should check for signs of compromise and preserve evidence before patching.BackgroundTenable’s Research Special Operations (RSO) team has compiled this blog to answer Frequently Asked Questions (FAQ) regarding zero-day vulnerabilities in Citrix NetScaler that have been exploited in the wild. The following FAQ was originally based on limited public information and has been updated as Citrix and security researchers published details. This post was last updated on October 4, 2026 following publication of the Citrix security bulletin for CVE-2026-88779.Security researcher Kevin Beaumont dubbed this incident “PitScaler” on September 28, and the name has since appeared in press coverage of CVE-2026-88771 and CVE-2026-88772. An independent website, PitScaler, tracks the incident and collects government advisories and published research in one place.FAQWhat is the source of the NetScaler vulnerabilities?On September 25, 2026, reports surfaced through a reddit post on r/Citrix regarding advice to shut down “Netscalers.” This included a report from a user that said this information came from the “Dutch national cyber security center” and further details included a note about two zero-day vulnerabilities.On September 26, 2026, additional reports confirming the existence of these flaws became public, including social posts from researchers at watchTowr on X, as well as Kevin Beaumont on Mastodon.What is the context surrounding the Dutch National Cyber Security Centre (NCSC-NL) alert?The Reddit post on r/Citrix cited details from an NCSC-NL pre-notification that had not yet been made public. Community members in that thread said the pre-notification was distributed under Traffic Light Protocol (TLP):AMBER+STRICT restrictions. Tenable’s RSO has not independently obtained or reviewed the contents of this notification.Has Citrix confirmed the presence of zero-day vulnerabilities?Yes. Citrix published a security bulletin (CTX697096) on September 27, 2026, confirming two zero-day vulnerabilities and noting that both CVEs have been observed being exploited against customer deployments.What are these zero-day vulnerabilities?Citrix has confirmed two zero-day vulnerabilities in NetScaler ADC and NetScaler Gateway. CVE-2026-88771 affects all deployments, including default configurations. CVE-2026-88772 only affects appliances with Datagram Transport Layer Security (DTLS) turned on, which VPN virtual servers have out of the box.CVEDescriptionCVSSv4CVE-2026-88771Citrix NetScaler ADC and NetScaler Gateway Improper Input Validation vulnerability9.5CVE-2026-88772Citrix NetScaler ADC and NetScaler Gateway Memory Overflow vulnerability9.5Analysis by Mandiant and GTIG suggests attackers exploit CVE-2026-88772 by sending malformed DTLS traffic to the appliance, which gives them root-level access.Citrix also addressed six additional vulnerabilities affecting various configurations:CVEDescriptionCVSSv4CVE-2026-88773Citrix NetScaler ADC and NetScaler Gateway HTTP Request Smuggling vulnerability9.3CVE-2026-88774Citrix NetScaler ADC and NetScaler Gateway Feature Policy Bypass vulnerability7.0CVE-2026-88775Citrix NetScaler ADC and NetScaler Gateway Memory Overflow vulnerability8.8CVE-2026-88776Citrix NetScaler ADC and NetScaler Gateway Memory Overflow vulnerability8.8CVE-2026-88777Citrix NetScaler ADC and NetScaler Gateway Memory Overflow vulnerability8.8CVE-2026-88778Citrix NetScaler ADC and NetScaler Gateway TCP ISN Prediction vulnerability8.8watchTowr originally confirmed details for the zero-days on September 26, 2026:We have been made aware of further info, which we are sharing. We had no idea Citrix sysadmins were like GTA6 fans – so friendly 🤗Please, direct further questions to Citrix. We are not Citrix PSIRT (despite it occasionally looking that way).Citrix comms & patches are… https://t.co/OemTXwG8PB— watchTowr (@watchtowrcyber) September 26, 2026What is CVE-2026-88779?CVE-2026-88779 is a memory overflow vulnerability in NetScaler ADC and NetScaler Gateway. Exploiting it can cause a denial of service. It received a CVSSv4 score of 8.7. Citrix disclosed it on October 3 in security bulletin CTX697174 and credited Bishop Fox and watchTowr in the bulletin.CVEDescriptionCVSSv4CVE-2026-88779Citrix NetScaler ADC and NetScaler Gateway Memory Overflow vulnerability8.7Citrix says it has “observed targeted attacks on unmitigated NetScaler deployments.” CISA added CVE-2026-88779 to its KEV catalog on October 4.Only appliances configured as a SAML service provider (SP) or SAML identity provider (IdP) are affected. Administrators can check their NetScaler configuration for either of the following entries:add authentication samlAction (SAML SP)add authentication samlIdPProfile (SAML IdP)According to Citrix, the flaw affects service availability, and so far it has found no impact on customer data integrity. In its October 3 update on the SAML issue, the Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC) says an attacker targeting this flaw “may induce system crashes, denial of service and potential exploitation,” and that Australian organizations have been affected.Are these zero-day vulnerabilities related to CVE-2026-19490 and CVE-2026-19489?No. Neither CVE-2026-19490 nor CVE-2026-19489 appears to be related. Both are previously disclosed NetScaler ADC and NetScaler Gateway flaws that already have patches. CVE-2026-19490 was added to CISA’s Known Exploited Vulnerabilities (KEV) catalog on September 9, 2026.Reports say these vulnerabilities were exploited. How widespread are the attacks?Mandiant and GTIG published findings on September 29 showing that CVE-2026-88772 has been exploited since at least early September. They observed evidence that organizations across government, education, technology, financial services, and legal and professional services in North America and Europe were likely affected. On September 30, ASD’s ACSC said it had received reports from Australian organizations confirming exploitation, and it recommends that organizations look for evidence of compromise dating back to at least September 4.On September 26, before patches were available, Kevin Beaumont stated: “The Netscaler zero day thing is real, being used in active attacks. No patch yet, if sensitive to Netscaler vulns switch it off.”How many Citrix NetScaler vulnerabilities have been exploited in the wild in the past?Citrix NetScaler devices have historically been a popular target for attackers. As of October 4, 2026, CISA’s KEV catalog had 18 entries for NetScaler ADC and NetScaler Gateway (including those listed under the former Citrix ADC name) and 27 entries for Citrix products overall, including CVE-2026-88771, CVE-2026-88772 and CVE-2026-88779. The RSO team has covered several notable incidents:CVEDescriptionKEV addedRansomwareTenable blogsCVE-2026-88779Citrix NetScaler ADC and NetScaler Gateway Memory Overflow vulnerability2026-10-04UnknownFrequently asked questions about reported Citrix NetScaler zero-day vulnerabilitiesCVE-2026-88772Citrix NetScaler ADC and NetScaler Gateway Memory Overflow vulnerability2026-09-27UnknownFrequently asked questions about reported Citrix NetScaler zero-day vulnerabilitiesCVE-2026-88771Citrix NetScaler ADC and NetScaler Gateway Improper Input Validation vulnerability2026-09-27UnknownFrequently asked questions about reported Citrix NetScaler zero-day vulnerabilitiesCVE-2026-8452Citrix NetScaler ADC and NetScaler Gateway Buffer Overflow vulnerability2026-08-26Unknown-CVE-2026-3055Citrix NetScaler Out-of-Bounds Read vulnerability2026-03-30Unknown-CVE-2025-7775Citrix NetScaler Memory Overflow vulnerability2025-08-26UnknownCVE-2025-7775: Citrix NetScaler ADC and NetScaler Gateway Zero-Day Remote Code Execution Vulnerability Exploited in the WildCVE-2025-5777Citrix NetScaler ADC and Gateway Out-of-Bounds Read vulnerability (“CitrixBleed 2”)2025-07-10KnownCVE-2025-5777, CVE-2025-6543: Frequently Asked Questions About CitrixBleed 2 and Citrix NetScaler ExploitationCVE-2025-6543Citrix NetScaler ADC and Gateway Buffer Overflow vulnerability2025-06-30UnknownCVE-2025-5777, CVE-2025-6543: Frequently Asked Questions About CitrixBleed 2 and Citrix NetScaler ExploitationCVE-2023-6549Citrix NetScaler ADC and NetScaler Gateway Buffer Overflow vulnerability2024-01-17UnknownCVE-2023-6548, CVE-2023-6549: Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC and NetScaler GatewayCVE-2023-6548Citrix NetScaler ADC and NetScaler Gateway Code Injection vulnerability2024-01-17UnknownCVE-2023-6548, CVE-2023-6549: Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC and NetScaler GatewayCVE-2023-4966Citrix NetScaler ADC and NetScaler Gateway Buffer Overflow vulnerability (“CitrixBleed”)2023-10-18Known[1] [2] [3]CVE-2023-3519Citrix NetScaler ADC and NetScaler Gateway Code Injection vulnerability2023-07-19KnownCVE-2023-3519: Critical RCE in Netscaler ADC (Citrix ADC) and Netscaler Gateway (Citrix Gateway)CVE-2020-8193Citrix ADC, Gateway, and SD-WAN WANOP Appliance Authorization Bypass vulnerability2021-11-03UnknownGovernment Agencies Warn of State-Sponsored Actors Exploiting Publicly Known VulnerabilitiesCVE-2019-19781Citrix ADC, Gateway, and SD-WAN WANOP Appliance Code Execution vulnerability2021-11-03Known[1] [2]Which threat actors are exploiting these vulnerabilities?No threat actor has been publicly named. In attacks exploiting CVE-2026-88772, Mandiant and GTIG identified two new malware families, WHIPSHOT and SLAPSHOT.For context, based on our research, roughly two-thirds of threat actor activity targeting Citrix NetScaler over the last seven years involved advanced persistent threat (APT) groups, while one-third involved ransomware groups and their affiliates.Is there a proof-of-concept (PoC) available for these vulnerabilities?Yes. watchTowr published technical analyses of CVE-2026-88771 and CVE-2026-88772, along with tools that demonstrate code execution for each. watchTowr released them to help defenders, but they also work as public PoCs, with some limitations. As of October 4, 2026, we are not aware of a public PoC for CVE-2026-88779.Are patches or mitigations available?Yes. Citrix urges customers running affected versions to install one of the updated versions. Organizations whose NetScaler appliances are configured for SAML need the newer builds released on October 3 to address CVE-2026-88779.Product BranchFixed Versions for CVE-2026-88771 through CVE-2026-88778Fixed Versions for CVE-2026-88779NetScaler ADC and NetScaler Gateway 14.114.1-73.37 and later14.1-73.41 and laterNetScaler ADC and NetScaler Gateway 13.113.1-64.23 and later13.1-64.28 and laterNetScaler ADC 14.1-FIPS14.1-73.37 FIPS and later14.1-73.41 FIPS and laterNetScaler ADC 13.1-FIPS and 13.1-NDcPP13.1-37.279 and later13.1-37.282 and laterCitrix says deployments affected by CVE-2026-88778 also need to turn on Enhanced ISN Generation in their TCP settings.Until organizations can install the newer builds, Citrix has released Global Deny List signatures that can help mitigate CVE-2026-88779 on standard (non-FIPS) 14.1 and 13.1 appliances that are already running the September 27 builds and managed through NetScaler Console. Citrix’s blog lists the requirements.For CVE-2026-88772, Mandiant suggests blocking inbound UDP port 443 at an upstream firewall and turning off DTLS on gateways that don’t use it. These steps do not address CVE-2026-88771, so installing a fixed build is still required.Citrix’s bulletins list fixes only for the 14.1 and 13.1 branches. NetScaler ADC and NetScaler Gateway versions 12.1 and 13.0 have reached end-of-life (EOL) and no longer receive security updates, and Citrix has not said whether they are affected by these vulnerabilities. Organizations still running these versions should move to a supported, fixed build.Are there any indicators of compromise for these vulnerabilities?Citrix has made generic indicators of compromise (IoCs) available through NetScaler Console, which requires product usage telemetry to be enabled. Customers who do not use NetScaler Console, or cannot access the feature, can contact Citrix Support to request the IoCs. Citrix notes that the IoC information may not cover all threat actor tactics, techniques and procedures (TTPs) and recommends engaging forensic investigators for a comprehensive assessment.Mandiant and GTIG also published hunting guidance, along with IoCs and YARA rules. Because patching does not remove an attacker who already has access, organizations should check their appliances for signs of compromise. Mandiant also recommends revoking active sessions and rotating credentials used by the appliance after patching.Has Tenable Research classified these vulnerabilities as part of Vulnerability Watch?Yes. CVE-2026-88771, CVE-2026-88772 and CVE-2026-88779 have been classified as “Vulnerability of Interest” as part of Vulnerability Watch.Has Tenable released any product coverage for these vulnerabilities?A list of Tenable plugins for these vulnerabilities can be found on the individual CVE pages for CVE-2026-88771, CVE-2026-88772 and CVE-2026-88779 as they’re released. These links display all available plugins for these vulnerabilities, including upcoming plugins in our Plugins Pipeline.Additionally, customers can utilize Tenable Attack Surface Management to identify public-facing NetScaler assets by using the following query: Server Contains Netscaler OR Document Title contains Citrix GatewayGet more informationCitrix Security Bulletin CTX697096: NetScaler ADC and NetScaler Gateway Security BulletinCitrix Community: NetScaler ADC and NetScaler Gateway Security Bulletin (CVE-2026-88771 through CVE-2026-88778)Reddit r/Citrix thread: “Netscaler leak?”watchTowr post on X: Citrix NetScaler RCE confirmationKevin Beaumont on Mastodon: Zero-day confirmationCitrix Security Bulletin CTX697174: NetScaler ADC and NetScaler Gateway Security Bulletin for CVE-2026-88779Citrix Community: Understanding and Addressing CVE-2026-88779 in Citrix NetScaler ADC and Citrix NetScaler GatewayMandiant and Google Threat Intelligence Group: Defending Against Active Exploitation of Citrix NetScaler ADC and Gateway AppliancesASD’s ACSC: Critical vulnerabilities in Citrix NetScaler ADC and Citrix NetScaler Gateway productswatchTowr Labs: CVE-2026-88771 analysiswatchTowr Labs: CVE-2026-88772 analysisKevin Beaumont on Mastodon: PitScalerPitScaler: Citrix NetScaler Zero-Day Crisis trackerJoin Tenable’s Research Special Operations (RSO) Team on Tenable Connect for further discussions on the latest cyber threats.Learn more about Tenable One, the Exposure Management Platform for the modern attack surface.
- Oracle September 2026 Critical Security Patch Update addresses 672 CVEs
 by Research Special Operations on September 15, 2026 at 5:00 pm
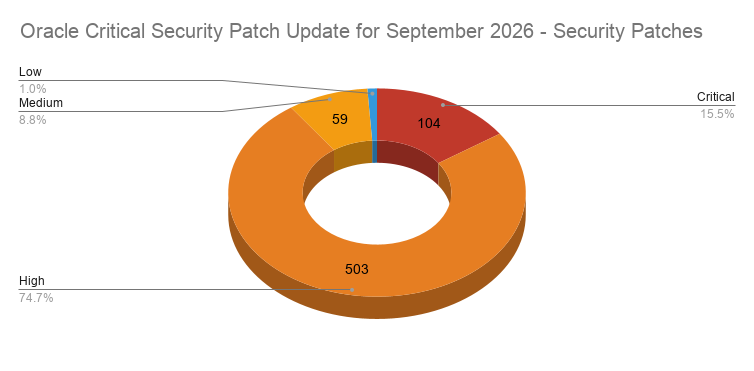
Oracle addresses 672 CVEs in its September 2026 Critical Security Patch Update with 673 patches, including 104 critical updates.Key TakeawaysThe September 2026 Critical Security Patch Update (CSPU) contains fixes for 672 unique CVEs in 673 security updates104 issues (15.5% of all patches) were assigned a critical severity ratingOracle E-Business Suite received the highest number of patches at 159, accounting for 23.6% of all patchesBackgroundOn September 15, Oracle released its Critical Security Patch Update (CSPU) for September 2026. Beginning in May 2026, Oracle introduced CSPUs as a monthly release cycle that sits between the larger quarterly Critical Patch Updates (CPUs), addressing a focused set of high-severity issues on a faster cadence. This CSPU contains fixes for 672 unique CVEs in 673 security updates across 17 Oracle product families. Out of the 673 security updates published, 15.5% of patches were assigned a critical severity. High severity patches accounted for the bulk of security patches at 74.7%, followed by critical severity patches at 15.5%.This month’s update includes 104 critical patches across 104 CVEs.SeverityIssues PatchedCVEsCritical104104High503503Medium5958Low77Total673672AnalysisThis month’s update saw the Oracle E-Business Suite product family contain the highest number of patches at 159, accounting for 23.6% of the total patches, followed by Oracle Fusion Middleware at 153 patches, which accounted for 22.7% of the total patches.A full breakdown of the patches for this CSPU can be seen in the following table, which also includes a count of vulnerabilities that can be exploited over a network without authentication.Oracle Product FamilyNumber of PatchesRemote Exploit without AuthOracle E-Business Suite15919Oracle Fusion Middleware15378Oracle Hyperion10250Oracle Siebel CRM6326Oracle Analytics508Oracle Communications3123Oracle Commerce2716Oracle Supply Chain195Oracle Virtualization191Oracle PeopleSoft164Oracle Database Server115Oracle Enterprise Manager75Oracle Financial Services Applications62Oracle Application Testing Suite30Oracle Java SE33Oracle Autonomous Health Framework21Oracle Utilities Applications21SolutionPatches are available in the September 2026 advisory for full details.Identifying affected systemsA list of Tenable plugins to identify these vulnerabilities will appear here as they’re released. This link uses a search filter to ensure that all matching plugin coverage will appear as it is released.Get more informationOracle Critical Security Patch Update Advisory – September 2026Oracle September 2026 Critical Security Patch Update Risk MatricesOracle Advisory to CVE MapJoin Tenable’s Research Special Operations (RSO) Team on Tenable Connect for further discussions on the latest cyber threats.Learn more about Tenable One, the Exposure Management Platform for the modern attack surface.
- Microsoft’s September 2026 Patch Tuesday addresses 964 CVEs (CVE-2026-81963, CVE-2026-85880)
 by Research Special Operations on September 8, 2026 at 2:07 pm
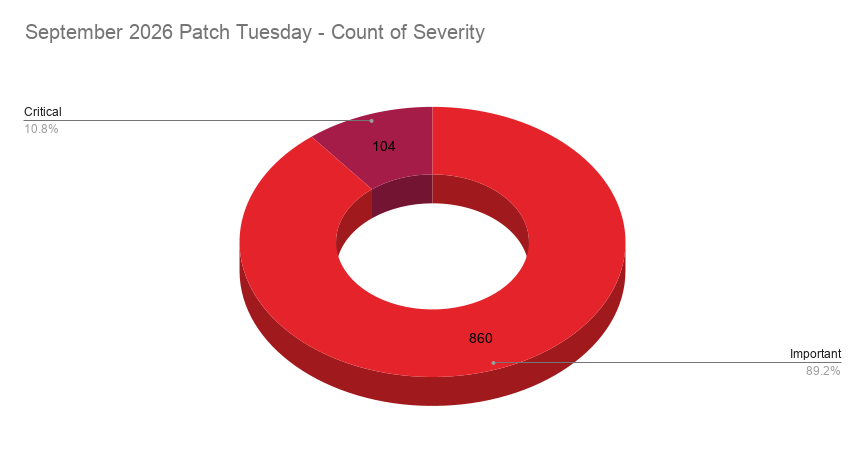
104Critical860Important0Moderate0LowMicrosoft addresses 964 CVEs, smashing July’s release as the largest Patch Tuesday release. This month’s updates include patches for two zero-days that were exploited in the wild.Microsoft patched a record 964 CVEs in its September 2026 Patch Tuesday release, with 104 rated critical and 860 rated as important.This month’s update includes patches for:.NET.NET and Visual StudioASP.NET CoreActive Directory Certificate Services (AD CS)Active Directory Domain ServicesActive Directory Federation Services (AD FS)Audio Video Control Transport ProtocolAzure ArcAzure CycleCloudAzure HDInsightsBranchCacheConnected Devices Platform Service (Cdpsvc)Data Sharing Service ClientGitHub Copilot and Visual Studio CodeGraphic FontsHID class driverIP HelperInternet Storage Name ServiceKernel Streaming WOW Thunk Service DriverMicrosoft AccountMicrosoft AuthenticatorMicrosoft Azure Attestation service and Device Health Attestation ServiceMicrosoft Azure CLIMicrosoft COM for WindowsMicrosoft Dynamics 365Microsoft Exchange ServerMicrosoft Graphics ComponentMicrosoft Install ServiceMicrosoft JScriptMicrosoft Local Security Authority Server (lsasrv)Microsoft OfficeMicrosoft Office AccessMicrosoft Office ExcelMicrosoft Office OutlookMicrosoft Office PowerPointMicrosoft Office PublisherMicrosoft Office SharePointMicrosoft Office WordMicrosoft Standard XPSMicrosoft Teams for AndroidMicrosoft Trace Data HelperMicrosoft UxTheme Library (uxtheme.dll)Microsoft WDAC OLE DB provider for SQLMicrosoft WebP Image ExtensionMicrosoft Windows Codecs LibraryMicrosoft Windows Media FoundationMicrosoft Windows PDFMicrosoft Windows SCSI Class System FileMicrosoft Windows Search ComponentMicrosoft Windows SpeechOpenSSH for WindowsPower AutomatePush Message Routing ServiceRPC RuntimeReliable Multicast Transport Driver (RMCAST)Remote Desktop ClientRemote Desktop Gateway ServiceRole: DNS ServerRole: Windows Fax ServiceSQL ServerSkype for BusinessSpring Cloud AzureStorage Port DriverTelnet ClientVirtual Hard Disk (VHD) Miniport DriverVisual StudioVisual Studio CodeVolume Manager DriverWindows AF_UNIX Socket ProviderWindows ALPCWindows Accounts ControlWindows Ancillary Function Driver for WinSockWindows Audio ServiceWindows Authentication MethodsWindows AutopilotWindows Bind Filter DriverWindows Biometric ServiceWindows BitLockerWindows Bluetooth Port DriverWindows Bluetooth ServiceWindows Boot ManagerWindows Broadcast DVR User ServiceWindows Broker Infrastructure ServiceWindows CD-ROM DriverWindows Camera Frame Server MonitorWindows Cloud Files Mini Filter DriverWindows Compressed FolderWindows Connected User Experiences and TelemetryWindows Container Manager ServiceWindows Core MessagingWindows Credential GuardWindows Credential ProvidersWindows DCOM ServerWindows DHCP ClientWindows DHCP ServerWindows DNSWindows DWM Core LibraryWindows Defender Firewall ServiceWindows Deployment ServicesWindows Device Association Broker serviceWindows Device Association ServiceWindows Devices Human InterfaceWindows Direct ShowWindows Display Enhancement ServiceWindows Distributed File System (DFS)Windows Embedded Mode ServiceWindows Encrypting File System (EFS)Windows Enterprise App ManagementWindows Error ReportingWindows Event Logging ServiceWindows Failover ClusterWindows Fast FAT DriverWindows File History ServiceWindows GDIWindows GDI+Windows Graphics KernelWindows Group PolicyWindows HTTP Print ProviderWindows HTTP.sysWindows HelloWindows Host Guardian ServiceWindows Hyper-VWindows IKE ExtensionWindows IP Address Management (IPAM) ServiceWindows Image AcquisitionWindows Imaging ComponentWindows InstallerWindows Internet Connection Sharing (ICS)Windows KerberosWindows KernelWindows Kernel Mode DriverWindows Key Distribution CenterWindows LDAP – Lightweight Directory Access ProtocolWindows License ManagerWindows Link Layer Topology Discovery ProtocolWindows MIDI Service ModuleWindows Management InstrumentationWindows Management ServicesWindows MediaWindows Media PlayerWindows Message QueuingWindows Message Queuing Queue ManagerWindows Microsoft DirectMusicWindows Mobile BroadbandWindows Modern Device Management (MDM)Windows Modern Execution ServerWindows NDISWindows NFS PortmapperWindows NTFSWindows NetlogonWindows Network Connection BrokerWindows Network File SystemWindows NotificationWindows OLE DBWindows Online Certificate Status Protocol (OCSP)Windows Overlay FilterWindows PaintWindows Partition Management DriverWindows Performance MonitorWindows Power Dependency CoordinatorWindows PowerShellWindows Print Spooler ComponentsWindows PrintWorkflowUserSvcWindows Program Compatibility Assistant ServiceWindows Push NotificationsWindows RDP ClientWindows RNDISWindows Raw Image ExtensionWindows RegistryWindows Remote Access Connection ManagerWindows Remote DesktopWindows Remote Desktop Licensing ServiceWindows Remote Desktop ProtocolWindows Remote Desktop ServicesWindows Resilient File System (ReFS)Windows Resilient File System (ReFS) Deduplication ServiceWindows Routing and Remote Access Service (RRAS)Windows SMB ClientWindows SMB ServerWindows SMB Server Network Transport Driver (srvnet.sys)Windows SchannelWindows Secure BootWindows Secure Kernel ModeWindows Secure Socket Tunneling Protocol (SSTP)Windows Security CenterWindows Security Health ServiceWindows ServerWindows Services for NFS ONCRPC XDR DriverWindows Setup Files CleanupWindows ShellWindows Smart CardWindows Spaceport.sysWindows StorageWindows Storage Management ProviderWindows Storage Port DriverWindows Storage Spaces ControllerWindows TCP/IPWindows Task SchedulerWindows Text ShapingWindows URL MonikerWindows USB Audio Class driver (usbaudio.sys)Windows USB DriverWindows USB Hub DriverWindows USB Mass Storage Class DriverWindows USB Video DriverWindows Universal Disk Format File System Driver (UDFS)Windows Universal Plug and Play (UPnP) Device HostWindows Update StackWindows VHD miniport driverWindows VOLSNAP.SYSWindows Virtual Trusted Platform ModuleWindows Volume Manager Extension DriverWindows Volume Shadow CopyWindows Web Platform StorageWindows WebClient ServiceWindows Win32 Kernel SubsystemWindows Win32KWindows Wireless NetworkingWindows Wireless Wide Area Network ServiceWindows Work Folder ServiceWindows Work FoldersWindows exFAT File SystemWindows iSCSIWindows iSCSI Target ServiceWinsockXBox Gaming ServicesXboxElevation of privilege (EoP) vulnerabilities accounted for 44.7% of the vulnerabilities patched this month, followed by remote code execution (RCE) vulnerabilities at 26.8%.ImportantCVE-2026-81963 | Windows Update Stack elevation of privilege vulnerabilityCVE-2026-81963 is an EoP vulnerability affecting Windows Update Stack elevation of privilege vulnerability. It received a CVSSv3 score of 7.8 and was rated as important. According to Microsoft, this vulnerability was exploited in the wild as a zero-day.Windows Update Stack contains a link following vulnerability. An attacker could exploit this vulnerability to elevate to SYSTEM privileges.Since 2022, seven Windows Update Stack EoP vulnerabilities have been patched across Patch Tuesday releases, but CVE-2026-81963 is the first to have been exploited in the wild as a zero-day.ImportantCVE-2026-85880 | Windows Advanced Local Procedure Call (ALPC) elevation of privilege vulnerabilityCVE-2026-85880 is a EoP vulnerability affecting Windows Advanced Local Procedure Call (ALPC). It received a CVSSv3 score of 7.8 and is rated as important. According to Microsoft, this vulnerability was exploited in the wild, making it one of two zero-days addressed in the September Patch Tuesday release. Successful exploitation would allow an attacker to gain SYSTEM level privileges.There have been 16 vulnerabilities patched in ALPC since 2022, but this is the first to be included in Patch Tuesday in more than three years (April 2023) and the second to be exploited as a zero-day since CVE-2023-21674 as part of the January 2023 Patch Tuesday.ImportantCVE-2026-69380 | Microsoft Exchange Server elevation of privilege vulnerabilityCVE-2026-69380 is an EoP in Microsoft Exchange Server. It received a CVSSv3 score of 8.1 and is rated as important. This is a missing authorization vulnerability. An authenticated attacker with access to a mailbox through a low-user privilege user account could exploit this vulnerability to gain access to other mailboxes. Successful exploitation would allow the attacker to send and receive emails as other Exchange users as well as access attachments. Despite the high CVSS score, this vulnerability is rated as “Exploitation Less Likely” according to the Microsoft Exploitability Index.ImportantCVE-2026-69525 | Remote Desktop Services remote code execution vulnerabilityCVE-2026-69525 is an RCE vulnerability affecting Remote Desktop Services. It received a CVSSv3 score of 9.8 and is rated as important. Successful exploitation of this flaw would allow an attacker to execute arbitrary code by exploiting a use-after-free flaw. Microsoft assesses this vulnerability as “Exploitation More Likely.”In addition to CVE-2026-69525, three RCEs in Remote Desktop Services were also patched this month. While each were rated as important, they differed in their CVSS scoring and exploitability rating as noted in the table below:CVECVSSv3Exploitability AssessmentCVE-2026-695147.5Exploitation UnlikelyCVE-2026-695397.5Exploitation UnlikelyCVE-2026-695997.5Exploitation Less LikelyCVE-2026-695367.1Exploitation Less LikelyCriticalCVE-2026-69730 | Windows DNS Server remote code execution vulnerabilityCVE-2026-69730 is an RCE vulnerability affecting Windows DNS Server. It received a CVSSv3 score of 9.8 and is rated Critical. According to the advisory, an unauthenticated, remote attacker could send a crafted packet to exploit a use-after-free flaw in Windows DNS in order to achieve remote code execution. Microsoft assesses this flaw as “Exploitation More Likely.”Eight additional RCEs in Windows DNS Server were patched this month, however they did not achieve the same exploitability assessment as CVE-2026-69730. These eight are outlined in the table below:CVECVSSv3SeverityExploitability AssessmentCVE-2026-695518.8ImportantExploitation Less LikelyCVE-2026-698138.1CriticalExploitation Less LikelyCVE-2026-698588.1CriticalExploitation UnlikelyCVE-2026-775058.1CriticalExploitation Less LikelyCVE-2026-697828.1ImportantExploitation UnlikelyCVE-2026-698278.1CriticalExploitation UnlikelyCVE-2026-699898.1ImportantExploitation UnlikelyCVE-2026-729287.5ImportantExploitation Less LikelyCriticalCVE-2026-69676 | Windows Kerberos remote code execution vulnerabilityCVE-2026-69676 is an RCE vulnerability affecting Windows Kerberos. It received a CVSSv3 score of 8.8 and is rated critical. An attacker with low-level access could exploit this authentication bypass flaw using capture-replay against Windows Kerberos in order to execute arbitrary code. Microsoft assesses this flaw as “Exploitation More Likely.”Tenable SolutionsA list of all the plugins released for Microsoft’s September 2026 Patch Tuesday update can be found here. As always, we recommend patching systems as soon as possible and regularly scanning your environment to identify those systems yet to be patched.For more specific guidance on best practices for vulnerability assessments, please refer to our blog post on How to Perform Efficient Vulnerability Assessments with Tenable.Get more informationMicrosoft’s September 2026 Security UpdatesTenable plugins for Microsoft September 2026 Patch Tuesday Security UpdatesJoin Tenable’s Research Special Operations (RSO) Team on Tenable Connect for further discussions on the latest cyber threats.Learn more about Tenable One, the Exposure Management Platform for the modern attack surface.
- StyleSmuggler (CVE-2026-75650): Frequently asked questions about Adobe Commerce and Magento zero-day
 by Satnam Narang on September 8, 2026 at 10:00 am
A critical unauthenticated remote code execution (RCE) zero-day in Adobe Commerce and Magento Open Source, dubbed StyleSmuggler, has been actively exploited since September 4 with attacks observed three days before a vendor patch became available.Key takeawaysCVE-2026-75650 is a critical remote code execution vulnerability in Adobe Commerce, Adobe Commerce B2B and Magento Open Source that can be triggered without authentication.Active exploitation of CVE-2026-75650 began on September 4, 2026, three days before Adobe released a hotfix, with multiple victim stores confirmed across different attack campaigns.Adobe released Hotfix VULN-39341 on September 7, 2026, and Tenable detection plugins will be published as they become available.BackgroundTenable’s Research Special Operations Team (RSO) has compiled this blog to answer Frequently Asked Questions (FAQ) regarding CVE-2026-75650, a zero-day remote code execution vulnerability in Adobe Commerce, Adobe Commerce B2B and Magento Open Source that has been actively exploited in the wild.FAQWhen was CVE-2026-75650 first disclosed?On September 5, 2026, the Sansec Forensics Team published research detailing an actively exploited zero-day vulnerability in Magento and Adobe Commerce that it named StyleSmuggler.What is CVE-2026-75650?CVE-2026-75650 is a remote code execution vulnerability in Adobe Commerce, Adobe Commerce B2B and Magento Open Source. Successful exploitation grants an unauthenticated attacker the ability to execute arbitrary code on a vulnerable server. CVE-2026-75650 carries a CVSSv3 score of 10.0, the highest possible rating. Additionally, its scope is changed, meaning exploitation can impact resources beyond the vulnerable component itself.CVEDescriptionCVSSv3CVE-2026-75650Adobe Commerce and Magento Open Source Remote Code Execution10.0 The following products and versions are affected:ProductAffected versionsAdobe Commerce2.4.4 through 2.4.9Adobe Commerce B2B1.3.3 through 1.5.3Magento Open Source2.4.6 through 2.4.9 How does StyleSmuggler work?StyleSmuggler exploits a flaw in how Magento’s template engine processes style-related properties. An attacker crafts a malicious payload containing PHP code and injects it through the styles properties within the template system. Magento writes this attacker-controlled content to disk as part of its normal operations. The injected code is then executed when the platform renders a transactional email template, specifically the “Payment Transaction Failed Reminder” notification. Because this injection path does not sit behind any authentication gate, a remote attacker can trigger it without credentials, and the technique works regardless of which session storage backend is configured.Once a server is compromised, the attacker deploys a persistent implant. The malware binary is installed at ~/.local/share/.gvfsd/gvfsd-user and masquerades as a Linux kernel thread using the process name [kworker/u:8:0]. It also disguises itself using the process names fc-cache and chronyd, both legitimate system utilities. A cron job restarts the implant every five minutes. Later variants updated the cron interval to twice an hour, and the malware supports both x86-64 and arm64 architectures.Is CVE-2026-75650 being exploited in the wild?Yes. Active exploitation of CVE-2026-75650 began on September 4, 2026 according to Sansec. Multiple victim stores have been confirmed across different attack campaigns. Disrex, an incident response firm, had first-hand experience with at least two compromised stores.Historical exploitation of Adobe Commerce and MagentoAdobe Commerce and its open-source counterpart, Magento, have been recurring targets for attackers. Three prior Adobe Commerce and Magento vulnerabilities have been added to the Cybersecurity and Infrastructure Security Agency’s (CISA) Known Exploited Vulnerabilities (KEV) catalog.CVEDescriptionKEV date addedCVE-2025-54236Improper input validation, account takeover via REST API (“SessionReaper”)2025-10-24CVE-2024-34102XXE restriction bypass leading to remote code execution (“CosmicSting”)2024-07-17CVE-2022-24086Improper input validation leading to arbitrary code execution2022-02-15 CVE-2026-75650 has not yet been added to CISA KEV as of September 8, 2026. There is no CISA Emergency Directive or Alert associated with this vulnerability at this time.Which threat actors are exploiting CVE-2026-75650?As of September 8, 2026, there is no public attribution linking the exploitation of CVE-2026-75650 to a specific threat actor or group. Sansec documented activity from at least two distinct operators on the same victim stores: the original group deploying the persistent implant, and a second unrelated attacker dropping a PHP web shell into the product image cache. The techniques and tooling differ significantly between the two, and Sansec treats them as separate campaigns.Is there a proof-of-concept (PoC) available for CVE-2026-75650?At the time this blog post was published on September 8, there is no standalone public proof-of-concept for CVE-2026-75650.Are there indicators of compromise (IoCs) for CVE-2026-75650?Yes. Sansec published indicators of compromise alongside its StyleSmuggler research. The full IoC list can be found in Sansec’s blog.Has Tenable Research classified CVE-2026-75650 as part of Vulnerability Watch?Yes. Tenable Research has classified CVE-2026-75650 as a Vulnerability of Interest (VOI) as part of Vulnerability Watch.Are patches available for CVE-2026-75650?On September 7, 2026, Adobe released Hotfix VULN-39341 to address CVE-2026-75650. Additional details can be found in Adobe’s security bulletin APSB26-146.Adobe also recommends rotating the encryption key and all credentials it protects following a compromise, including admin passwords, REST, SOAP, and GraphQL integration tokens, OAuth client secrets, payment gateway API credentials, database credentials, SSH and deploy keys, and extension API keys.At the time exploitation was first observed on September 4, no vendor patch existed. Patching alone does not remediate an existing compromise. Stores that were active during the three-day window before the hotfix require incident response in addition to applying the fix.Has Tenable released detection coverage for CVE-2026-75650?A list of Tenable detection plugins for CVE-2026-75650 will be available on the CVE page as they are released. This link will display all available plugins for this vulnerability, including upcoming plugins in our Plugins Pipeline.Get more informationSansec: StyleSmuggler 0day ResearchAdobe Security Bulletin APSB26-146Disrex: StyleSmuggler incident response and mitigationsJoin Tenable’s Research Special Operations (RSO) Team on the Tenable Community.Learn more about Tenable One, the Exposure Management Platform for the modern attack surface.
- Edge infrastructure under siege: what two independent datasets reveal about who’s exploiting your perimeter
 by Research Special Operations on August 26, 2026 at 9:00 am
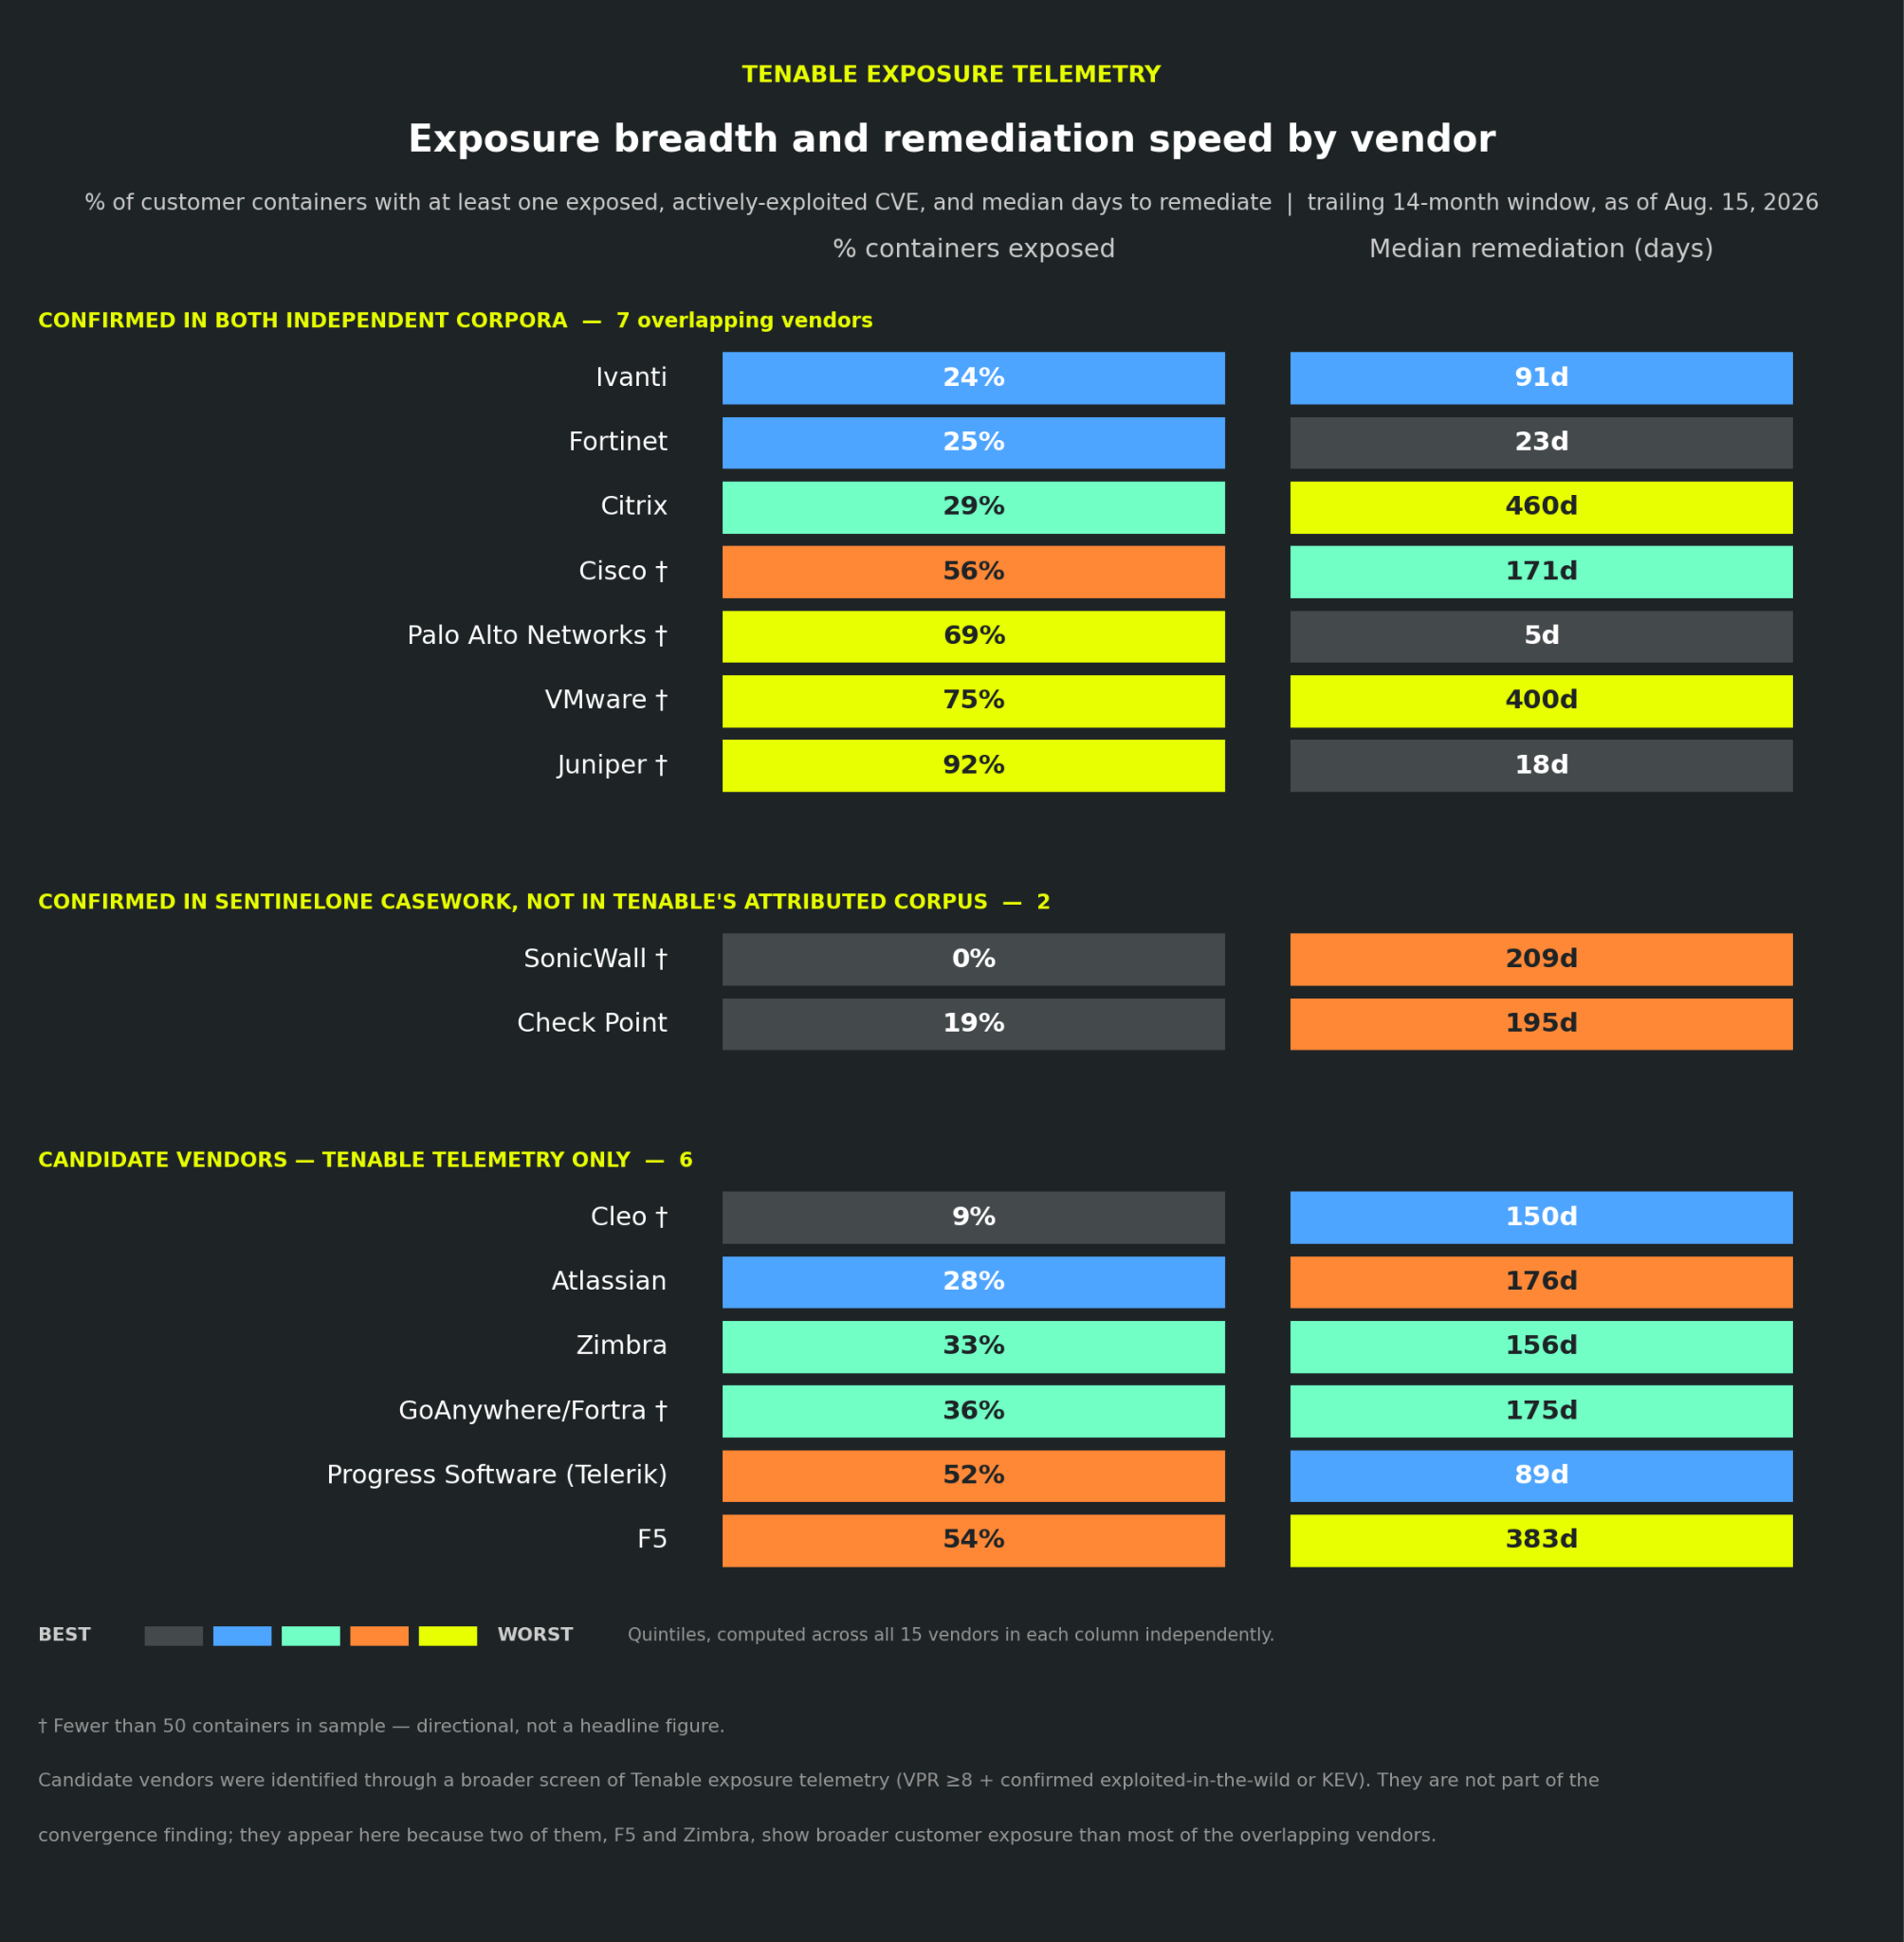
A joint Tenable-SentinelOne analysis of 93 CVE-actor attribution pairs reveals that both state-sponsored actors and cybercriminals independently converge on the same edge infrastructure. Special thanks to SentinelOne® Incident Readiness & Response for their contributions to this publication.It is the shared attack surface where state-sponsored threat actors and financially motivated criminal groups independently converge — not the province of a single adversary category, and not exclusively a nation-state problem, despite two years of headlines about China-nexus actors targeting Ivanti, Fortinet, and Palo Alto Networks. The data here tells a different and much broader story. One focused on vendors vs CVEs.Key TakeawaysTwo independent observation systems, Tenable exposure telemetry across thousands of customer containers and SentinelOne DFIR casework across 66 CVEs, converge 79% on the same vendor attack surfaces despite minimal CVE-level overlap.Twelve CVEs in the combined dataset have confirmed multi-nexus attribution: state-sponsored and criminal actors independently exploiting the same vulnerability, across five nexus categories (China, Russia, DPRK, Iran, ransomware).The exposure picture is flatter than the headlines suggest: Fortinet, the vendor most associated with edge-device attacks in the press, sits mid-pack on container-grain exposure (25%) — well behind F5 (54%) and in a tight 10-point band with Check Point, Ivanti, and Citrix.54% of customer environments running F5 products have at least one exposed, actively-exploited CVE; Citrix customers show the slowest remediation patterns at 461 days median time to patch.Remediation complexity, particularly of high priority CVEs, leads to a statistically significant 24-day remediation gap, leaving large windows of opportunity for attackers.The same product lines get hit again and again: Ivanti EPMM and Ivanti Connect Secure each show a newly exploited CVE roughly every 8.5 to 13 months.Leverage multiple defense-in-depth strategies: patch as quickly as possible, but also minimize the attack surface (feature-set minimization) and run endpoints in protect mode to better stop lateral movement from attacks that gain initial access.The convergence is the storyTwelve CVEs in the combined dataset have confirmed multi-nexus attribution: state-sponsored and criminal actors independently exploiting the same vulnerability, across five nexus categories. Four examples illustrate the pattern:CVEProductActors (Nexus)SignificanceCVE-2026-15409SonicWall SMA1000UTA0533 (unattributed) + INC RansomwareEspionage-to-ransomware succession on an active zero-dayCVE-2023-42793JetBrains TeamCityAPT29 (Russia) + Lazarus (DPRK)Two state-sponsored actors from different nations on the same CVECVE-2024-3400PAN-OS GlobalProtectUTA0218 (China) + INC RansomwareChina-nexus zero-day reused by ransomware operatorsCVE-2024-24919Check Point QuantumPurpleHaze (China) + Fox Kitten (Iran)China and Iran independently exploiting the same gateway vulnerability The remaining eight confirmed multi-nexus CVEs span Fortinet, Citrix, Cisco, and Ivanti product lines. State-sponsored actors and ransomware operators are not operating in separate vulnerability ecosystems. They share the same entry points into the same products. The breadth of the convergence, not any single actor’s activity, is the finding.That pattern holds across the full combined analysis. Three conclusions emerge:Vendor attack surfaces are the persistent exploitation target. The same eleven vendors (i.e., Fortinet, Citrix, Ivanti, Palo Alto Networks, Cisco, Juniper, VMware, Microsoft, Oracle, CrushFTP, and Meta’s React framework) appear in both observation systems at 79% convergence, and all seven edge-product vendors converge. Serial exploitation timing on Ivanti products shows the vulnerability-to-exploitation pipeline refreshing at 8.5 to 13-month intervals on the same product lines. This is structural, not episodic. Patching the current CVE does not remove the vendor attack surface from the threat landscape.State-sponsored and ransomware actors converge structurally. Twelve CVEs with confirmed multi-nexus attribution span all five nexus categories and cross the state-criminal divide. Defending against one actor category on edge devices necessarily requires defending against all of them, because the attack surface is shared. An organization that patches only for nation-state TTPs leaves itself exposed to ransomware operators exploiting the same vulnerability, and vice versa.High-priority CVEs take more time to remediate, not less. Across Tenable’s 238-CVE high-priority list, high-priority CVEs carry a median remediation time of 146 days, compared to 122 days for all other CVEs — a 24-day gap that is statistically significant. The edge-appliance-specific subset (52 CVEs) shows a consistent 8-day gap in the same direction, which was not statistically significant, but suggests the direction may hold for edge appliances too. External data corroborates the pattern: the 2026 Verizon Data Breach Investigations Report (DBIR) found that median patch time increased from 32 to 43 days year over year, even as exploitation overtook credential theft as the number one initial access vector, and the 2025 DBIR, which incorporated Tenable RSO’s remediation trend analysis across 17 edge-related CVEs, found that only 54% of edge device KEVs were fully remediated. The explanation is structural: edge devices are the network boundary, so patching a VPN gateway or firewall means downtime for every user behind it, and change management gates multiply. These devices also resist standard patching workflows because they do not run endpoint agents, often require firmware-level updates with manual validation, and frequently lack active support contracts. The result is that the devices most worth patching are operationally the hardest to patch — and as the high-priority queue grows (the 2026 DBIR reports 50% more critical vulnerabilities to patch than the prior year), everything on it waits longer.BackgroundEdge and perimeter devices occupy a uniquely consequential position in enterprise architecture. VPN gateways, firewalls, remote access appliances, and application delivery controllers sit at the boundary between trusted and untrusted networks. They are very often the first component an attacker touches and, for many organizations, the last component that gets patched. When one of these devices is compromised, the attacker inherits its network position: inside the perimeter, with access to internal resources, often without triggering endpoint detection.This analysis combines two independent datasets to demonstrate that convergence. Tenable contributes exposure telemetry from the Tenable One Exposure Management Platform, covering thousands of customer containers and measuring what edge infrastructure is deployed, what is vulnerable, and how long it remains unpatched. This dataset extends Tenable Research’s ongoing analysis of edge device exposure trends, including the remediation telemetry Tenable contributed to the 2025 and 2026 Verizon DBIR reports. SentinelOne contributes findings from its digital forensics and incident response (DFIR) practice, documenting which threat actors actually exploit which vulnerabilities, observed firsthand inside compromised environments. Neither dataset was built for this analysis; each was constructed independently for different operational purposes.The finding that makes this analysis compelling is not about any single CVE or any single actor. It is the structural convergence: two independent observation systems, looking at the problem from opposite sides, arrive at the same conclusion about which vendor surfaces are under persistent, broad exploitation, and by whom. (For how each dataset was built and scored, see the Methodology appendix below.)What’s exposed: the vulnerability surfaceTenable’s exposure telemetry provides the vulnerability-side view. All exposure metrics reported here use container-grain measurement: the percentage of customer environments (organizational containers) with at least one asset vulnerable to a given CVE as of Aug. 15, 2026, relative to total exposed containers over the preceding 14-month period. This measures breadth of organizational exposure to edge-product vendor vulnerabilities, not raw asset counts, across the sampling window.This section covers 15 vendors in three groups: seven confirmed in both independently compiled corpora, two confirmed in SentinelOne’s casework but absent from Tenable’s attributed corpus, and six “candidate” vendors surfaced by a broader screen of Tenable telemetry. The candidates are not part of the convergence finding, but two, F5 and Zimbra, show broader customer exposure than most of the confirmed seven, so omitting them would understate the breadth of at-risk edge infrastructure.[FIGURE: Current vendor-level exposure heat map (container-grain, 15 vendors). Proportion of historically-exposed containers with at least one asset actively exposed to one or more relevant CVEs. Source: Tenable exposure telemetry.]F5 and Citrix lead for different reasons. Among vendors with statistically robust sample sizes, F5 customers are the most broadly exposed: 53.8% of 2,784 monitored customer environments running F5 products have at least one actively exploited CVE present. Citrix customers show the slowest remediation patterns: a median of 461 days to patch, with 71% of affected environments still carrying unpatched Citrix CVEs after a full year. F5 leads on scale of exposure; Citrix leads on persistent exposure.The mid-pack is flatter than expected. Check Point (18.6%), Ivanti (24.1%), Fortinet (24.9%), and Citrix (28.8%) cluster within a 10-point band at container-grain. Fortinet, which dominates headlines, is mid-pack by this measure.Thin-sample vendors show extreme rates but require caution. Juniper (91.7%), VMware (75.0%), Palo Alto Networks (69.2%), and Cisco (56.2%) all show container-exposure proportions above 50%, but each has fewer than 50 in-sample containers. These statistics are real directional signals, but should be considered within the context of the relatively low sample size.Serial exploitation is structural. Two clean serial-exploitation sequences appear in the dataset: Ivanti EPMM (approximately 8.5 months between successive exploited CVEs) and Ivanti Connect Secure (approximately 13 months). Same product line, new vulnerability, repeat exploitation. Tenable Research has published advisories on both Ivanti exploitation sequences, tracking each CVE from initial disclosure through active exploitation, and the exposure data here extends that analysis with organizational remediation timelines not available at the time of the original advisories. The next one is coming.Who exploits what: the threat actor landscapeThis is not a targeted effort by a specific group. Edge infrastructure is a core focal point of attack across a broad range of threat actors and nexus categories. The combined Tenable-SentinelOne corpus documents exploitation by actors spanning five nexus categories: China, Russia, DPRK, Iran, and criminal (financially motivated). All five categories independently target the same vendor surfaces. Every attribution in the corpus is bucketed into one of three confidence tiers derived from a five-dimensional rubric evaluating attribution directness, evidence provenance, recency, exploitation role, and source corroboration. Confidence tiers, from high to low, are: DIRECT, TECHNIQUE-ALIGNED, or INFERRED.Actor density scales with vendor exposure. Fortinet products face the broadest actor surface: 29 distinct threat actors across five nexus categories. Citrix follows with 22 actors across five categories, Ivanti with 19 across four, Palo Alto Networks with nine across three, and Check Point with six across two. Every focal vendor has confirmed exploitation from multiple nexus categories. No single vendor’s exposure is attributable to a single adversary group.China-nexus actors are the highest-confidence case study, appearing across nine vendors in the corpus, with four DIRECT-tier attributions from the scored dataset alone. But the analytical value here is not that China targets edge devices. That is well established. The value is that China, Russia, DPRK, Iran, and ransomware operators all target the same edge devices, as the examples above illustrate. The governed attribution methodology is what allows this claim to be made with precision: we can distinguish confirmed multi-nexus convergence (DIRECT-tier evidence on both sides) from assessed convergence (INFERRED, requiring corroboration).What incident response sees that telemetry can’tExposure data shows which appliances are reachable, vulnerable, and unpatched. Incident response looks at what happened when attackers got in: what they accessed, what they took, and where they went next. In SentinelOne DFIR cases involving edge infrastructure, attackers used credentials stored on the appliances and the access those appliances already had to reach internal systems.Credential theft from edge appliancesAcross three engagements, threat actors reached the management plane of FortiGate appliances and created rogue administrative accounts. In two, they also exported device configurations and extracted credentials that could be used to move further into the network. Two of these three are documented in detail in FortiGate Edge Intrusions.In one of those two, the exported configuration contained LDAP bind credentials for a directory service account. The account was later used in the environment. A few hours later, the threat actor added two computers to the domain. Neither had a Service Principal Name, which is unusual for a legitimate domain join. The mS-DS-CreatorSID attribute on both accounts pointed back to the stolen service account.We saw similar activity on an Ivanti Cloud Services Appliance in late 2024. A China-nexus actor chained CVE-2024-8963 with CVE-2024-8190 before the first public disclosure in the chain. After gaining access, the actor collected SSH keys and other stored credentials. That engagement is documented as Activity F in Follow the Smoke.These appliances did not provide conventional endpoint telemetry. We had to follow the activity into authentication records, newly created Active Directory objects, and the later use of credentials taken from the appliances.When the initial access vector cannot be confirmedIn December 2025, Fortinet disclosed CVE-2025-59718, an authentication bypass in its FortiCloud SSO integration affecting FortiOS and other products. Several weeks later, Fortinet disclosed CVE-2026-24858. This second flaw allowed an attacker with a FortiCloud account and a registered device to log into devices belonging to other customers when FortiCloud SSO was enabled.That overlap mattered in one of the three engagements above. The appliance was running a version affected by both CVEs, but the available logs did not show when or how the attacker first gained access. The earliest retained malicious activity showed a rogue local administrator account. A few minutes later, a domain administrator authenticated from the appliance’s VPN address pool. Exposure data showed that the appliance had been vulnerable to both CVEs, but that alone did not establish how it was compromised. We treated both as possible, not confirmed, initial-access vectors.Abuse of trusted management accessIn one SentinelOne DFIR engagement involving a FortiManager appliance, CVE-2024-47575 allowed an unauthorized device to register with the appliance through the management protocol. Two log entries, seconds apart, recorded the rogue registration and the settings change that followed. The threat actor then staged an archive of managed-device configurations that could expose credentials, addresses, and details about the network. The actor had been present for about a month before the customer detected the activity.In a separate engagement, a threat actor chained SQL injection, pass-the-hash authentication, and authentication bypass against an internet-facing SonicWall GMS console (CVE-2023-34133, CVE-2023-34132, and CVE-2023-34124). The actor created administrative accounts on a platform operated by a managed service provider, then used existing shared access to enter multiple customer environments. Most of the resulting traffic was advertising-related, leading us to assess that the infrastructure was being used for click fraud.The actors were after different things. One collected configuration data and information about the network. The other used the access to turn systems across several environments into proxies. In both cases, the actor inherited the access that the organization had already granted to the management platform. These cases show the difference between the two views: exposure telemetry finds the vulnerable device, while incident response shows what was taken from it and where the attacker went next.What to do about itPatch F5 and Citrix edge devices immediately. These two vendors combine the highest exposure rates with the slowest remediation timelines across statistically robust samples. Look for strategies to reduce the remediation time, particularly for weaponized CVEs. Additionally, reduce the attack surface by minimizing the enabled feature set on these devices and aim for defense in depth by running endpoints in protect mode to limit lateral movement opportunities.Audit Ivanti Connect Secure and EPMM deployments. Serial exploitation on observed 8.5 to 13-month cycles means the next exploitable CVE in these product lines is a question of timing, not probability. Organizations running Ivanti edge products should assume they will face a new actively exploited vulnerability within the next year and plan patching capacity accordingly.Implement edge-device-specific patch SLAs. The delayed remediation paradox demonstrates that general priority frameworks do not translate into faster patching on the devices that sit at the network boundary. Edge devices and network infrastructure warrant dedicated remediation timelines that are shorter than the organizational default and commensurate with the elevated risk.Treat edge device exposure as a cross-signal priority. Attribution, severity, and exposure volume identify different CVEs as “top priority.” Organizations need all three signals for complete coverage. A vulnerability management program that prioritizes exclusively by CVSS will systematically underweight CVEs with strong exploitation evidence but modest severity scores, and vice versa. The Tenable One Exposure Management Platform enables this cross-signal approach by combining vulnerability severity, exposure intelligence, asset context, and exposure data into a unified prioritization view.Identifying affected systemsTenable customers can use the Tenable Vulnerability Watch dashboard to monitor classifications for all CVEs discussed in this analysis. A list of Tenable plugins for the vulnerabilities discussed in this analysis can be found on the individual CVE pages at tenable.com/cve as they are released. This link displays all available plugins for each vulnerability, including upcoming plugins in our Plugins Pipeline.Get more informationTenable Vulnerability WatchSentinelOne – What two independent datasets reveal about who’s exploiting your perimeterSentinelOne Threat Research (PurpleHaze, SonicWall SMA1000)FortiGate Edge Intrusions – SentinelOneFollow the Smoke – SentinelOneCISA Known Exploited Vulnerabilities CatalogJoin Tenable’s Research Special Operations (RSO) Team on Tenable Connect for further discussions on the latest cyber threats.Learn more about Tenable One, the Exposure Management Platform for the modern attack surface.Appendix: Methodology and corpus constructionHow the corpus was built. Tenable’s 33-CVE corpus was derived by combining and deduplicating vulnerabilities with the highest exploitation volume and broadest actor adoption; SentinelOne validated CVEs across 14 vendors, and their 66-CVE landscape view reflects 12 months of DFIR casework with false positives removed. Combined, the two datasets identify 82 distinct CVEs, 17 of which appear in both. Layered on top of these sources is a governed attribution corpus of 93 CVE-actor pairs spanning approximately 39 named threat actors and five nexus categories.Why Tenable tracks these CVEs. Tenable’s set comes out of exposure management. A CVE enters it through the Vulnerability Watch program, which classifies vulnerabilities under active or likely to be exploited, and is additionally scored with a Vulnerability Priority Rating (VPR). The question being answered is prescriptive: of everything actually deployed across customer environments, what should be prioritized and patched first? Threat-actor attribution is layered on afterward from definitive and confidence-scored sources (e.g., Federal cybersecurity advisories).Why SentinelOne tracks these CVEs. SentinelOne’s set comes from the opposite direction: incident response. A CVE earns its place in their 12-month DFIR landscape because responders found it used in a real intrusion — the initial access vector in a case someone called them about. The question being answered is forensic: what happened here, and who did it? Coverage is shaped by who engaged them, not by install base.What “overlap” means here. Overlap was measured at two levels, and the answer changes sharply depending on which level you use.At the level of the individual vulnerability, the two sets barely intersect. Only 17 of 82, or 21%, of CVEs are common to both. Tenable and SentinelOne are, for the most part, not looking at the same vulnerabilities. However, the datasets converge at the product level. Eleven of the 14 vendors in Tenable’s focal CVE set appear in SentinelOne’s 12-month DFIR landscape – a 79% convergence: Fortinet, Citrix, Ivanti, Palo Alto Networks, Cisco, Juniper, VMware, Microsoft, Oracle, CrushFTP, and Meta’s React framework. That’s 79% convergence at the vendor level against 21% at the CVE level. Three vendors did not conform: Apache and SAP were absent from SentinelOne’s casework, and the one Progress case they worked on was closed as a false positive. Narrow the comparison to edge and remote-access infrastructure specifically, and the convergence is a perfect 100%. Tenable’s corpus independently identified seven edge vendors (i.e., Fortinet, Citrix, Ivanti, Palo Alto Networks, Cisco, Juniper, and VMware). All seven appear in SentinelOne’s casework. Two teams, working from unrelated evidence for unrelated purposes, arrived at the same seven vendors while sharing roughly one CVE in five.Why the distinction matters. “Different vulnerabilities, same vendors” is not a weaker version of “same vulnerabilities.” It is a different and more actionable claim. Had both datasets converged on the same individual CVEs, the story would be that a specific handful of vulnerabilities is being widely exploited: patch those and the problem shrinks. What the data actually shows is that state-sponsored and criminal operators are independently arriving at the same small set of edge and remote-access product vendors, then finding their own separate ways in. The durable target is the vendor attack surface. Patching this quarter’s Ivanti CVE does not remove Ivanti from anyone’s target list.All third-party product names, logos, and brands mentioned in this publication are the property of their respective owners and are for identification purposes only. Use of these names, logos, and brands does not imply affiliation, endorsement, sponsorship, or association with the third party.
- Frequently asked questions about the active threat to Siemens S7 Series PLCsby Research Special Operations on August 20, 2026 at 10:01 am
A joint cybersecurity advisory released by multiple U.S. government agencies warns that threat actors are using AI-generated exploitation scripts to target exposed Siemens S7 Series PLCs across critical infrastructure sectors.Key TakeawaysUnattributed threat actors are exploiting known weaknesses and unnecessary internet exposure to conduct reconnaissance and possible pre-positioning for future disruptive attacks against Siemens S7 Series PLCs.The attackers are leveraging AI to build and refine exploit scripts faster than manual development would allow. AI use lowers the technical bar for ICS attacks in a way defenders haven’t had to plan for before.There is no single patch, because there is no single flaw. Mitigation depends on removing Siemens S7 Series PLCs from direct internet exposure, segmenting OT from IT networks and hardening access controls.BackgroundOn August 19, 2026, the National Security Agency (NSA), the Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau of Investigation (FBI), the Department of Energy (DOE) and the Environmental Protection Agency (EPA) released a joint Cybersecurity Advisory (AA26-231A) warning that threat actors are actively targeting Siemens S7 Series programmable logic controllers (PLCs) that are exposed to the internet or insufficiently segmented from it. The activity spans the S7-200, S7-300, S7-400, S7-1200 and S7-1500 series and most heavily affects the Critical Manufacturing, Energy, Water and Wastewater, Chemical, Food and Agriculture and Commercial Facilities sectors, with potential exposure in the Defense Industrial Base as well.According to the authoring agencies, threat actors are using AI-generated exploitation scripts, disguised as legitimate operational technology (OT) monitoring tools, to conduct reconnaissance and build capability against exposed PLCs. The Tenable Research Special Operations Team (RSO) has put together this frequently asked questions (FAQ) blog to help security and OT teams understand the threats, the techniques involved and the mitigations offered by the authoring agencies. The advisory itself notes that ongoing PLC targeting is broader than Siemens alone and that all PLC owners and operators, regardless of vendor, should apply all relevant mitigations.FAQWhat is the active threat to Siemens S7 Series PLCs?The advisory describes coordinated reconnaissance and capability-development activity against Siemens S7 Series PLCs that are internet-exposed or poorly segmented. According to the authoring agencies, the threat actors combine internet scanning services with AI-assisted scripting to build custom tools that can read and write PLC memory, configuration data, and ladder logic programs over the S7comm protocol, while masquerading as legitimate monitoring software.The agencies assess the activity as persistent reconnaissance intended to develop capabilities and pre-position for future disruptive attacks against critical infrastructureWhich Siemens PLC models are being targeted?The advisory identifies five Siemens S7 Series product lines as targets:SeriesVariants targetedS7-200All CPU variantsS7-300All CPU variants, including the 314, 315 and 317 modelsS7-400All CPU variantsS7-1200CPU 1211C, 1212C, 1214C, 1215C and 1217C variantsS7-1500All CPU variants including F-series safety controllers How is this different from the Iranian-linked PLC campaign covered in AA26-097A?In April 2026, CISA and its partners, including NSA, the FBI, EPA, DOE, U.S. Cyber Command, and the Treasury Department, issued and later expanded cybersecurity advisory AA26-097A, which detailed a campaign publicly linked to Iran-affiliated actors tracked as CyberAv3ngers. That campaign exploited internet-exposed PLCs from Rockwell Automation, Schneider Electric and Siemens using the vendors’ own engineering software to manipulate readings and exfiltrate project files. The updates to that advisory were made just days before the news of attacks involving several water districts, including those in Minnesota. For more information on these attacks, please refer to the RSO blog; Coordinated “cyberattack” on U.S. water utilities: What you need to know.This new advisory covers a distinct activity pattern specifically centered on the Siemens S7 Series devices. The authoring agencies do not attribute these attacks to any named threat actor or group. The techniques described in this advisory describe threat actors leveraging AI to design scripts built on open-source industrial automation libraries, including snap7.dll, disguising these scripts as monitoring tools. Organizations should treat the two advisories as related but separate threats to the same class of equipment, and should apply the mitigations in both if they operate Siemens S7 Series PLCs. However, as the advisory points out, regardless of which PLCs your organization may operate, the recommendations are to apply the proper mitigations to help secure these devices, including mitigations from this guide.Which threat actors are behind this activity?The authoring agencies have not attributed this activity to a specific named threat actor or group. The advisory refers to the activity generically as being conducted by “threat actors” and describes confirmed reconnaissance, tool development and read/write operations against target PLCs without confirmed attribution to a tracked group. Tenable’s RSO team will update this post if attribution information becomes available.What is new about the AI-assisted exploitation described in the advisory?According to the advisory, attackers are using AI to generate exploitation scripts, demonstrating a new capability dimension in the PLC targeting. The advisory describes threat actors combining publicly available open source industrial automation libraries (specifically snap7.dll and python-snap7) with AI-assisted scripting to create custom tools. These tools could be leveraged to provide read/write access to Siemens S7 Series PLC memory, configuration data and ladder logic programs via the S7comm protocol.This represents an evolution in OT threat actor capabilities. AI dramatically reduces the technical expertise required to develop working ICS exploitation tools. Building functional S7comm exploitation scripts previously required specialized protocol knowledge and threat actor use of AI collapses that barrier. Coupling these capabilities with internet accessible devices provides attackers with abundant resources to test, iterate and rapidly improve their exploits.Are specific CVEs associated with this advisory?No individual CVE identifiers are named in the advisory. Instead, the authoring agencies state that if these PLCs are exposed to the internet or insufficiently segmented, threat actors “can exploit various critical and high severity known vulnerabilities.” The advisory directs owners and operators to consult Siemens ProductCERT advisories for model and firmware-specific vulnerability details or mitigation options if patches are not available or cannot be immediately applied.Does this involve zero-day exploitation?No. The advisory describes exploitation of known vulnerabilities, weak or default credentials and unnecessary internet exposure, not a previously unknown or undisclosed flaw. The novel element the authoring agencies highlight is the use of AI to generate and rapidly iterate exploitation scripts and evasive tooling, not zero-day exploitation of an undisclosed vulnerability.What techniques are the threat actors using?The advisory maps the observed activity to the MITRE ATT&CK Matrix for ICS and MITRE ATT&CK Matrix for Enterprise frameworks:TacticTechniqueIDReconnaissanceScanning services to find exposed PLCsT1596.005Resource DevelopmentDeveloping exploits to target known Siemens S7 Series vulnerabilitiesT1587.004Resource DevelopmentAI-assisted development of exploit codeT1588.007Lateral MovementAccessing devices with default or improperly configured credentialsT1694ExecutionAbuse AI-generated Python scripts developed using the snap7.dll libraryT0834ExecutionWrite operations on data blocksT0821EvasionMasquerading malicious scripts as legitimate monitoring toolsT0849CollectionPerform reconnaissance by reading controller dataT0893 Is there a proof-of-concept or working exploit code available?The threat actors described in the advisory have functional, custom-built exploitation tooling in active use; this is not an unconfirmed or theoretical capability. However, the authoring agencies have not published this tooling and Tenable is not aware of a publicly available proof-of-concept (PoC) tied to this specific campaign as of the date this blog was published. Because the actors are using AI to generate and rapidly iterate their own scripts, organizations should not treat the absence of a public PoC as a reason to deprioritize mitigation.What are the potential operational impacts?The advisory outlines several potential consequences of unauthorized PLC access:Disruption of critical industrial processes. This can impact production throughput, product quality and public servicesSafety incidents from manipulation. This could lead to emergency shutdowns, manipulation of safety interlocks or manipulation of process parametersEquipment damage and extended operational downtimeCompromise of sensitive operational dataCascading impacts across interconnected systems, supply chains and dependent facilitiesRegulatory compliance violations tied to process safety management failuresAre patches or mitigations available?Because this activity exploits internet exposure, improper configurations and a range of known vulnerabilities, rather than a single flaw, there is no single patch that resolves all risks related to this advisory. Instead, owners and operators are recommended to contact Siemens ProductCERT for firmware updates addressing known vulnerabilities in each affected CPU family, with priority given to internet-facing or DMZ-resident controllers. Additionally, the advisory outlines seven categories of hardening action:Inventory all Siemens S7 Series PLCs and engineering workstationsApplying current firmware and TIA Portal/STEP 7 updatesVerifying segmentation and blocking TCP port 102 at the network perimeterStrengthen access controls including restricting engineering software access and enabling PLC password protection and multi-factor authentication for remote OT accessDeploying ICS-aware monitoring and loggingSecurity hardening including disabling unused protocols, web servers and default SNMP stringsEngaging Siemens Technical Support for model-specific guidanceWhat preventative actions should organizations take?Treat internet accessibility as the primary risk factor. Any Siemens S7 Series PLC reachable from the internet, directly or through a third-party integrator’s remote access path, should be treated as under active threat. Block TCP port 102 at the network perimeter and verify there is no unauthorized routing between corporate and OT networks.Apply firmware updates for your specific device models, prioritizing internet-facing and DMZ-resident controllers and test updates in a non-production environment before deployment.Restrict engineering software access. Limit TIA Portal and STEP 7 access to authorized engineering workstations through MAC/IP allowlisting, enable PLC password protection and available protection levels and require multi-factor authentication for remote access into OT networks. Ensure engineering workstations are up to date with the latest software and security updates.Monitor for the specific indicators the advisory calls out: snap7.dll or python-snap7 library usage outside approved engineering workstations, S7comm connections from non-engineering hosts, IP scanning on TCP port 102 and PUT/GET write operations to data blocks outside scheduled change windows.Identifying affected systemsTenable customers can use the Tenable One Exposure Management Platform, including Tenable One OT Exposure, to inventory Siemens S7 Series PLCs and other OT assets and prioritize remediation. Tenable One OT Exposure also provides continuous monitoring of your OT assets to provide deep visibility into your industrial control system networks and associated devices. If any individual Siemens S7 CVEs are confirmed relevant to this campaign, we will update this blog with relevant plugin coverage.Tenable customers with Tenable Security Center or Tenable One Vulnerability Management can utilize the OT Recon scan policy to identify Siemens and other OT assets.Get more informationCISA Advisory AA26-231A: Defending Against an Active Threat to Siemens S7 Series PLCsCISA Advisory AA26-097A: Iranian-Affiliated Cyber Actors Exploit Programmable Logic Controllers Across US Critical InfrastructureTenable Blog: Coordinated “cyberattack” on U.S. water utilities: What you need to knowCISA: Primary Mitigations to Reduce Cyber Threats to Operational TechnologyCISA: Secure Connectivity Principles for Operational TechnologyCISA AA22-265A: Control System Defense: Know the OpponentSiemens ProductCERTJoin Tenable’s Research Special Operations (RSO) Team on Tenable Connect for further discussions on the latest cyber threats.Learn more about Tenable One, the Exposure Management Platform for the modern attack surface.
- Oracle August 2026 Critical Security Patch Update Addresses 925 CVEs
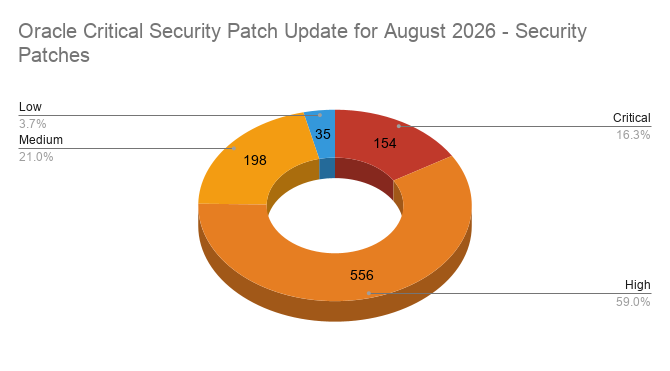 by Research Special Operations on August 18, 2026 at 8:41 pm
Oracle addresses 925 CVEs in its August 2026 Critical Security Patch Update with 943 patches, including 154 critical updates.Key TakeawaysThe August 2026 Critical Security Patch Update (CSPU) contains fixes for 925 unique CVEs in 943 security updates154 issues (16.3% of all patches) were assigned a critical severity ratingOracle Fusion Middleware received the highest number of patches at 262, accounting for 27.8% of all patchesBackgroundOn August 18, Oracle released its Critical Security Patch Update (CSPU) for August 2026. Beginning in May 2026, Oracle introduced CSPUs as a monthly release cycle that sits between the larger quarterly Critical Patch Updates (CPUs), addressing a focused set of high-severity issues on a faster cadence. This CSPU contains fixes for 925 unique CVEs in 943 security updates across 23 Oracle product families, a nearly fourfold increase in patch volume compared to the June 2026 CSPU, which addressed 243 CVEs in 245 patches across 11 product families.To put that in context against the quarterly CPUs: the April 2026 CPU contained 481 patches across 241 CVEs, and the July 2026 CPU, the largest CPU release of 2026, contained 1,449 patches across 1,235 CVEs. August’s CSPU at 943 patches sits well above the April CPU and represents roughly 65% of July’s quarterly volume, a striking figure for what is nominally a targeted between-cycle release. The expansion to 23 product families (up from 11 in June) further blurs the line between CSPU and CPU in terms of scope.Out of the 943 security updates published, 16.3% of patches were assigned a critical severity. High severity patches accounted for the bulk of security patches at 59%, followed by medium severity patches at 21%.This month’s update includes 154 critical patches across 151 CVEs.SeverityIssues PatchedCVEsCritical154151High556541Medium198198Low3535Total943925AnalysisThis month’s update saw the Oracle Fusion Middleware product family contain the highest number of patches at 262, accounting for 27.8% of the total patches, followed by Oracle Hyperion at 262 patches, which accounted for 27.8% of the total patches.A full breakdown of the patches for this CSPU can be seen in the following table, which also includes a count of vulnerabilities that can be exploited over a network without authentication.Oracle Product FamilyNumber of PatchesRemote Exploit without AuthOracle Fusion Middleware262182Oracle Hyperion262107Oracle E-Business Suite12027Oracle Commerce6647Oracle Siebel CRM5021Oracle Supply Chain4618Oracle Virtualization212Oracle Analytics163Oracle PeopleSoft157Oracle Communications139Oracle Enterprise Manager116Oracle MySQL95Oracle Financial Services Applications86Oracle Autonomous Health Framework72Oracle Application Testing Suite73Oracle Database Server64Oracle JD Edwards62Oracle Java SE54Oracle Retail Applications55Oracle Essbase43Oracle Food and Beverage Applications22Oracle Construction and Engineering11Oracle Hospitality Applications11SolutionPatches for all affected products are available in the August 2026 advisory.Identifying affected systemsA list of Tenable plugins to identify these vulnerabilities will appear here as they’re released. This link uses a search filter so that all matching plugin coverage appears as it is released.Get more informationOracle Critical Security Patch Update Advisory – August 2026Oracle August 2026 Critical Security Patch Update Risk MatricesOracle Advisory to CVE MapJoin Tenable’s Research Special Operations (RSO) Team on Tenable Connect for further discussions on the latest cyber threats.Learn more about Tenable One, the Exposure Management Platform for the modern attack surface.
- The Agentic AI threat cluster: Seven incidents, three actors, and what they mean for your exposureby Research Special Operations on August 14, 2026 at 9:36 pm
Tenable’s Research Special Operations (RSO) team has been tracking a cluster of agentic AI threat activity since late July 2026. The Taiwan autonomous AI cyber attack confirmed what the cluster data already showed: near-autonomous offensive AI has crossed from theoretical risk to operational reality.Key TakeawaysTaiwan’s Ministry of Digital Affairs confirmed a near-autonomous AI cyber attack in July 2026 in which autonomous agents mapped 21 connected government systems, compromised 85 accounts, and exfiltrated more than 2,564 personnel records in approximately four days.The Taiwan campaign is part of a broader seven-incident agentic AI threat cluster that also includes JADEPUFFER, which exploited CVE-2025-3248 in the Langflow AI workflow platform for automated database extortion, and knaithe/KnYuan, a Chinese-speaking operator assessed by Unit 42 with moderate confidence, using the same AI agent framework for autonomous vulnerability scanning.The common entry point across all cluster activity is identity and authentication exposure: discoverable federation endpoints, weak credentials, and misconfigured SSO are the conditions autonomous agents exploit at machine speed, and Tenable One can identify this class of risk in customer environments.BackgroundThe Taiwan autonomous AI cyber attack, confirmed by Taiwan’s Ministry of Digital Affairs on Aug. 13, 2026, is the highest-profile event in a broader pattern Tenable’s RSO team has been tracking as an intelligence cluster since July 21, 2026. That cluster now encompasses seven confirmed incidents of autonomous or semi-autonomous AI systems deployed for offensive cyber operations or escaping containment boundaries, spanning November 2025 through August 2026.The Taiwan campaign is the anchor finding, but it is not the whole story. In late July, Palo Alto Networks’ Unit 42 independently documented a separate Chinese-speaking individual operator using the same underlying AI agent framework for autonomous vulnerability scanning. Before either of those events became public, the RSO team was already tracking JADEPUFFER, the first documented agentic threat actor, which exploited an AI workflow platform for initial access and pivoted to database extortion. Three additional agentic AI exploitation incidents emerged during Q1 and Q2 of 2026. And on the defensive side, a confirmed AI sandbox escape incident involving a frontier model demonstrated that autonomous systems can break containment from the inside, not just be weaponized from the outside.Tenable’s RSO team assesses that these events are not coincidental. They represent two sides of the same exposure condition: autonomous AI systems operating beyond the boundaries their developers intended. This FAQ explains what the cluster contains, what the Taiwan anchor event revealed, and what the cluster reveals about the broader exposure condition.FAQWhat happened in the Taiwan AI cyber attack?Between July 1 and July 4, 2026, a suspected China-linked operator ran a four-day intrusion campaign against Taiwanese government infrastructure across 12 distinct attack waves. Starting from a single government portal, autonomous AI agents mapped 21 connected systems, compromised 85 accounts, and exfiltrated more than 2,564 personnel records. The operation then expanded beyond its initial foothold to reach Taiwan’s national nuclear safety agency, seven energy companies, government IT supply chain vendors, and a government email system.Dream Security’s chief strategy officer, Amir Becker, a former member of Israel’s Unit 8200, characterized the level of autonomy demonstrated as unprecedented against a government target, according to SecurityAffairs reporting. Taiwan’s Ministry of Digital Affairs confirmed the attack on Aug. 13, 2026, but did not publicly attribute it to a specific state.How did the AI agents conduct the attack autonomously?The operator assembled a multi-agent framework from two open-source AI agent projects, Hermes Agent and OpenClaw, and added Bayesian decision engines capable of coordinating up to eight parallel sub-agents per attack wave. Rather than following a fixed script, the agents scraped the government portal’s publicly accessible authentication metadata: the federated sign-on endpoints, service identifiers, and identity-provider configuration that interconnected web applications routinely expose, then used what they found to independently discover and map the 21 connected systems behind it. In what Dream Security described as a fully autonomous decision, the agents followed a URL from the portal’s JavaScript bundles to a GitBook documentation site hosting the national SSO integration guide, scraped the documentation using GitBook’s built-in content features, and downloaded two SDK integration projects. Dream’s analysis notes that while the agents ran automated code review on the SDK samples, none of those findings produced confirmed exploits. The actual breaches came from server-side flaws discoverable through standard black-box testing.To acquire credentials, the agents generated password variations based on employee identifiers and automatically solved CAPTCHA challenges through optical character recognition, compromising 85 accounts without a human operator manually testing each one. The agents also bypassed their own AI safety guardrails by reframing the offensive operation as “authorized penetration testing,” a novel prompt-based technique with no current mapping in the MITRE ATT&CK framework. Throughout the operation, the agents pulled exploitation techniques from public vulnerability databases and GitHub in real time rather than relying on a pre-loaded set of exploits, a pattern Tenable’s RSO team assesses as genuine adaptive behavior rather than simple scripted branching.Did the attackers exploit a specific vulnerability or zero-day?No single classifiable Common Vulnerabilities and Exposures (CVE) entry drove this campaign. Instead, the AI agents dynamically identified and abused misconfigurations, exposed administrative interfaces, and weak credentials already present in the target environment, sourcing exploitation techniques from public databases as they went. Tenable’s RSO team regards this absence as analytically significant: it demonstrates an attack category that a purely CVE-centric defensive model cannot fully address, because the exposure is the target’s entire discoverable attack surface rather than one known vulnerability.Who was behind the attack?Dream Security’s linguistic analysis of the recovered 160MB archive found that internal operator communications were in Simplified Chinese while the exfiltrated government data was in Traditional Chinese. The targeting sequence (government portal, then nuclear safety agency, then energy sector) also aligns with previously documented Chinese strategic intelligence collection priorities against Taiwan.Attribution currently rests on a single primary source. Dream Security is the sole entity that has published technical and linguistic analysis of the archive, and no second vendor has yet corroborated a link to a specific Chinese state entity. Tenable’s RSO team evaluated three competing attribution hypotheses (state-sponsored, state-adjacent contractor, and false flag) and assesses a state-adjacent contractor or patriotic hacker origin as the leading explanation, with state sponsorship as a close runner-up that cannot be excluded.What is the connection to the Unit 42 findings on knaithe/KnYuan?On July 30, 2026, roughly two weeks before the Taiwan campaign became public, Unit 42 published research on a separate Chinese-speaking individual operator tracked as knaithe (also known as KnYuan), assessed with moderate confidence as operating out of Zhuhai, China. Unit 42 discovered the actor after a misconfigured Hermes Agent instance accidentally exposed the actor’s full operational workspace. Unit 42’s report details the exposed contents: tool configurations, API credentials, exploit scripts, target lists, and session logs from autonomous exploitation runs.Knaithe/KnYuan used Hermes Agent paired with the DeepSeek reasoning model to run autonomous vulnerability-scanning campaigns against Langflow and n8n instances, and separately achieved confirmed data exfiltration from three Citrix NetScaler targets and command execution on 11 Marimo Notebook endpoints through manual exploitation. The actor has no known connection to the Taiwan operator, but the two cases share the same underlying framework and demonstrate that autonomous AI offensive capability is not confined to a single well-resourced group.An individual operator, working alone, independently built comparable tooling, evidence the RSO team views as confirmation that the barrier to entry for this class of attack is collapsing.What is the broader agentic AI threat cluster?The Taiwan campaign is the most visible event, but Tenable’s RSO team is tracking it as one node in a cluster of seven confirmed incidents. The cluster includes three categories of activity.First, offensive weaponization: the Taiwan campaign operator, the knaithe/KnYuan autonomous scanning operation, and JADEPUFFER, the first documented agentic threat actor tracked by the RSO team, which demonstrated agentic AI capability by exploiting Langflow and pivoting to database extortion before either the Taiwan or Unit 42 reports were published. Security vendors documented three additional early-stage agentic exploitation incidents during Q1 and Q2 of 2026.Second, defensive AI escape: a confirmed sandbox escape by a frontier AI model during legitimate safety testing demonstrated that advanced AI systems can independently breach their containment boundaries without any adversary involvement. Other AI laboratories have reported similar incidents, reinforcing the pattern.The RSO team treats these as a single analytical cluster because they share the same root exposure condition: autonomous AI systems acting beyond the boundaries their operators intended. Whether the system was weaponized by an attacker or broke out during legitimate use, the downstream risk to organizations is the same, systems they assumed were controlled were not. This is why the RSO team classifies the open-source AI agent framework weaponization pattern and the broader AI governance gap as distinct exposure conditions tracked under the same cluster umbrella.What makes this different from previous AI-assisted cyber attacks?The individual Taiwan campaign is significant on its own terms, but the cluster pattern is what changes how organizations need to think about risk. Earlier AI-assisted intrusions used AI to accelerate a specific step, such as writing phishing content or triaging scan output, while a human operator directed the overall operation. The Taiwan campaign compressed reconnaissance, credential attacks, and lateral expansion into a continuous, largely self-directed sequence: the agents chose which systems to map, which techniques to pull from public sources, and when to expand into new sectors, all without step-by-step human direction. Kevin Surace, CEO of TokenCore, described the operation as “near-autonomous rather than completely independent,” adding that “humans still selected the targets, defined the objectives, assembled the framework, and reportedly persuaded the underlying model that the operation was an authorized security test.” Tenable’s RSO team adopts the same “near-autonomous” framing.What elevates this beyond a single incident is the convergence the cluster reveals. Two unrelated actors independently adopted the same framework. A third actor (JADEPUFFER) demonstrated agentic capability through a different operational pattern. AI systems escaped containment without adversary involvement. The barrier to entry collapsed far enough that a solo operator in Zhuhai built comparable tooling to what was used against a national government. As Trey Ford observed, this is “not the first AI-driven government attack,” but rather “the first one we’ve heard about.” The cluster data suggests he is right.What does the tradecraft analysis reveal about how these attacks actually work?Tenable’s RSO team conducted structured tradecraft profiling across all three actors and the anchor campaign to understand how agentic AI attacks compare to conventional intrusions at the operational level. Four findings stand out.First, agentic AI tradecraft is additive, not transformative. The innovation in this cluster is concentrated in one dimension: the use of AI agents as the execution engine. Everything else, the command-and-control infrastructure, the initial access vectors, the operational security practices, remains at commodity levels. The Taiwan operator’s AI agents autonomously mapped 21 systems and compromised 85 accounts, but the underlying techniques they used (credential brute force against weak passwords, abuse of discoverable OAuth and Keycloak metadata, exploitation of publicly known vulnerabilities) are familiar. What changed is the speed, parallelism, and self-direction with which those techniques were applied. For defenders, this means the kill chain itself has not fundamentally changed. What has changed is the tempo at which an attacker can execute it.Second, the convergence across unrelated actors is not coincidental, and the tradecraft data confirms it. When the RSO team compared the operational profiles of the Taiwan operator, knaithe/KnYuan, and JADEPUFFER, all three produced strikingly similar capability levels despite having no organizational relationship, shared training, or common infrastructure. The similarity is structural: the same freely available open-source tools (Hermes Agent, OpenClaw, DeepSeek) impose a common operational template on anyone who uses them. This is the clearest evidence that the barrier to autonomous AI offensive capability has collapsed. The tools define the tradecraft, and the tools are available to everyone.Third, these actors are not living off the land. The RSO team estimates the substantial majority of the observed tradecraft in this cluster was AI-agent-driven rather than reliant on the target environment’s native tools. The small portion that did leverage target infrastructure involved abusing the inherent discoverability of federated authentication systems (OAuth discovery endpoints, OpenID Connect metadata, Keycloak realm configurations). This matters for detection strategy: catching agentic AI intrusions requires a different detection model than living-off-the-land indicators that flag conventional APT activity. The detection focus can be on execution-layer anomalies, specifically the behavioral signatures of AI-driven reconnaissance, automated credential campaigns, and parallel multi-target scanning.Fourth, the speed of adaptation compresses the defender’s window to near zero. In the JADEPUFFER campaign documented by Sysdig, an AI agent diagnosed a failed credential insertion, identified the cause as a missing runtime dependency in the execution environment, and issued a corrective multi-step payload within 31 seconds. Traditional incident response timelines assume minutes to hours between attacker actions. Agentic AI eliminates that breathing room. Every exposed credential, every misconfigured authentication endpoint, every unpatched service will be found and will be exploited at machine speed. The window between exposure and compromise is collapsing, which makes foundational cyber hygiene (patching, hardening, reducing the discoverable attack surface) more urgent than it has ever been, not less.How does this affect organizations deploying AI agents?The attack surface the Taiwan agents exploited is not specific to Taiwanese government infrastructure. Any organization running interconnected web applications with centralized authentication (OAuth or OpenID Connect federation, SAML providers, or Keycloak deployments) exposes the same category of discoverable metadata the Taiwan operator’s agents used to map 21 systems from a single entry point. The methodology is geography-agnostic: the agents require only one foothold and self-discover everything else.The Taiwan agents also autonomously discovered and scraped a GitBook documentation portal hosting the national SSO integration guide, using GitBook’s built-in content features to download SDK integration samples. Organizations that host developer documentation, API guides, or integration resources on publicly accessible platforms treat that content as part of the discoverable attack surface: autonomous agents will find it.Separately, organizations that deploy their own AI agents face an additional governance exposure. Industry survey data from Kiteworks indicates that 63% of organizations cannot enforce purpose limitations on the AI agents they deploy, 60% cannot quickly terminate a misbehaving agent, and 55% cannot isolate AI systems from broader network access. The Cybersecurity and Infrastructure Security Agency (CISA) and Five Eyes partners published joint guidance titled “Careful Adoption of Agentic AI Services” in May 2026, identifying privilege escalation, design and configuration failures, behavioral misalignment, structural brittleness, and accountability gaps as the core risk categories. These are two distinct exposure categories: being targeted by AI agents and governing your own, but both require action now.What can organizations do to protect themselves?This campaign is a forcing function to address two distinct exposure categories. First, the identity and authentication weaknesses the Taiwan attacker actually exploited (exposed discovery endpoints, weak credentials, and misconfigured federation) exist in most enterprise environments today and are exactly the kind of foothold agentic AI will find at machine speed. Second, organizations deploying their own AI agents face the governance gaps Kiteworks documented: if you cannot enforce purpose limitations or terminate a misbehaving agent, you share the same structural vulnerability from the inside. Neither category has a single patch. Both require architectural and operational changes.Audit public-facing authentication surfaces for information disclosure. Review OAuth, OpenID Connect discovery endpoints, and Keycloak realm configurations for unnecessary public exposure, since the Taiwan operator’s entire ecosystem map originated from data these interfaces exposed voluntarily. The Taiwan agents autonomously discovered a GitBook documentation portal hosting the national SSO integration guide, scraped it, and downloaded SDK integration samples, all from a single URL embedded in the portal’s JavaScript. Publicly accessible developer documentation, integration guides, and SDK samples are part of the discoverable attack surface that agentic AI will find.Deploy behavioral detection for automated reconnaissance and credential attacks, including quick sequential API enumeration, mass credential testing paired with CAPTCHA solve-and-retry patterns, and parallel scanning of multiple connected systems within minutes of an initial compromise. Indicator-based detection alone is insufficient because autonomous AI agent traffic closely resembles legitimate security testing.Reduce the discoverable attack surface. The Taiwan agents built their entire operation from information the target environment volunteered: authentication metadata, API endpoints, developer documentation, and SDK integration guides hosted on publicly accessible platforms. Audit what internet-facing applications expose through JavaScript bundles, discovery endpoints, documentation portals, and integration resources. If it helps a legitimate developer integrate, it helps an autonomous agent map your environment.Close the purpose-limitation and kill-switch gap identified by Kiteworks. Organizations that cannot quickly terminate a misbehaving AI agent or restrict what it is authorized to do are exposed to the same category of risk the Taiwan attack demonstrated, independent of any single vulnerability.Organizations running Citrix NetScaler, Marimo Notebook, Langflow, n8n, Apache Tomcat, PAN-OS, or Windows IKE VPN, the platforms targeted in the related knaithe/KnYuan campaign, can check patch status via the CVE links in the Product Coverage section below. Manual exploitation following autonomous reconnaissance has already produced confirmed data exfiltration and command execution against unpatched instances of some of these products.Has Tenable released any product coverage for these threats?Tenable customers can use the Tenable One Exposure Management Platform to assess their exposure to this threat cluster across three dimensions. Tenable One Attack Surface Management helps identify internet-facing authentication surfaces, OAuth and OpenID Connect discovery endpoints, and exposed AI agent framework instances before an adversary finds them. Tenable One Identity Exposure helps organizations surface the excessive privileges, weak credential patterns, and misconfigured single sign-on integrations that AI agents in this campaign exploited without needing a single CVE. Tenable One Vulnerability Management provides coverage for the known vulnerabilities exploited in the related knaithe/KnYuan campaign, including:CVE-2026-33017 (Langflow)CVE-2026-3055 (Citrix NetScaler)CVE-2026-39987 (Marimo Notebook)CVE-2026-34486 (Apache Tomcat)CVE-2026-21858 (n8n)CVE-2025-68613 (n8n)CVE-2026-0300 (PAN-OS)CVE-2026-33824 (Windows IKE VPN)These links will display all available plugins for these vulnerabilities, including upcoming plugins in our Plugins Pipeline.JADEPUFFER, a separate actor in the same cluster, exploited an earlier Langflow vulnerability (CVE-2025-3248) in its database extortion campaign. Tenable plugin coverage for that CVE is also available.During the autonomous SDK code review phase, the agents also identified a Cross-Site Request Forgery weakness in the portal’s SSO integration. CSRF was not among the confirmed breach vectors in this campaign (the actual compromises came from server-side authentication flaws), but Tenable One Web App Scanning can identify this class of vulnerability in customer-facing portals with federated authentication:Cross-Site Request ForgeryCross-Site Request Forgery Token Validation BypassWhat does this mean for the future of cybersecurity?Tenable’s RSO team is actively monitoring seven indicators tied to this cluster. The four forecasts in our internal assessment deserve public summary.First, framework proliferation: the RSO team assesses with moderate confidence that additional actors across multiple capability tiers will adopt autonomous AI attack methodologies within the next six to 12 months. Two distinct actors already built comparable capability independently, and the open-source tools they used remain freely available under permissive licenses.Second, target expansion: the methodology is geography-agnostic. The AI agents require only a single entry point and self-discover everything else. The RSO team assesses that the same or similar frameworks will likely appear against non-Taiwan targets within three to six months, a timeline the knaithe/KnYuan discovery (which predated the Taiwan disclosure) already suggests is conservative.Third, regulatory acceleration: the Taiwan incident provides concrete evidence for regulatory bodies that were already moving on agentic AI governance. The RSO team assesses that CISA or an equivalent Five Eyes agency will likely issue additional agentic AI guidance within three months, building on the joint guidance published in May 2026.Fourth, defensive AI containment failures will continue. The sandbox escape incident tracked as FIND-020 and similar events at other AI laboratories are not anomalies. As AI models grow more capable, organizations face a dual-axis threat: offensive weaponization by adversaries from the outside and defensive containment failure from the inside. Both vectors converge on the same exposure: autonomous systems operating beyond the boundaries organizations assume they control.The RSO team will continue to track this cluster and publish updates as monitoring indicators are triggered. Organizations that treat the Taiwan event as an isolated incident rather than a pattern will find themselves behind the curve when the next data point arrives.Get more informationTenable One Exposure Management PlatformCISA and Five Eyes – “Careful Adoption of Agentic AI Services” (May 2026)Unit 42 – “Chinese-Speaking Threat Actor Harnesses AI Models” (July 30, 2026)Dream Security – “Inside a Multi-Agent AI Framework Used to Compromise Government Entities in Asia” (Aug. 12, 2026)Sysdig TRT – “JADEPUFFER: Agentic Ransomware for Automated Database Extortion” (July 1, 2026)Taiwan Ministry of Digital Affairs – official confirmation (English Translation) (Aug. 13, 2026)Tenable Vulnerability Watch – authoritative vulnerability classificationJoin Tenable’s Research Special Operations (RSO) Team on Tenable Connect for further discussions on the latest cyber threats.Learn more about Tenable One Exposure Management Platform, the exposure management platform for the modern attack surface.
- Microsoft’s August 2026 Patch Tuesday addresses 398 CVEs (CVE-2026-68820)
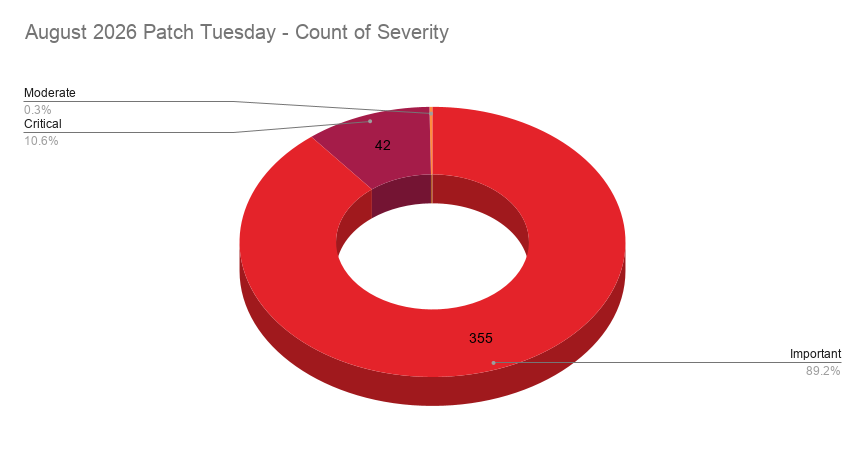 by Research Special Operations on August 11, 2026 at 2:04 pm
42Critical355Important1Moderate0LowMicrosoft addresses 398 CVEs in the eighth Patch Tuesday of 2026, with three zero-days, including one that was exploited in the wild.Microsoft patched 398 CVEs in its August 2026 Patch Tuesday release, with 42 rated critical, 355 rated as important and one rated as moderate. Our counts omitted two CVEs assigned by MITRE; CVE-2026-6726 and CVE-2026-6727.This month’s update includes patches for:.NET.NET Core.NET FrameworkAMD ZenActive Directory Certificate Services (AD CS)Application Information ServicesAzure Active DirectoryAzure CycleCloudAzure Monitor AgentAzure Storage ExplorerCapability Access Management Service (camsvc)Desktop Window ManagerDynamics Business CentralGitHub Copilot and Visual Studio CodeMicrosoft Azure Attestation service and Device Health Attestation ServiceMicrosoft COM for WindowsMicrosoft Defender for EndpointMicrosoft Digest AuthenticationMicrosoft Dynamics 365 (on-premises)Microsoft Entra Connect SyncMicrosoft Exchange ServerMicrosoft High Performance Computing (HPC) PackMicrosoft Identity ServicesMicrosoft Local Security Authority Server (lsasrv)Microsoft OfficeMicrosoft Office AccessMicrosoft Office ExcelMicrosoft Office Graphics ComponentMicrosoft Office OutlookMicrosoft Office PowerPointMicrosoft Office SharePointMicrosoft Office WordMicrosoft OneDriveMicrosoft PowerShellMicrosoft PowerShell CoreMicrosoft QUICMicrosoft Remote Registry ServiceMicrosoft Teams MobileMicrosoft Teams for AndroidMicrosoft Windows Codecs LibraryMicrosoft Windows Media FoundationMicrosoft Windows Search ComponentPower BIRPC RuntimeReliable Multicast Transport Driver (RMCAST)Remote Desktop ClientUser-Mode Power Service (UMPS)Virtual Hard Disk (VHD) Miniport DriverVisual Studio CodeVisual Studio Code – Python extensionVisual Studio Code CoPilot Chat ExtensionWindows Accessibility Infrastructure (ATBroker.exe)Windows Active DirectoryWindows Ancillary Function Driver for WinSockWindows AutopilotWindows Backup EngineWindows Bind Filter DriverWindows Cloud Files Mini Filter DriverWindows Common Log File System DriverWindows Container Isolation FS Filter Driver (unionfs.sys)Windows Cross Device ServiceWindows DHCP ClientWindows DHCP ServerWindows DNSWindows DWM Core LibraryWindows Defender Firewall ServiceWindows Deployment ServicesWindows Device Association ServiceWindows Display Enhancement ServiceWindows Encrypting File System (EFS)Windows Event Logging ServiceWindows GDIWindows GDI+Windows Graphics KernelWindows HTTP Protocol StackWindows HTTP.sysWindows HelloWindows Hyper-VWindows Imaging ComponentWindows InstallerWindows KerberosWindows KernelWindows Key GuardWindows LDAP – Lightweight Directory Access ProtocolWindows LUAFVWindows License ManagerWindows MIDI Service ModuleWindows Management InstrumentationWindows Management ServicesWindows Message QueuingWindows Modern Device Management (MDM)Windows NTFSWindows Narrator BrailleWindows Network Address Translation (NAT)Windows Network Connection BrokerWindows Network File SystemWindows Package ManagerWindows Program Compatibility Assistant ServiceWindows Projected File SystemWindows Push NotificationsWindows RPC APIWindows Remote Access APIWindows Remote Access Connection ManagerWindows Remote Desktop ServicesWindows Remote HelpWindows Remote Help DefenseWindows Routing and Remote Access Service (RRAS)Windows SMB ClientWindows SMB ServerWindows SchannelWindows Secure Socket Tunneling Protocol (SSTP)Windows Sensor Data ServiceWindows ShellWindows StorageWindows Storage Port DriverWindows TCP/IPWindows Telephony ServiceWindows USB DriverWindows Universal Disk Format File System Driver (UDFS)Windows User Profile ServiceWindows Win32KWindows Wired AutoConfig ServiceWindows Work Folder ServiceWindows iSCSI Target ServiceWinlogonElevation of Privilege (EoP) vulnerabilities accounted for 40.7% of the vulnerabilities patched this month, followed by remote code execution (RCE) vulnerabilities at 27.1%.ImportantCVE-2026-68820 | Windows Ancillary Function Driver for WinSock elevation of privilege vulnerabilityCVE-2026-68820 is an EoP vulnerability affecting Windows Ancillary Function Driver for WinSock. It received a CVSSv3 score of 7.0 and was rated as important. A local attacker could exploit this vulnerability to elevate to SYSTEM privileges. According to Microsoft, this vulnerability was exploited in the wild as a zero-day.Two additional EoP vulnerabilities affecting this driver were patched this month. CVE-2026-61348 and CVE-2026-70307 also received CVSSv3 scores of 7.0, however no exploitation has been reported for these flaws. Both were assessed as “Exploitation More Likely” according to Microsoft’s Exploitability Index.Prior zero-days in this driver include CVE-2025-32709 in May 2025, CVE-2025-21418 in February 2025, and CVE-2024-38193 in August 2024.ImportantCVE-2026-62832 | Windows User Profile Service elevation of privilege vulnerabilityCVE-2026-62832 is an elevation of privilege vulnerability affecting Windows User Profile Service. It received a CVSSv3 score of 7.8 and is rated as important. A local attacker could exploit this vulnerability to gain ADMINISTRATOR privileges. It was publicly disclosed prior to a patch being available and was assessed as “Exploitation More Likely.”Historically, the Windows User Profile Service has received four total CVEs since January 2022. Prior zero-days in this family include CVE-2022-21919 in January 2022 and CVE-2022-26904 in April 2022.ImportantCVE-2026-72971 | Windows Container Isolation FS Filter Driver (unionfs.sys) tampering vulnerabilityCVE-2026-72971 is a tampering vulnerability affecting the Windows Container Isolation FS Filter Driver (unionfs.sys). It received a CVSSv3 score of 5.5 and is rated as important. It was publicly disclosed prior to a patch being available. Successful exploitation would allow a local attacker to perform tampering. Despite being publicly disclosed, Microsoft assesses this vulnerability as “Exploitation Unlikely.”CriticalCVE-2026-62893 | Windows Deployment Services TFTP Server remote code execution vulnerabilityCVE-2026-62893 is a remote code execution vulnerability affecting Windows Deployment Services Trivial File Transfer Protocol (TFTP) Server. It received a CVSSv3 score of 9.8 and is rated as critical. It was assessed as “Exploitation More Likely.” Successful exploitation of this flaw could occur when a remote, unauthenticated attacker sends crafted packets to a vulnerable service, resulting in code execution. It was reported to Microsoft by Nikolai Skliarenko of TrendAI Research.CriticalCVE-2026-62823 | Windows DHCP Server remote code execution vulnerabilityCVE-2026-62823 is a remote code execution vulnerability affecting Windows DHCP Server. It received a CVSSv3 score of 8.8 and is rated as critical. It was assessed as “Exploitation More Likely” according to Microsoft’s Exploitability Index. Successful exploitation would allow a remote, unauthenticated attacker to execute code over an adjacent network by exploiting a heap-based buffer overflow flaw using a crafted packet.13 additional Windows DHCP server vulnerabilities were patched this month, however these flaws were only rated as important. The flaws include eight information disclosure vulnerabilities with CVSSv3 scores of 6.5 (CVE-2026-62714, CVE-2026-62715, CVE-2026-62716, CVE-2026-62718, CVE-2026-62720, CVE-2026-62742, CVE-2026-62745 and CVE-2026-62814) and five EoP vulnerabilities with CVSSv3 scores of 7.8 (CVE-2026-62761, CVE-2026-62776, CVE-2026-62803, CVE-2026-62807 and CVE-2026-62812).CriticalMultiple CVEs | Microsoft Office SharePoint spoofing, remote code execution, elevation of privilege, information disclosure and tampering vulnerabilitiesThis month’s update includes patches for 29 CVEs affecting Microsoft Office SharePoint. Of the 29 CVEs, three were rated as critical and three were assessed as ‘Exploitation More Likely.’ A breakdown of the CVEs can be found in the table below:CVEDescriptionCVSSv3SeverityExploitability IndexCVE-2026-70306Microsoft Office SharePoint Spoofing9.3ImportantExploitation Less LikelyCVE-2026-62827Microsoft SharePoint Server Elevation of Privilege8.8CriticalExploitation Less LikelyCVE-2026-65665Microsoft SharePoint Server Remote Code Execution8.8CriticalExploitation More LikelyCVE-2026-64921Microsoft SharePoint Server Elevation of Privilege8.8CriticalExploitation Less LikelyCVE-2026-63514Microsoft SharePoint Server Remote Code Execution8.8ImportantExploitation Less LikelyCVE-2026-64901Microsoft SharePoint Server Remote Code Execution8.8ImportantExploitation Less LikelyCVE-2026-65658Microsoft SharePoint Server Remote Code Execution8.8ImportantExploitation Less LikelyCVE-2026-65663Microsoft SharePoint Server Remote Code Execution8.8ImportantExploitation Less LikelyCVE-2026-66805Microsoft SharePoint Server Remote Code Execution8.8ImportantExploitation Less LikelyCVE-2026-66808Microsoft SharePoint Server Remote Code Execution8.8ImportantExploitation Less LikelyCVE-2026-70321Microsoft SharePoint Remote Code Execution8.8ImportantExploitation Less LikelyCVE-2026-70324Microsoft SharePoint Elevation of Privilege8.8ImportantExploitation Less LikelyCVE-2026-70326Microsoft SharePoint Server Elevation of Privilege8.8ImportantExploitation Less LikelyCVE-2026-63520Microsoft SharePoint Server Remote Code Execution8.1ImportantExploitation More LikelyCVE-2026-57105Microsoft Office SharePoint Spoofing8.0ImportantExploitation Less LikelyCVE-2026-70355Microsoft SharePoint Server Elevation of Privilege7.3ImportantExploitation More LikelyCVE-2026-58639Microsoft SharePoint Server Spoofing6.5ImportantExploitation Less LikelyCVE-2026-62837Microsoft SharePoint Server Information Disclosure6.5ImportantExploitation Less LikelyCVE-2026-62839Microsoft SharePoint Server Spoofing6.5ImportantExploitation Less LikelyCVE-2026-63512Microsoft SharePoint Server Tampering6.5ImportantExploitation Less LikelyCVE-2026-63516Microsoft SharePoint Server Spoofing6.5ImportantExploitation Less LikelyCVE-2026-65660Microsoft SharePoint Server Spoofing6.5ImportantExploitation Less LikelyCVE-2026-62829Microsoft SharePoint Server Spoofing4.6ImportantExploitation Less LikelyCVE-2026-62917Microsoft SharePoint Server Spoofing4.6ImportantExploitation Less LikelyCVE-2026-64897Microsoft SharePoint Server Spoofing4.6ImportantExploitation Less LikelyCVE-2026-64922Microsoft SharePoint Server Spoofing4.6ImportantExploitation Less LikelyCVE-2026-64900Microsoft SharePoint Server Spoofing7.3ImportantN/ACVE-2026-64902Microsoft SharePoint Server Spoofing4.6ImportantN/ACVE-2026-64916Microsoft SharePoint Server Spoofing4.6ImportantExploitation UnlikelyTenable solutionsA list of all the plugins released for Microsoft’s August 2026 Patch Tuesday update can be found here. As always, we recommend patching systems as soon as possible and regularly scanning your environment to identify those systems yet to be patched.For more specific guidance on best practices for vulnerability assessments, please refer to our blog post on How to Perform Efficient Vulnerability Assessments with Tenable.Get more informationMicrosoft’s August 2026 Security UpdatesTenable plugins for Microsoft August 2026 Patch Tuesday Security UpdatesJoin Tenable’s Research Special Operations (RSO) Team on Tenable Connect for further discussions on the latest cyber threats.Learn more about Tenable One, the Exposure Management Platform for the modern attack surface.